REDSHADES · INVESTOR TECHNICAL EDITION / 2026

Put models to work.
Keep software in control.

Long technical investigations ask more of a system than a good answer. RedShades gives smaller, specialized models defined decisions while deterministic software owns scheduling, evidence, policy and recovery. A native workspace brings those decisions, their sources and the tools behind them into view.

Smaller specialists.
Persistent engineering sessions.
One accountable workflow.
Put models to work.
Keep software in control. — operator workspace
Keep source notes, context and investigation progress together.
RedShades / engineered intelligence

Software carries the workflow

Implemented

The next step is a software decision

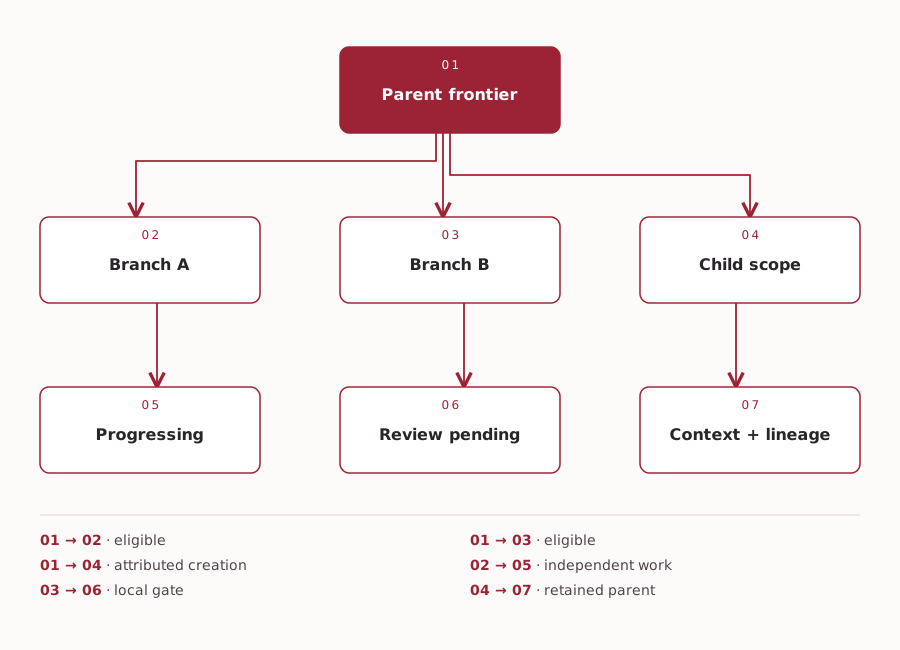
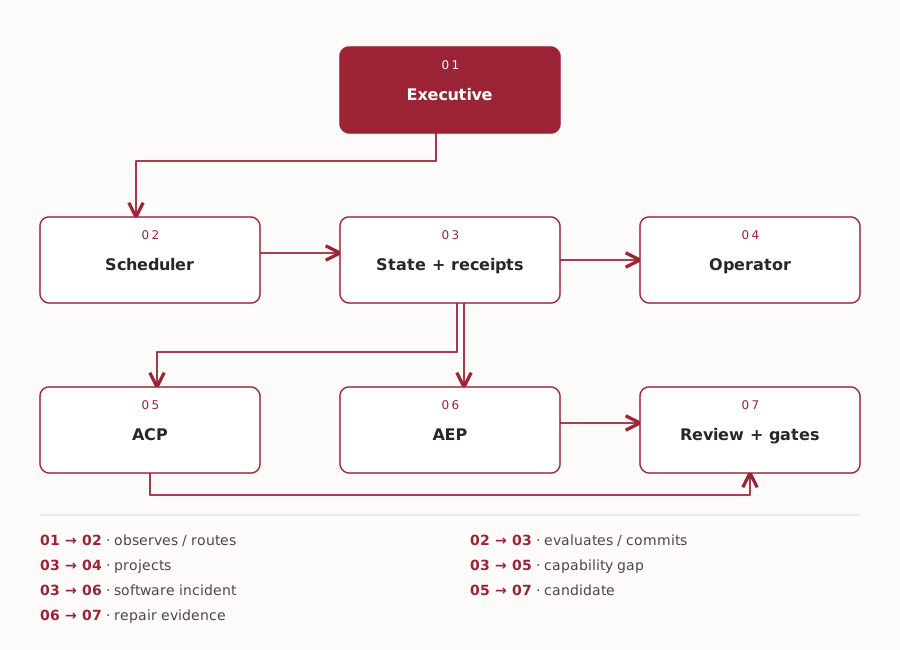
Each stage declares the evidence it needs. The scheduler advances eligible branches and revisits waiting work when observations change. Models interpret uncertain inputs; they do not have to reconstruct the workflow or remember which branch can run.

Evidence-driven scheduling

The Executive supervises progress. Capability development and software repair have separate owners, so a stalled investigation can be routed to the appropriate kind of work. Child investigations retain their scope, parent context and completion relationship.

Implemented
Evidence-driven scheduling — source-derived relationship diagram
Evidence-driven scheduling · overview.
Design philosophy

Spend intelligence on the uncertain part

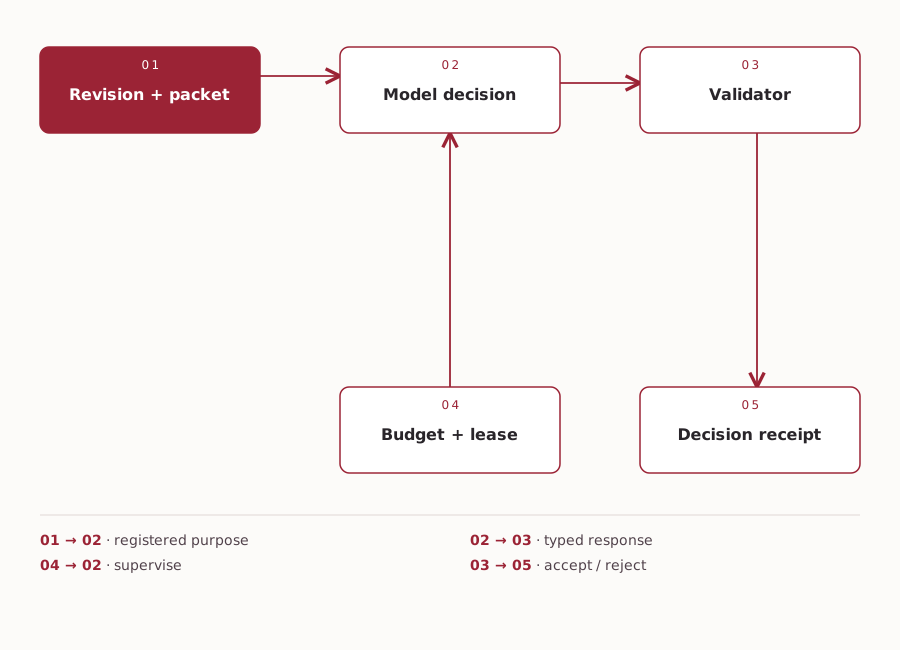
Scheduling, state, policy and validation are software responsibilities. Interpretation and synthesis are model responsibilities. That division gives a small specialist a complete, bounded job instead of asking it to manage an entire engagement.

Model allocation

The 70% deterministic / 30% neural framing describes the design philosophy. It is not a measured share of code, runtime or success. Model economics remain a question for controlled evaluation.

Design philosophy
Model allocation — source-derived relationship diagram
Model allocation · overview.
Adaptive orchestration

Progress worth keeping

Implemented

Memory belongs to the engagement

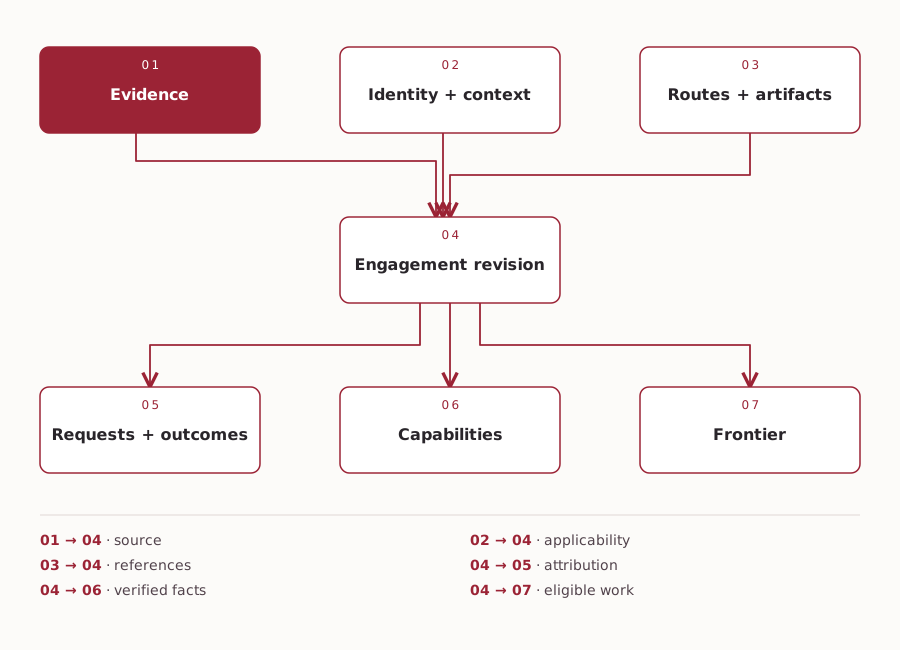
Versioned records link observations, identities, routes, artifacts and outcomes. A new model session or replacement worker can read the accepted state and its sources without rebuilding the investigation from a conversation.

Shared engagement state

The scheduler and native views draw on the same records. Revision references identify the inputs behind a decision; they also make stale results distinguishable from current work.

Implemented
Shared engagement state — source-derived relationship diagram
Shared engagement state · overview.
Implemented

A finding should lead back to its source

A tool result retains its source, context and interpretation. Later stages can reuse it, and an operator can inspect what actually supported a conclusion. Competing observations remain distinguishable until there is evidence to resolve them.

Evidence attribution

Attribution is the connection between tool integration and model quality: a specialist receives inspectable material with context, rather than an untraceable summary.

Implemented
A finding should lead back to its source — operator workspace
Inspect the source records supporting the selected finding.
Implemented

A repertoire, selected by evidence

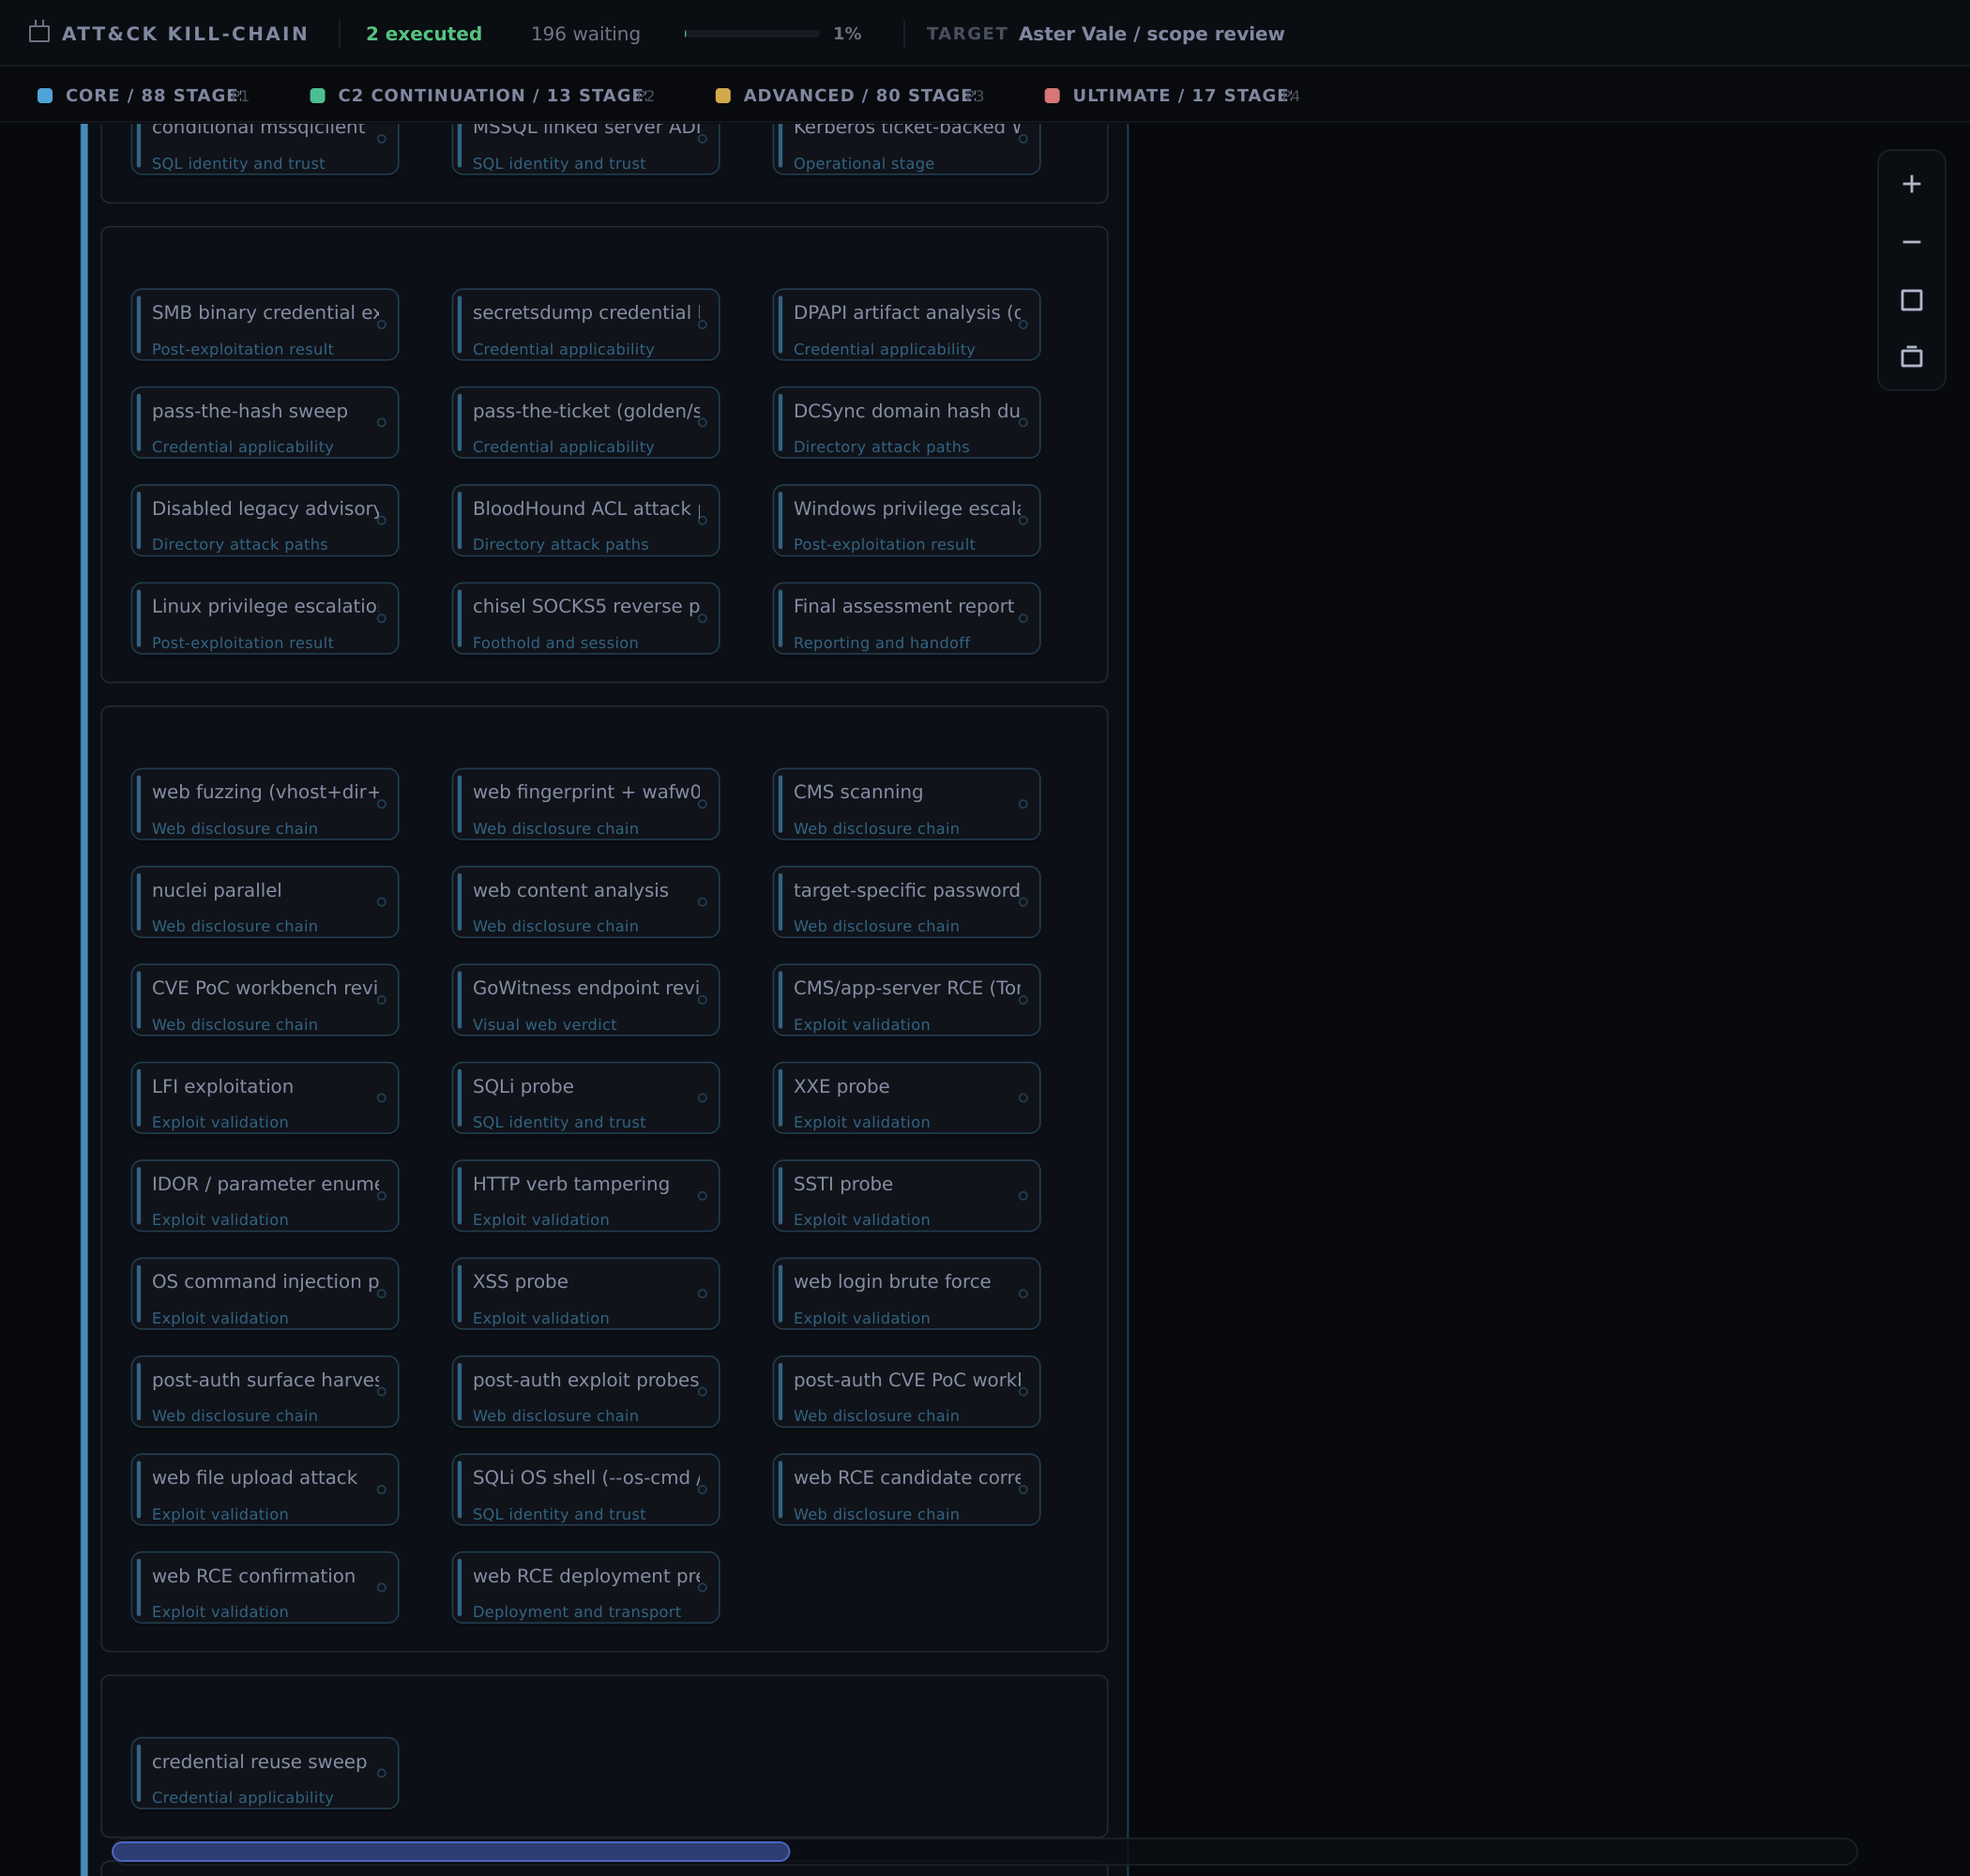
The Validated Core contains 88 conditional stages spanning discovery, service and identity analysis, web investigation, artifacts and reporting. Thirteen C2 continuation stages add shared and platform-specific session work.

Conditional stage coverage

Prerequisites, platform context and policy determine the path. The atlas identifies the available responsibilities; its order does not prescribe an execution sequence.

Implemented
A repertoire, selected by evidence — operator workspace
Web investigation within the 198-stage repertoire.
Implemented

A local question need not stop the run

An endpoint review or missing identity fact can hold one branch while unrelated work continues. A global pause is an explicit operator decision with a different scope.

Branch-local progress

Waiting work retains the input that could make it eligible. New observations can reopen useful branches without turning every unresolved item into a retry loop.

Implemented
Branch-local progress — source-derived relationship diagram
Branch-local progress · overview.
Models, ACP and specialist intelligence

Give each model the right job

Core model entitlement

A complete job for a specialist

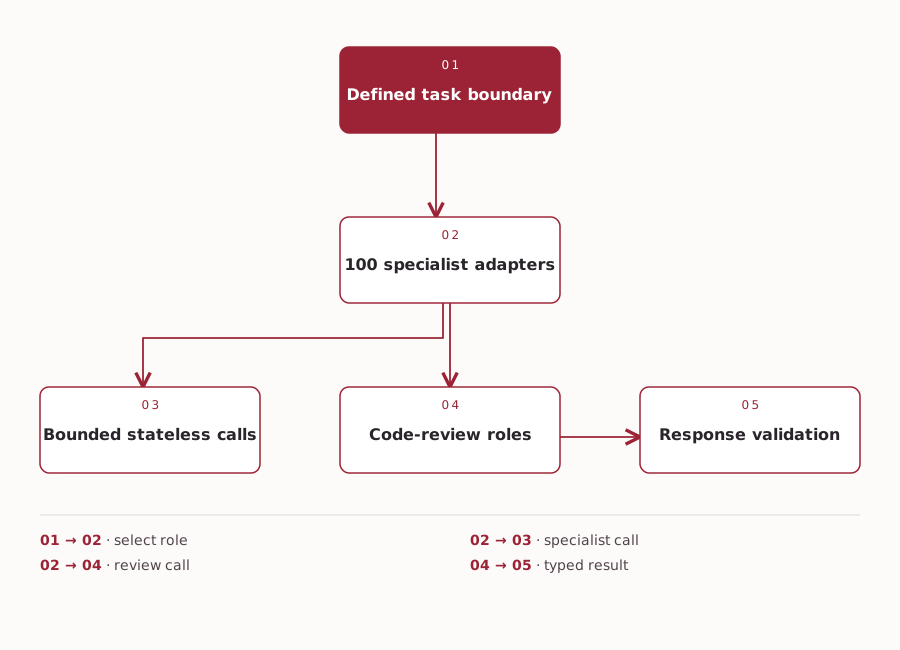
Core includes 100 fine-tuned specialist adapters for bounded stateless calls and code-review roles. Each call receives a defined purpose and structured evidence. Software validates its response and retains the accepted result with model attribution.

Bounded model calls

Capacity, token accounting and response limits surround the call. The task boundary selects the specialist; the engagement keeps the evidence and review history.

Core model entitlement
Bounded model calls — source-derived relationship diagram
Bounded model calls · overview.
Advanced model entitlement

Harder work needs a persistent workspace

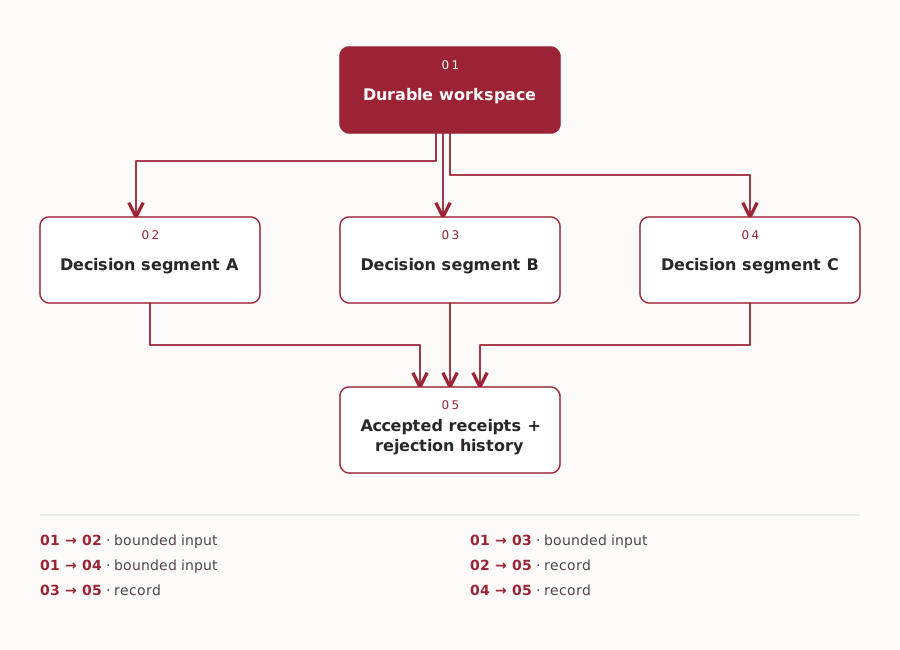
The fine-tuned 30B3A Flash model supports persistent higher-complexity sessions. Executive, capability-development and repair workspaces carry accepted artifacts, prior review and progress between segments.

Persistent model sessions

Access to fine-tuned models and specialist adapters follows controlled subscription gates. Weekly model credits and selective weights entitlements support different deployment needs; the bundle comparison sets out those terms.

Advanced model entitlement
Persistent model sessions — source-derived relationship diagram
Persistent model sessions · overview.
Implemented

Build the missing interaction against a contract

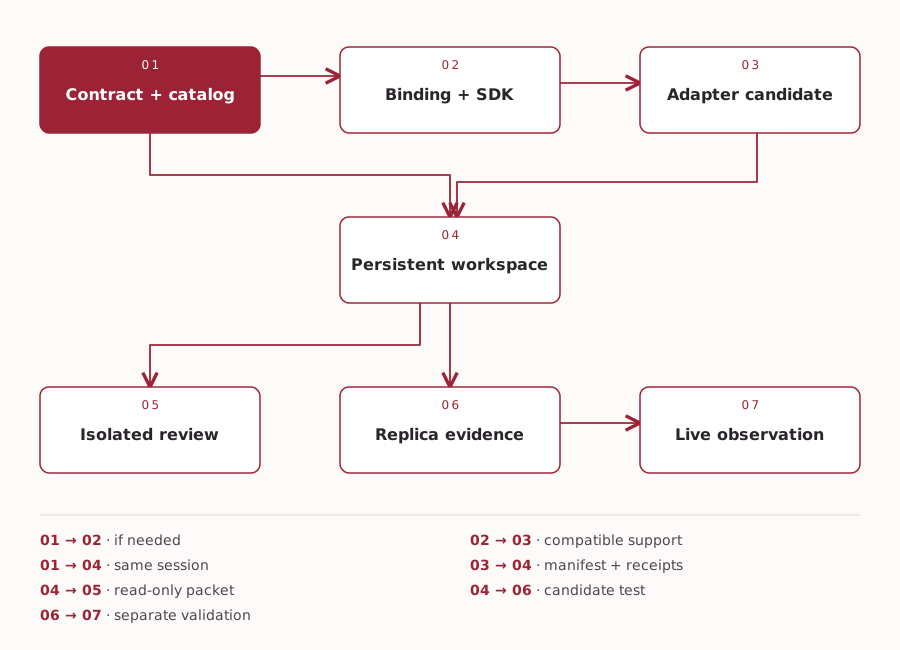
The Adaptive Capability Pipeline (ACP) is an adaptive capability-generation harness. It develops candidates from observed evidence and source mechanics, retaining the contract through binding, SDK selection, adapter generation, review and replica validation.

Capability development

A compatible catalog artifact or SDK can remove unnecessary generation work. New candidates retain their correction history and supporting artifacts for review.

Implemented
Capability development — source-derived relationship diagram
Capability development · overview.
Implemented

Generated code needs an admission boundary

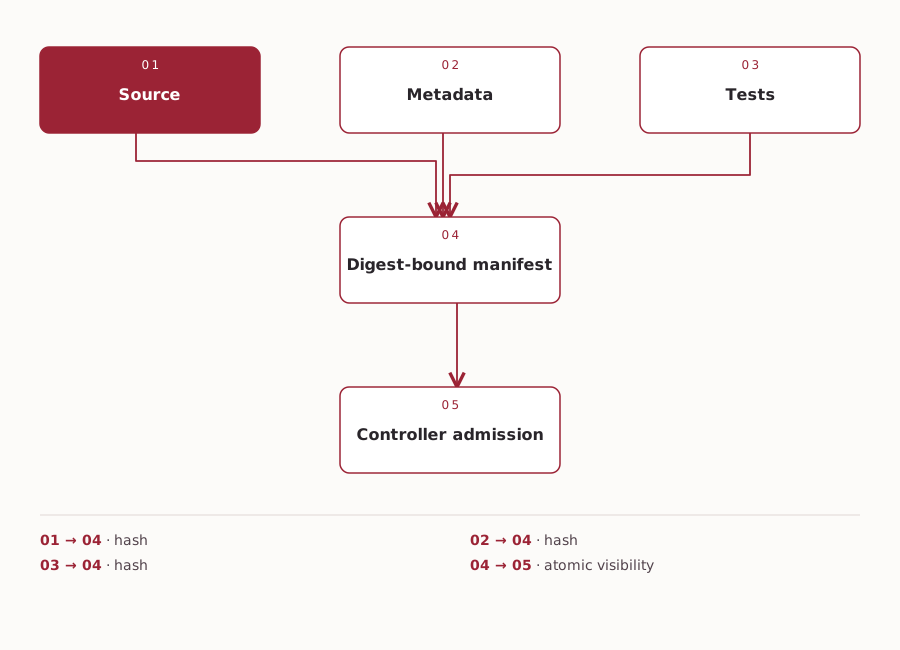
Source findings and advisories can inform a typed capability candidate. Source, metadata and tests are published together with their digests, giving review a specific artifact set to examine.

Candidate publication

The workbench can retain a candidate for controlled evaluation when a ready-made implementation is absent. Publication establishes artifact identity; admission determines whether it can be used.

Implemented
Candidate publication — source-derived relationship diagram
Candidate publication · overview.
Implemented

Test what happens when the names change

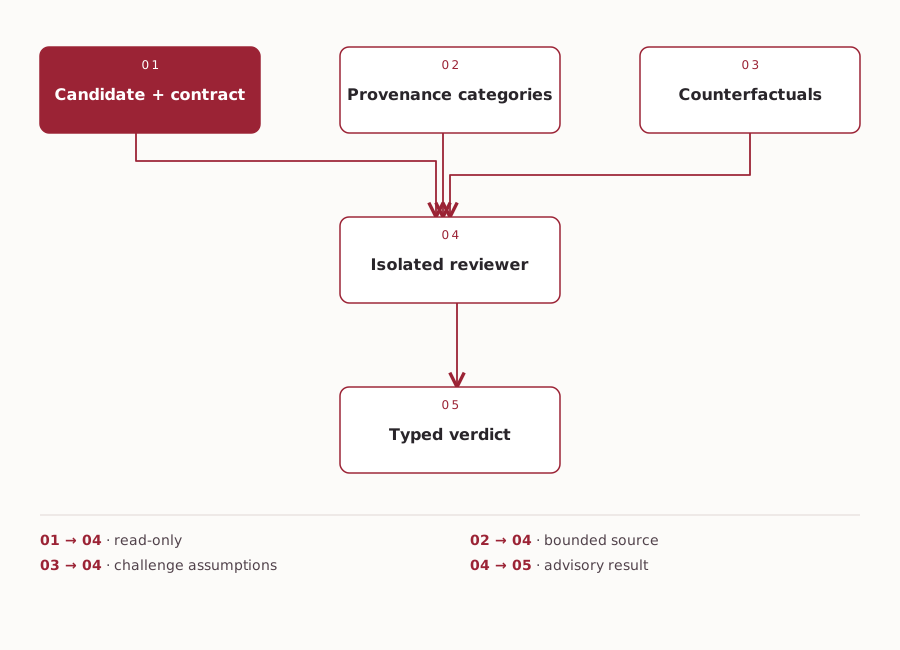
An isolated reviewer checks a candidate against its contract and provenance. Counterfactual cases change names, ordering, missing evidence and competing candidates to assess whether the behavior generalizes.

Independent capability review

The reviewer receives a read-only packet and returns a typed verdict. Generation, review and execution permission remain separately owned.

Implemented
Independent capability review — source-derived relationship diagram
Independent capability review · overview.
Implemented

Repair has to end with a working hand-back

The Autonomic Engineering Plane (AEP) is an adaptive software-repair harness. It owns diagnosis, a persistent repair session, scoped changes, tests, build admission and hot replacement, ending with verified hand-back to the run.

Runtime software repair

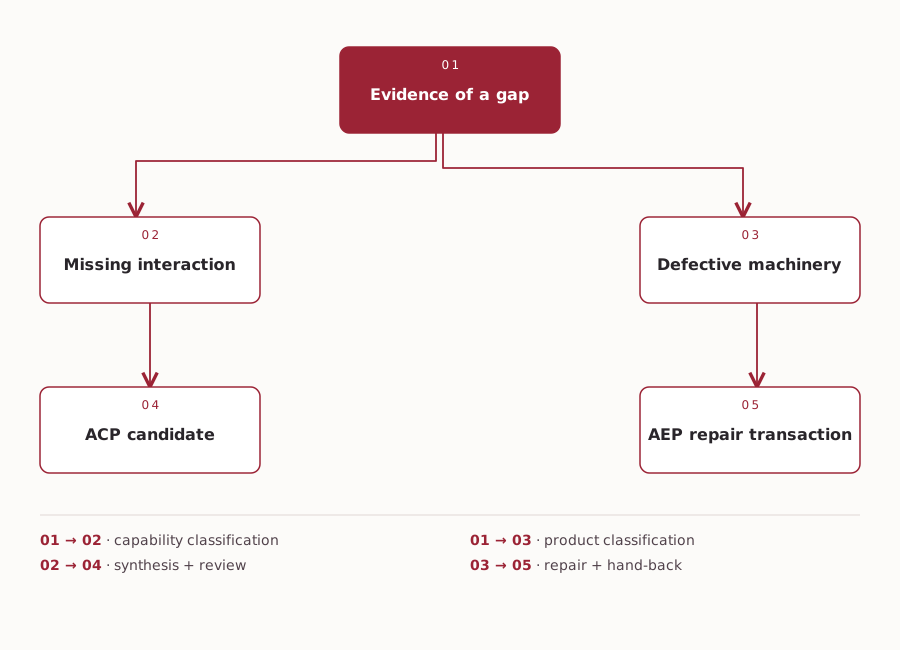
A missing interaction belongs to capability development; a defect in supported platform behavior belongs to software repair. The repair loop is assessed as a complete transaction, beyond the existence of a patch.

Implemented
Runtime software repair — source-derived relationship diagram
Runtime software repair · overview.
AEP, artifacts and integrated tools

Continuity is an engineering problem

Implemented

Replace the worker. Retain the record.

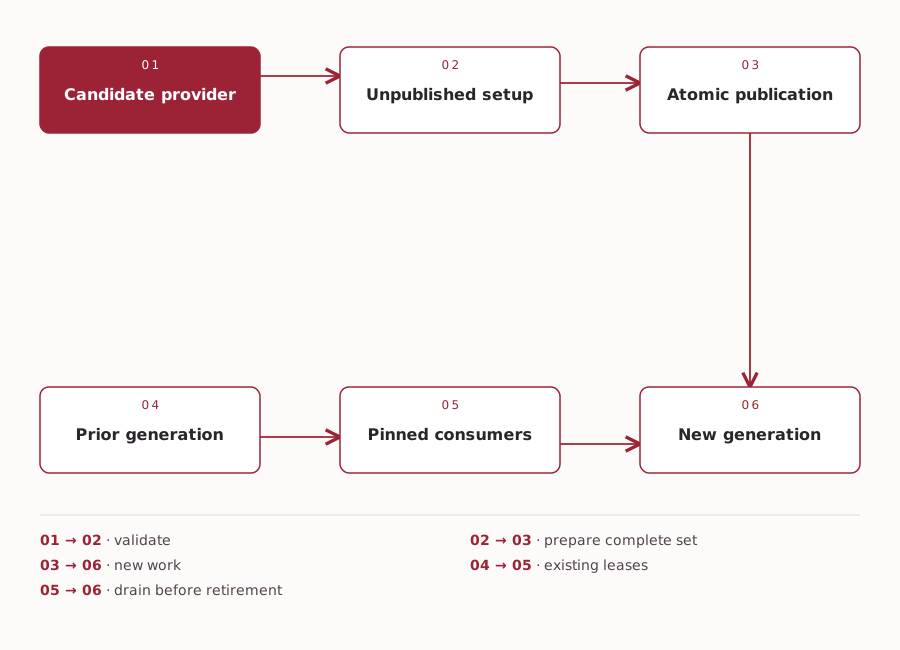
Versioned providers give runtime replacement a defined boundary. New work can adopt a replacement while existing work retains its implementation and the engagement state stays outside the provider.

Provider replacement

The Runtime Composition Kernel owns publication, leases, rollback and cleanup. This supplies the lifecycle foundation for repair without requiring the investigation record to move with the code.

Implemented
Provider replacement — source-derived relationship diagram
Provider replacement · overview.
Implemented

Old work cannot silently become current

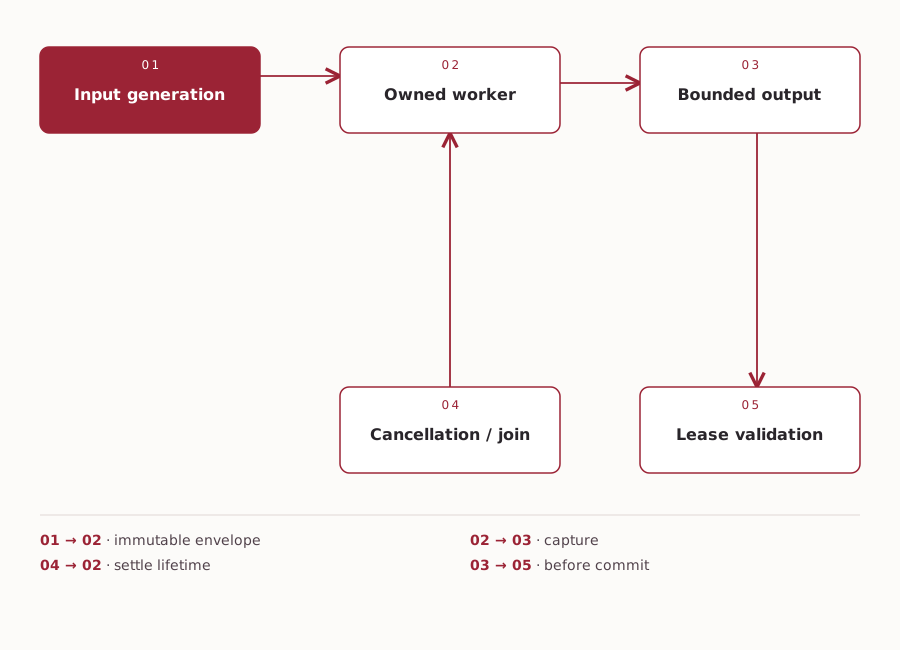
Isolated workers receive immutable execution envelopes. Acceptance checks the artifact, input and generation lease, so an expired worker cannot publish a plausible result into the current run.

Worker result attribution

In-process handlers and isolated workers have different replacement boundaries. A lease identifies the implementation responsible for a result. Process ownership, bounded output, cleanup handles and token accounting make resource use inspectable.

Implemented
Worker result attribution — source-derived relationship diagram
Worker result attribution · overview.
Implemented

Keep specialist tools in their native setting

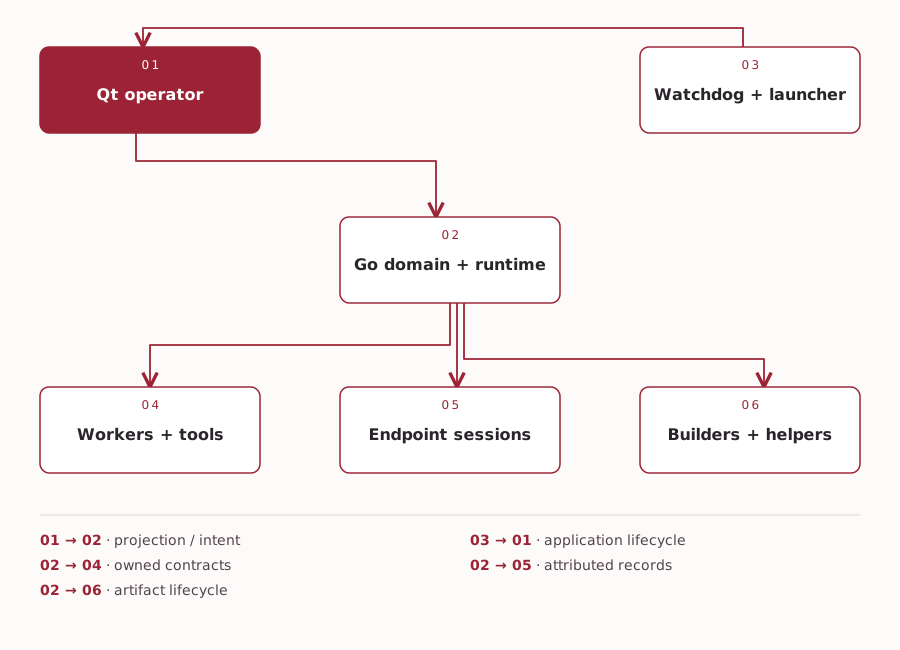
The Qt workspace combines dense investigation views with retained tool surfaces. Gitea, BloodHound, build workflows, RDP and development harnesses can sit alongside the operator environment.

Workspace integration

Lightweight QML chrome surrounds native widgets. Embedded windows preserve specialist interfaces while the investigation remains visible. Binary and source analysis remain beside the workbench; their results return to the same investigation record.

Implemented
Workspace integration — source-derived relationship diagram
Workspace integration · overview.
Implemented

Integration begins after the tool runs

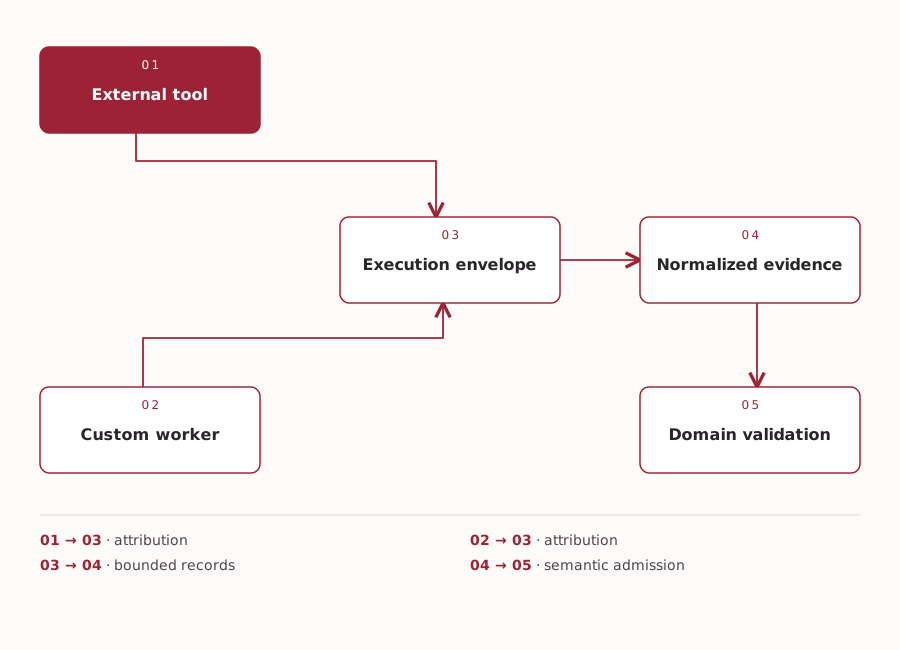
Network, web, directory, browser and source-inspection tools produce different kinds of output. Their value to the platform comes from controlled execution and the attributed evidence returned to the engagement.

Third-party execution

Admitted third-party proof-of-concept work can use isolated containers. Tool availability, candidate review and execution permission remain separate inputs.

Implemented
Third-party execution — source-derived relationship diagram
Third-party execution · overview.
Implemented

Built bytes need a traceable identity

Versioned builds, transformation and obfuscation components form the artifact toolchain. VM-oriented transformation sits within that engineering scope; digests and provenance connect the resulting material to its recorded role.

Artifact identity

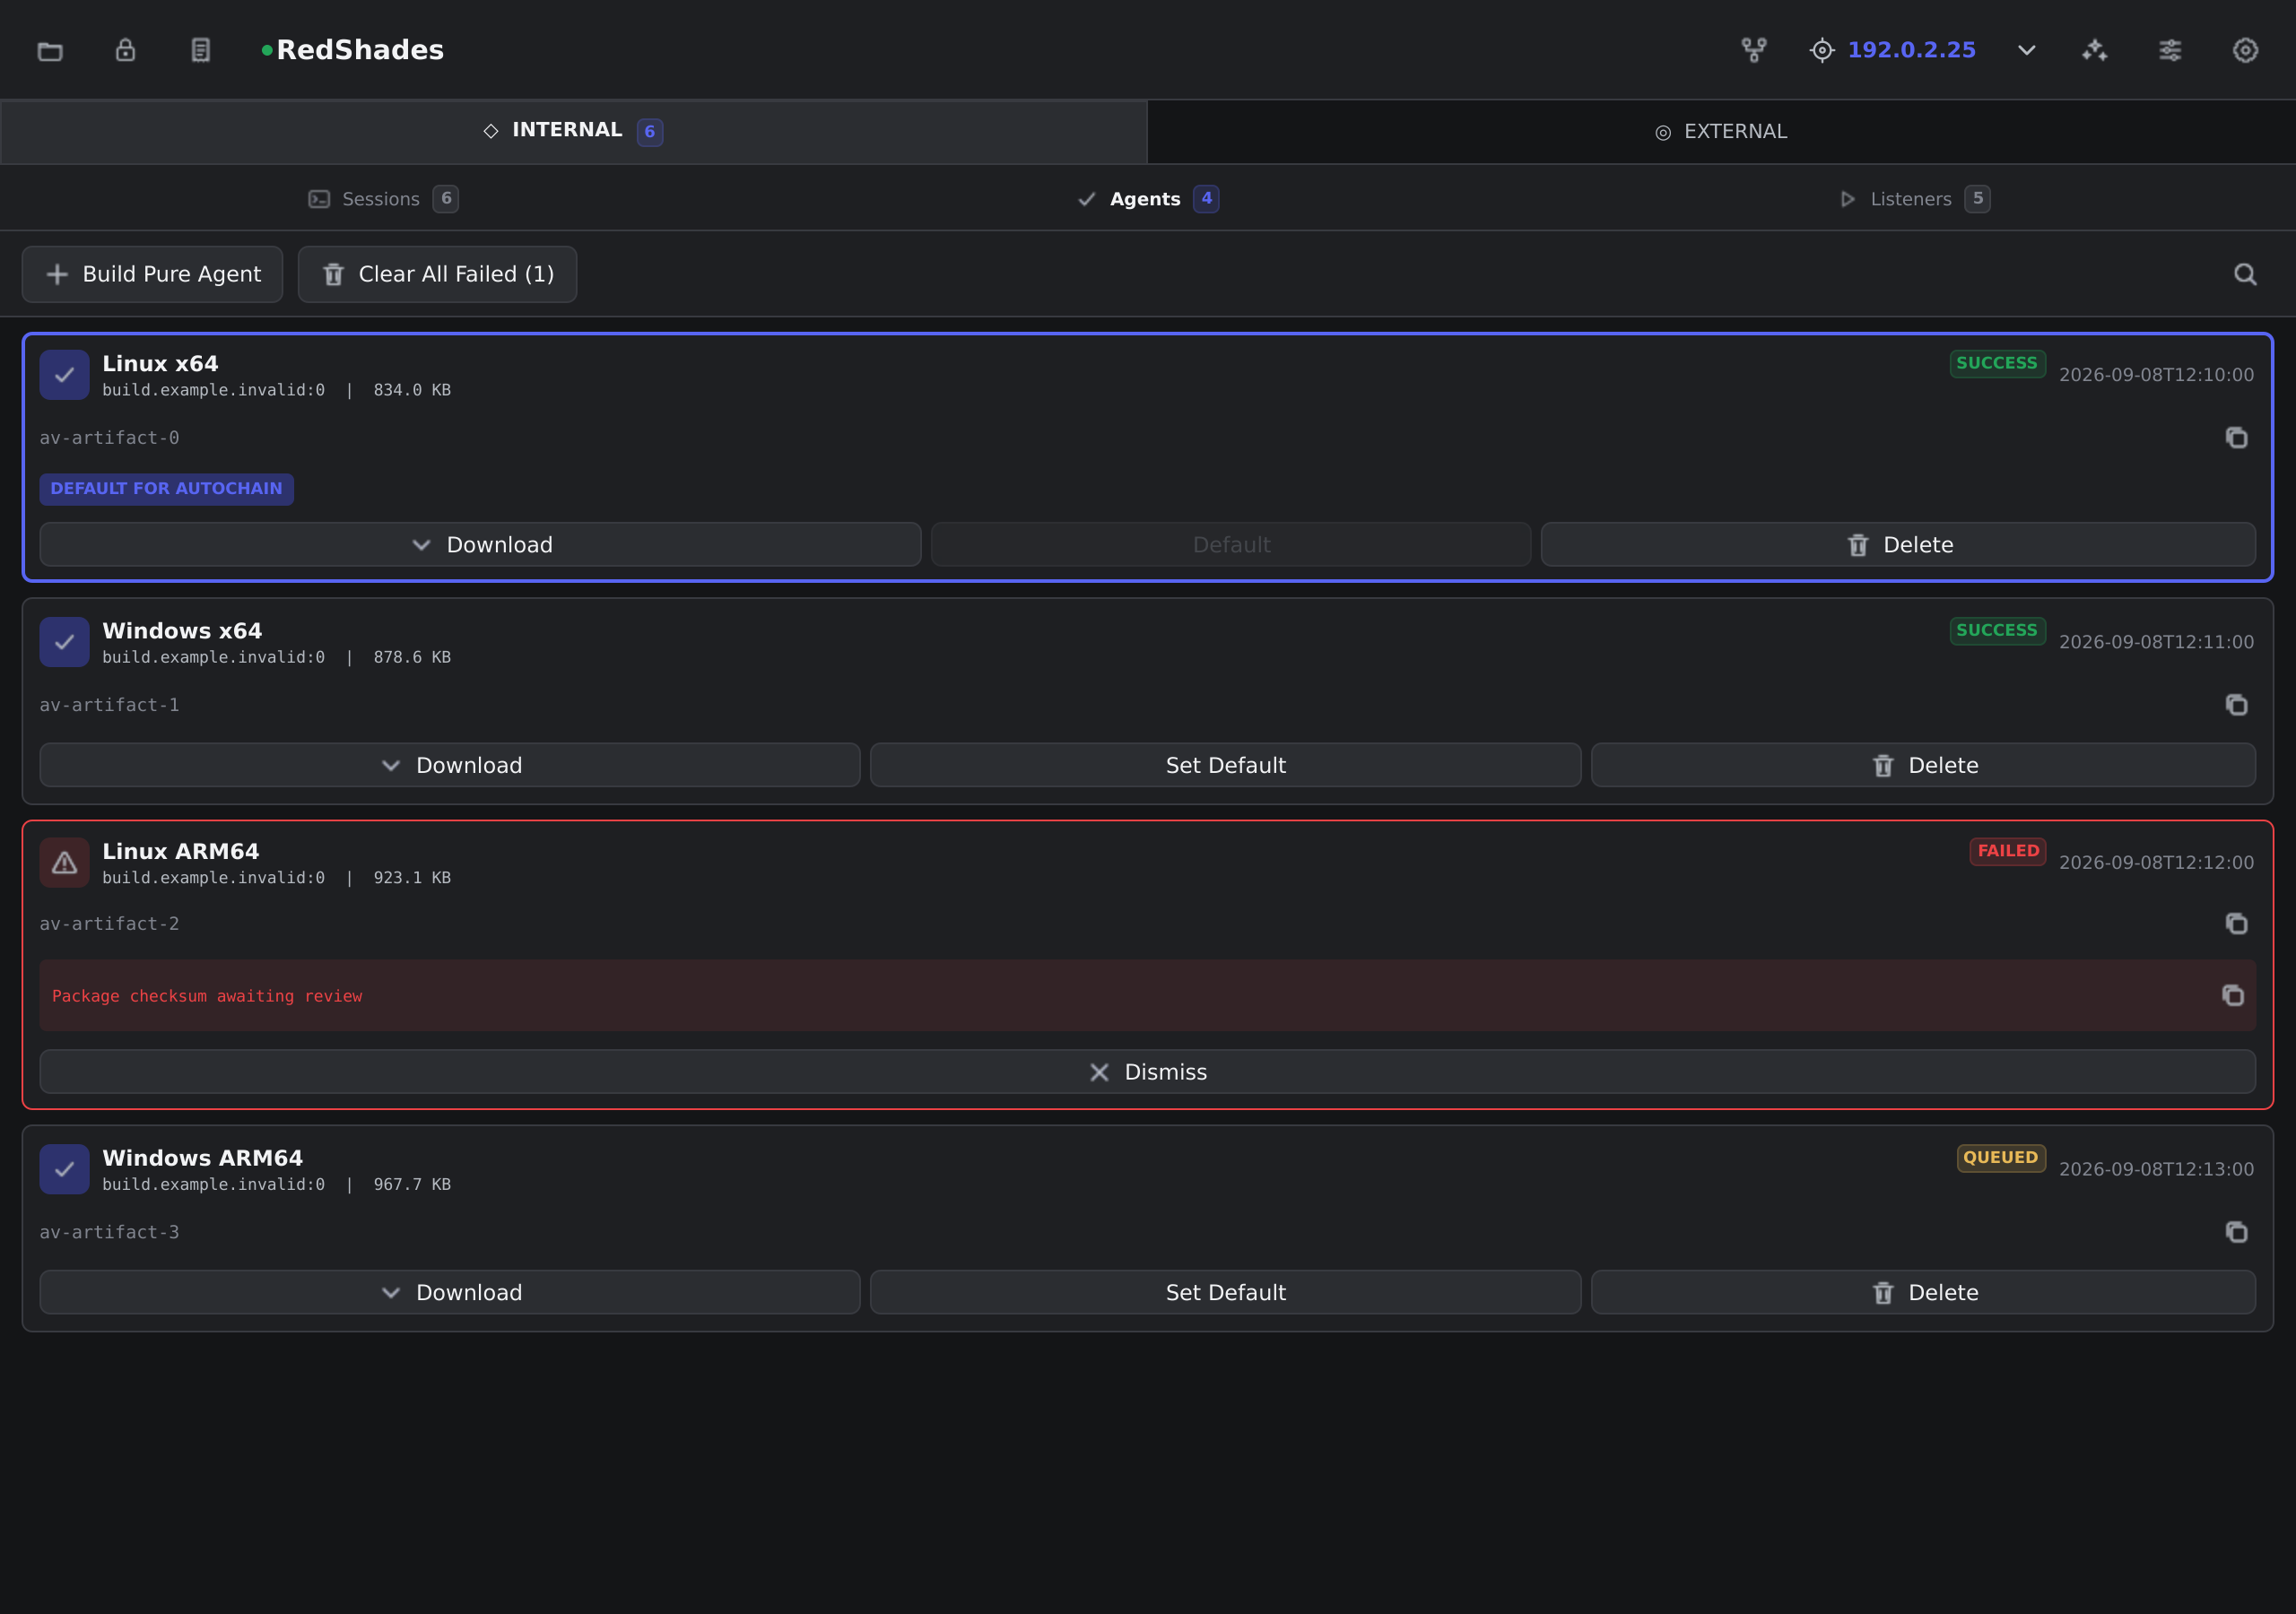
Native artifact views expose the inventory to the operator. A build record identifies material and purpose without implying that the artifact was deployed or a session established.

Implemented
Built bytes need a traceable identity — operator workspace
Compare versioned artifacts and their build states.
Implemented

A session adds context to the same investigation

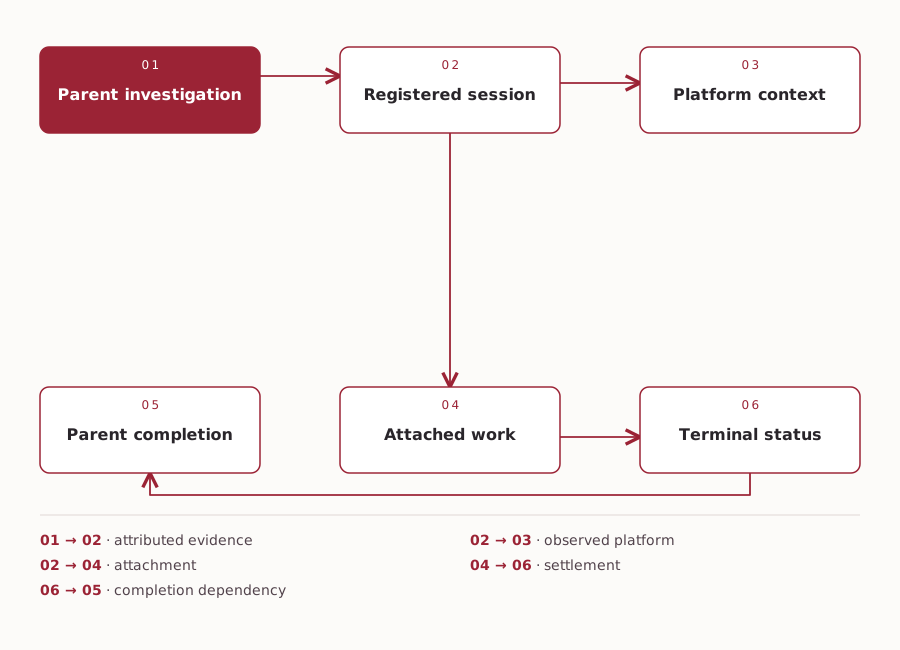
Registered sessions make platform-aware continuation available. Common, Windows and Linux stage families retain their prerequisites while artifacts and attached work remain linked to the parent engagement.

Session continuation

The 13 C2 continuation declarations complement the 88 Core stages. Session context selects applicable work.

Implemented
Session continuation — source-derived relationship diagram
Session continuation · overview.
Native Qt workspace

A workspace for close inspection

Native interface

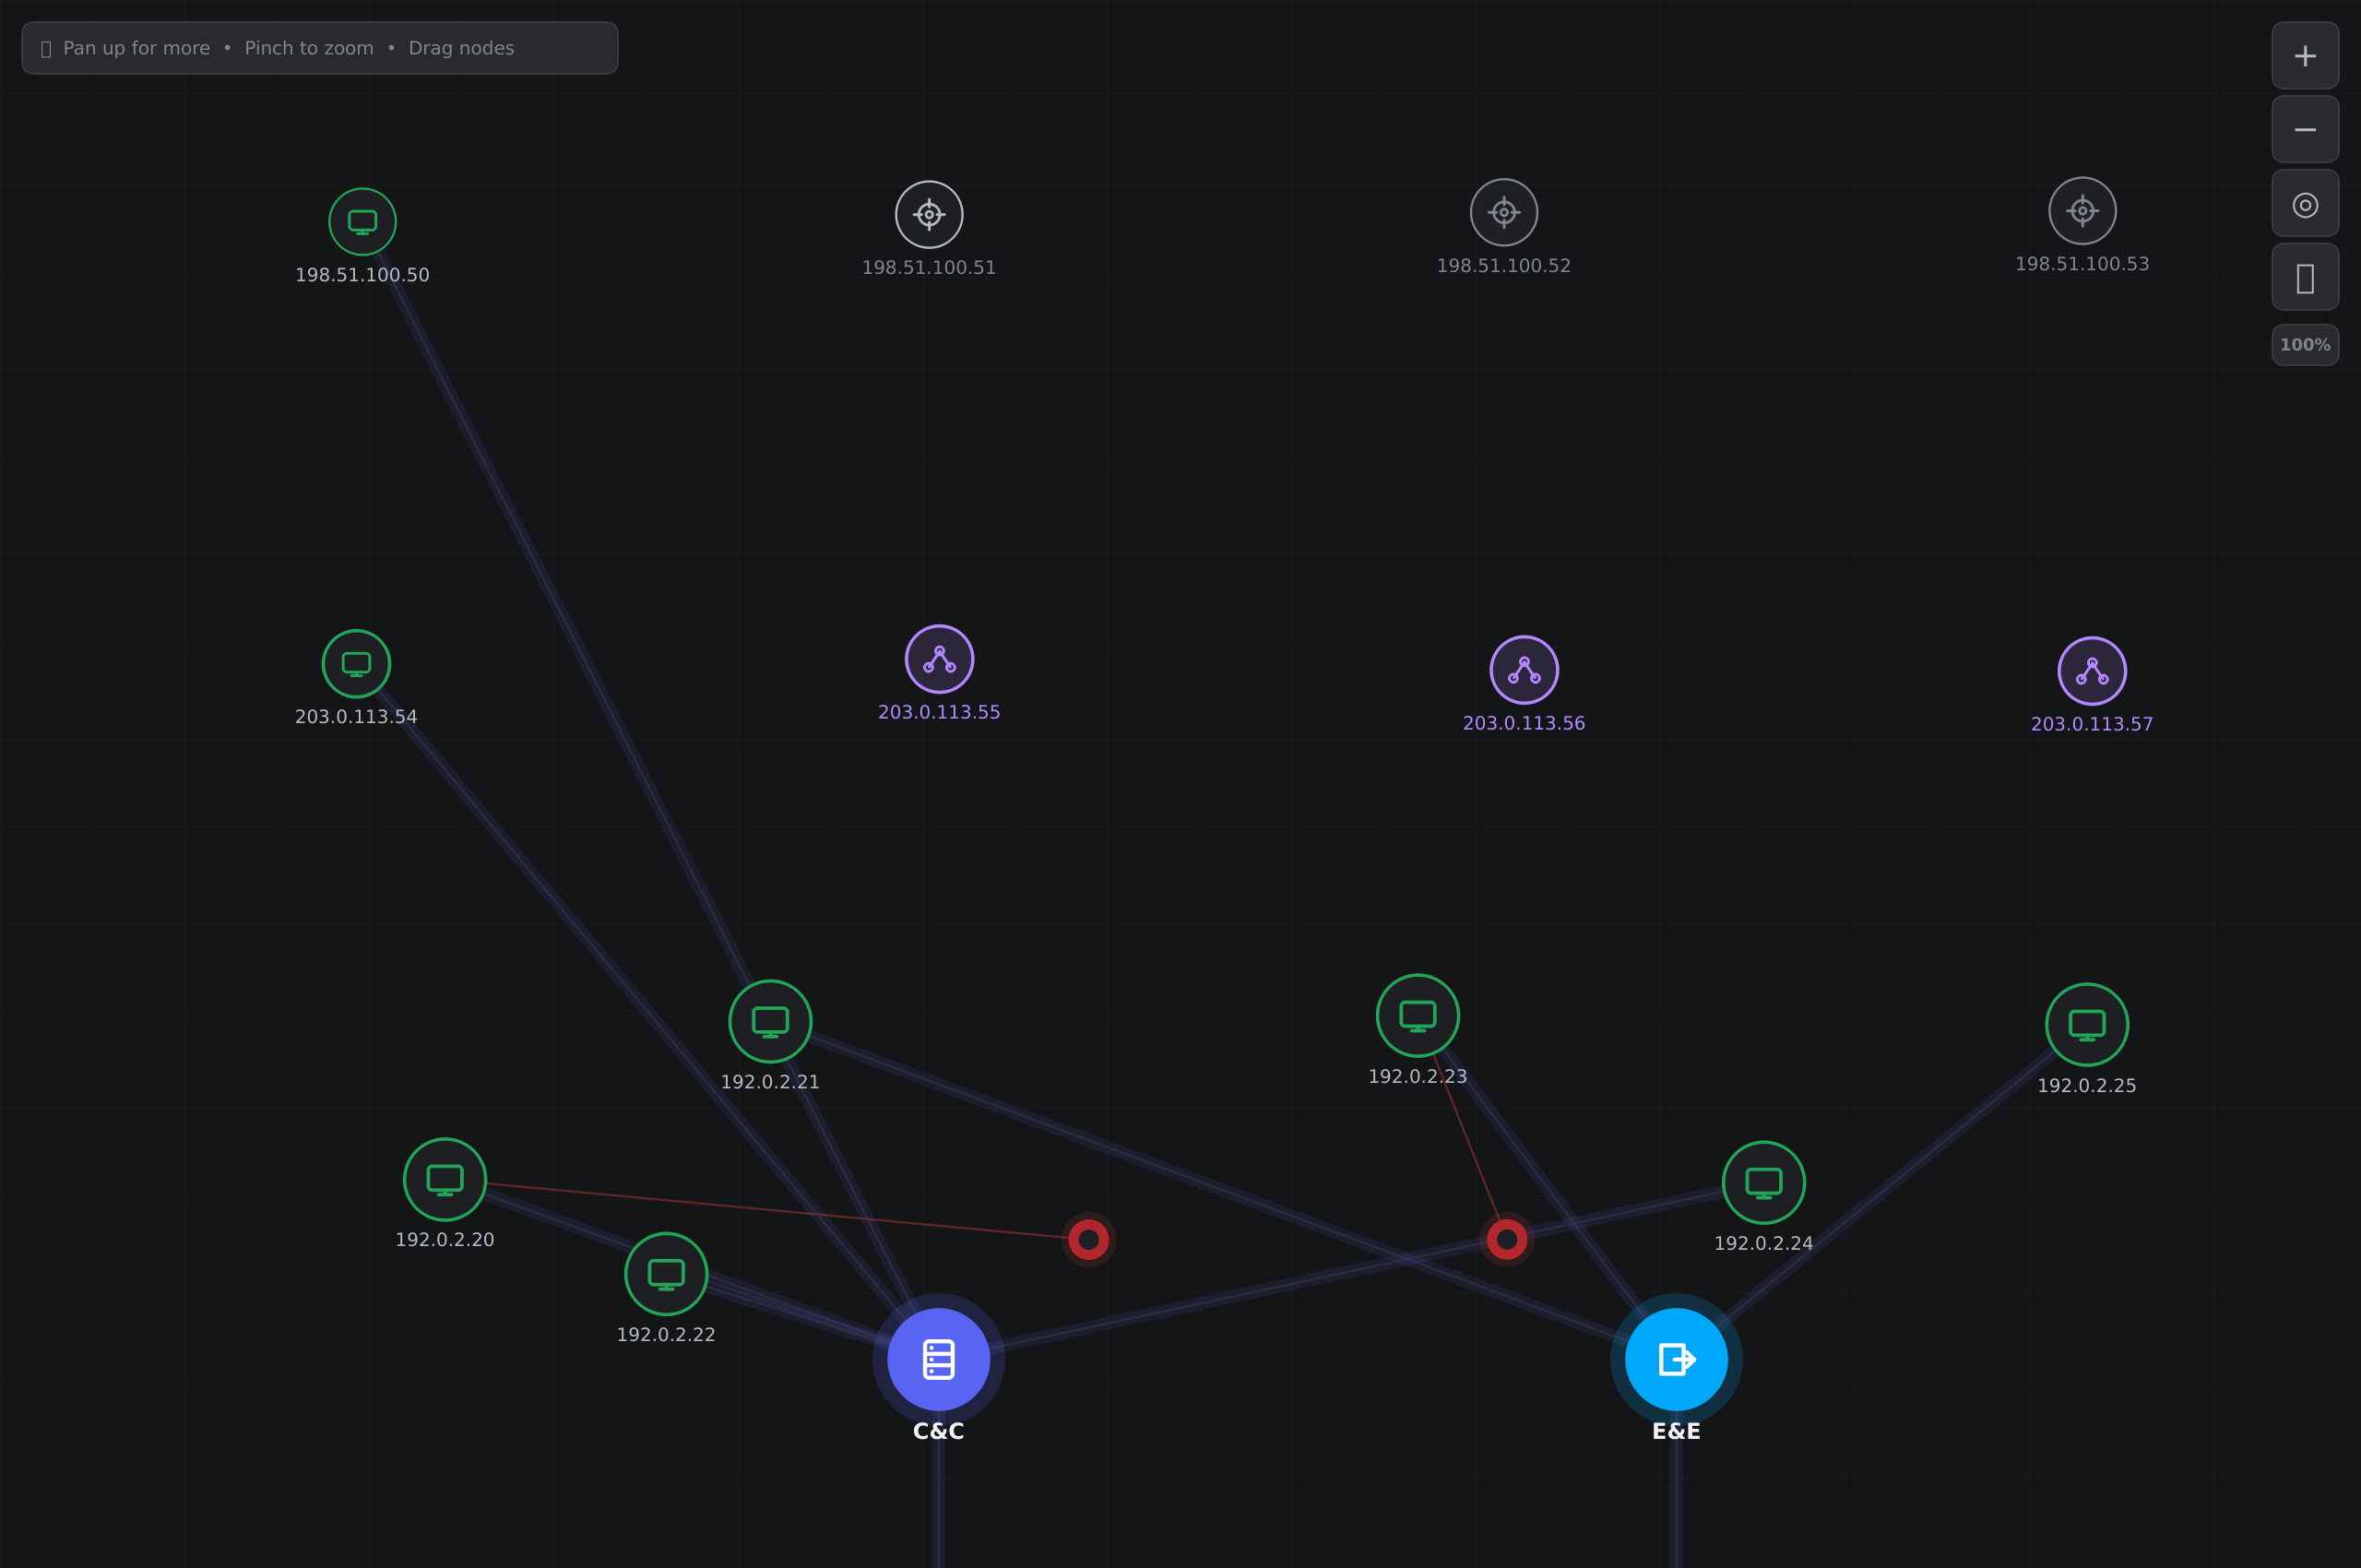
See where an observation belongs

Network Graph places observed hosts and relationships in the wider investigation. Selecting a host or link connects that overview to its available context.

Network Graph

A displayed relationship aids orientation. Its presence does not establish an admitted route or a verified capability.

Native interface
See where an observation belongs — operator workspace
Locate each host and its observed relationships in the wider investigation.
Native interface

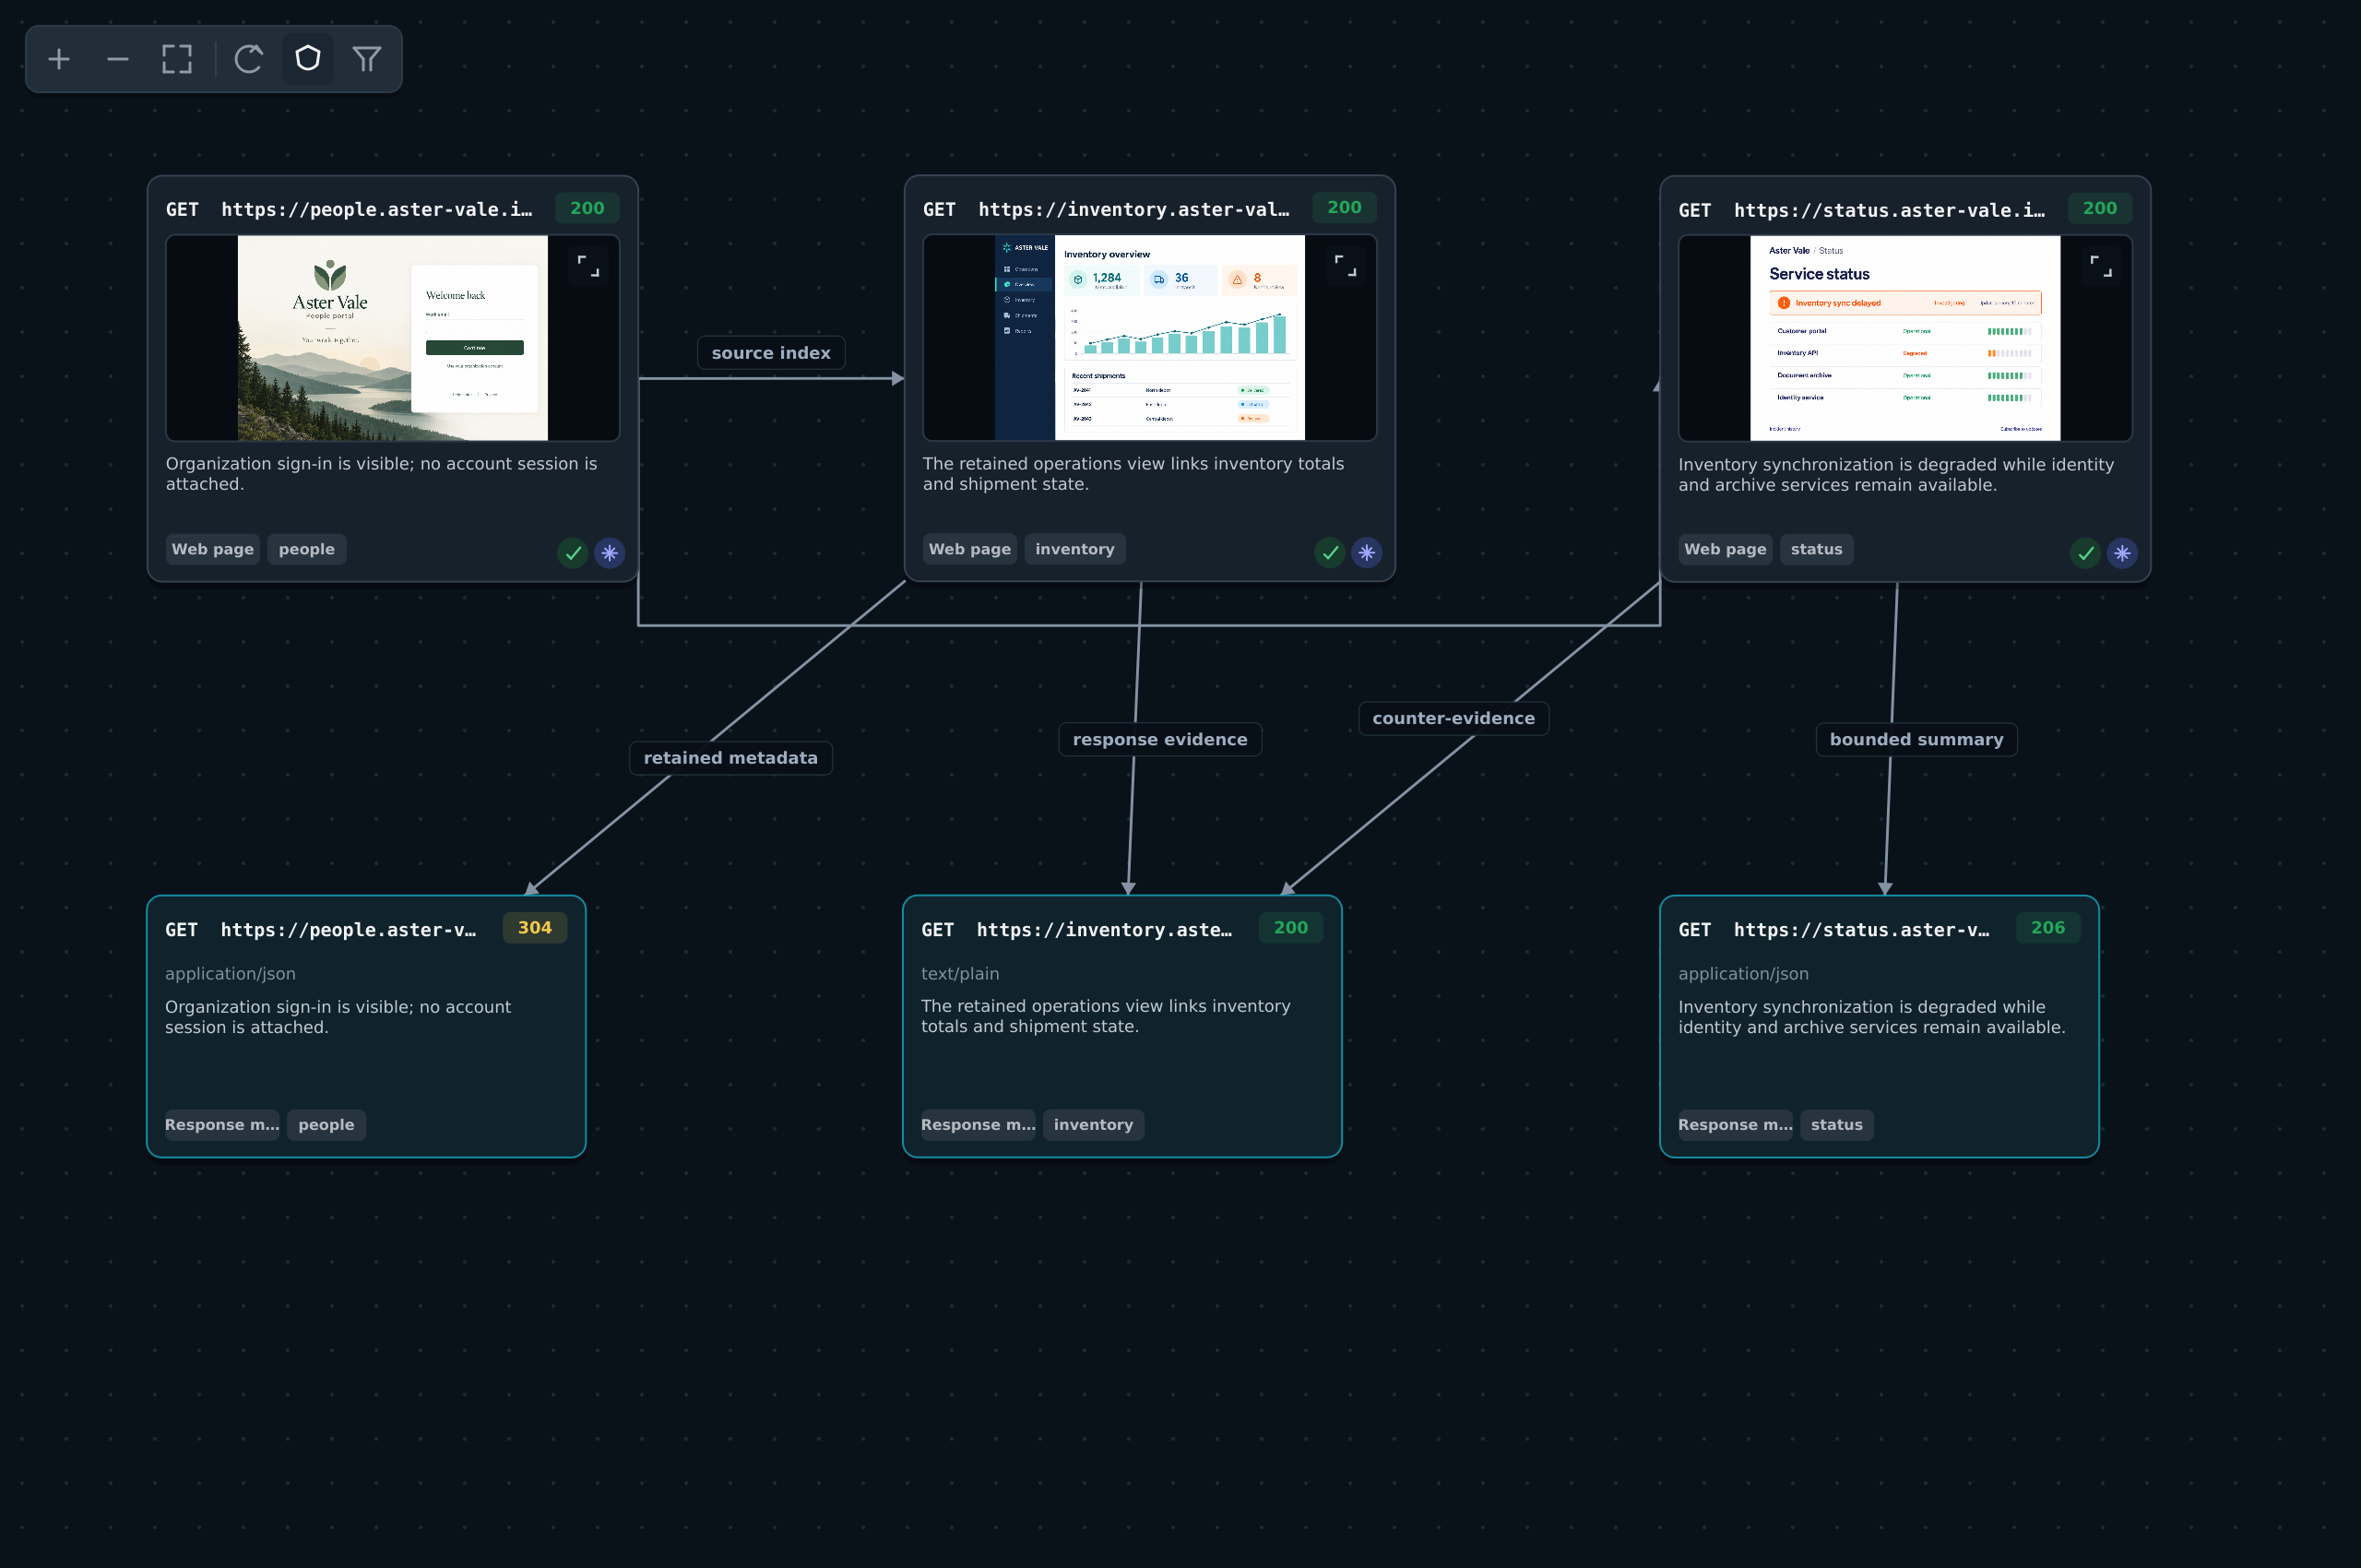
Read the source without losing the overview

WebRecon places web observations, source detail and endpoint review in one native surface. The operator can inspect a selected item while retaining the surrounding investigation.

WebRecon overview

Source material stays near the observation it supports, with selected evidence and review context available together.

Native interface
Read the source without losing the overview — operator workspace
Follow web observations from the page to the evidence record.
Native interface

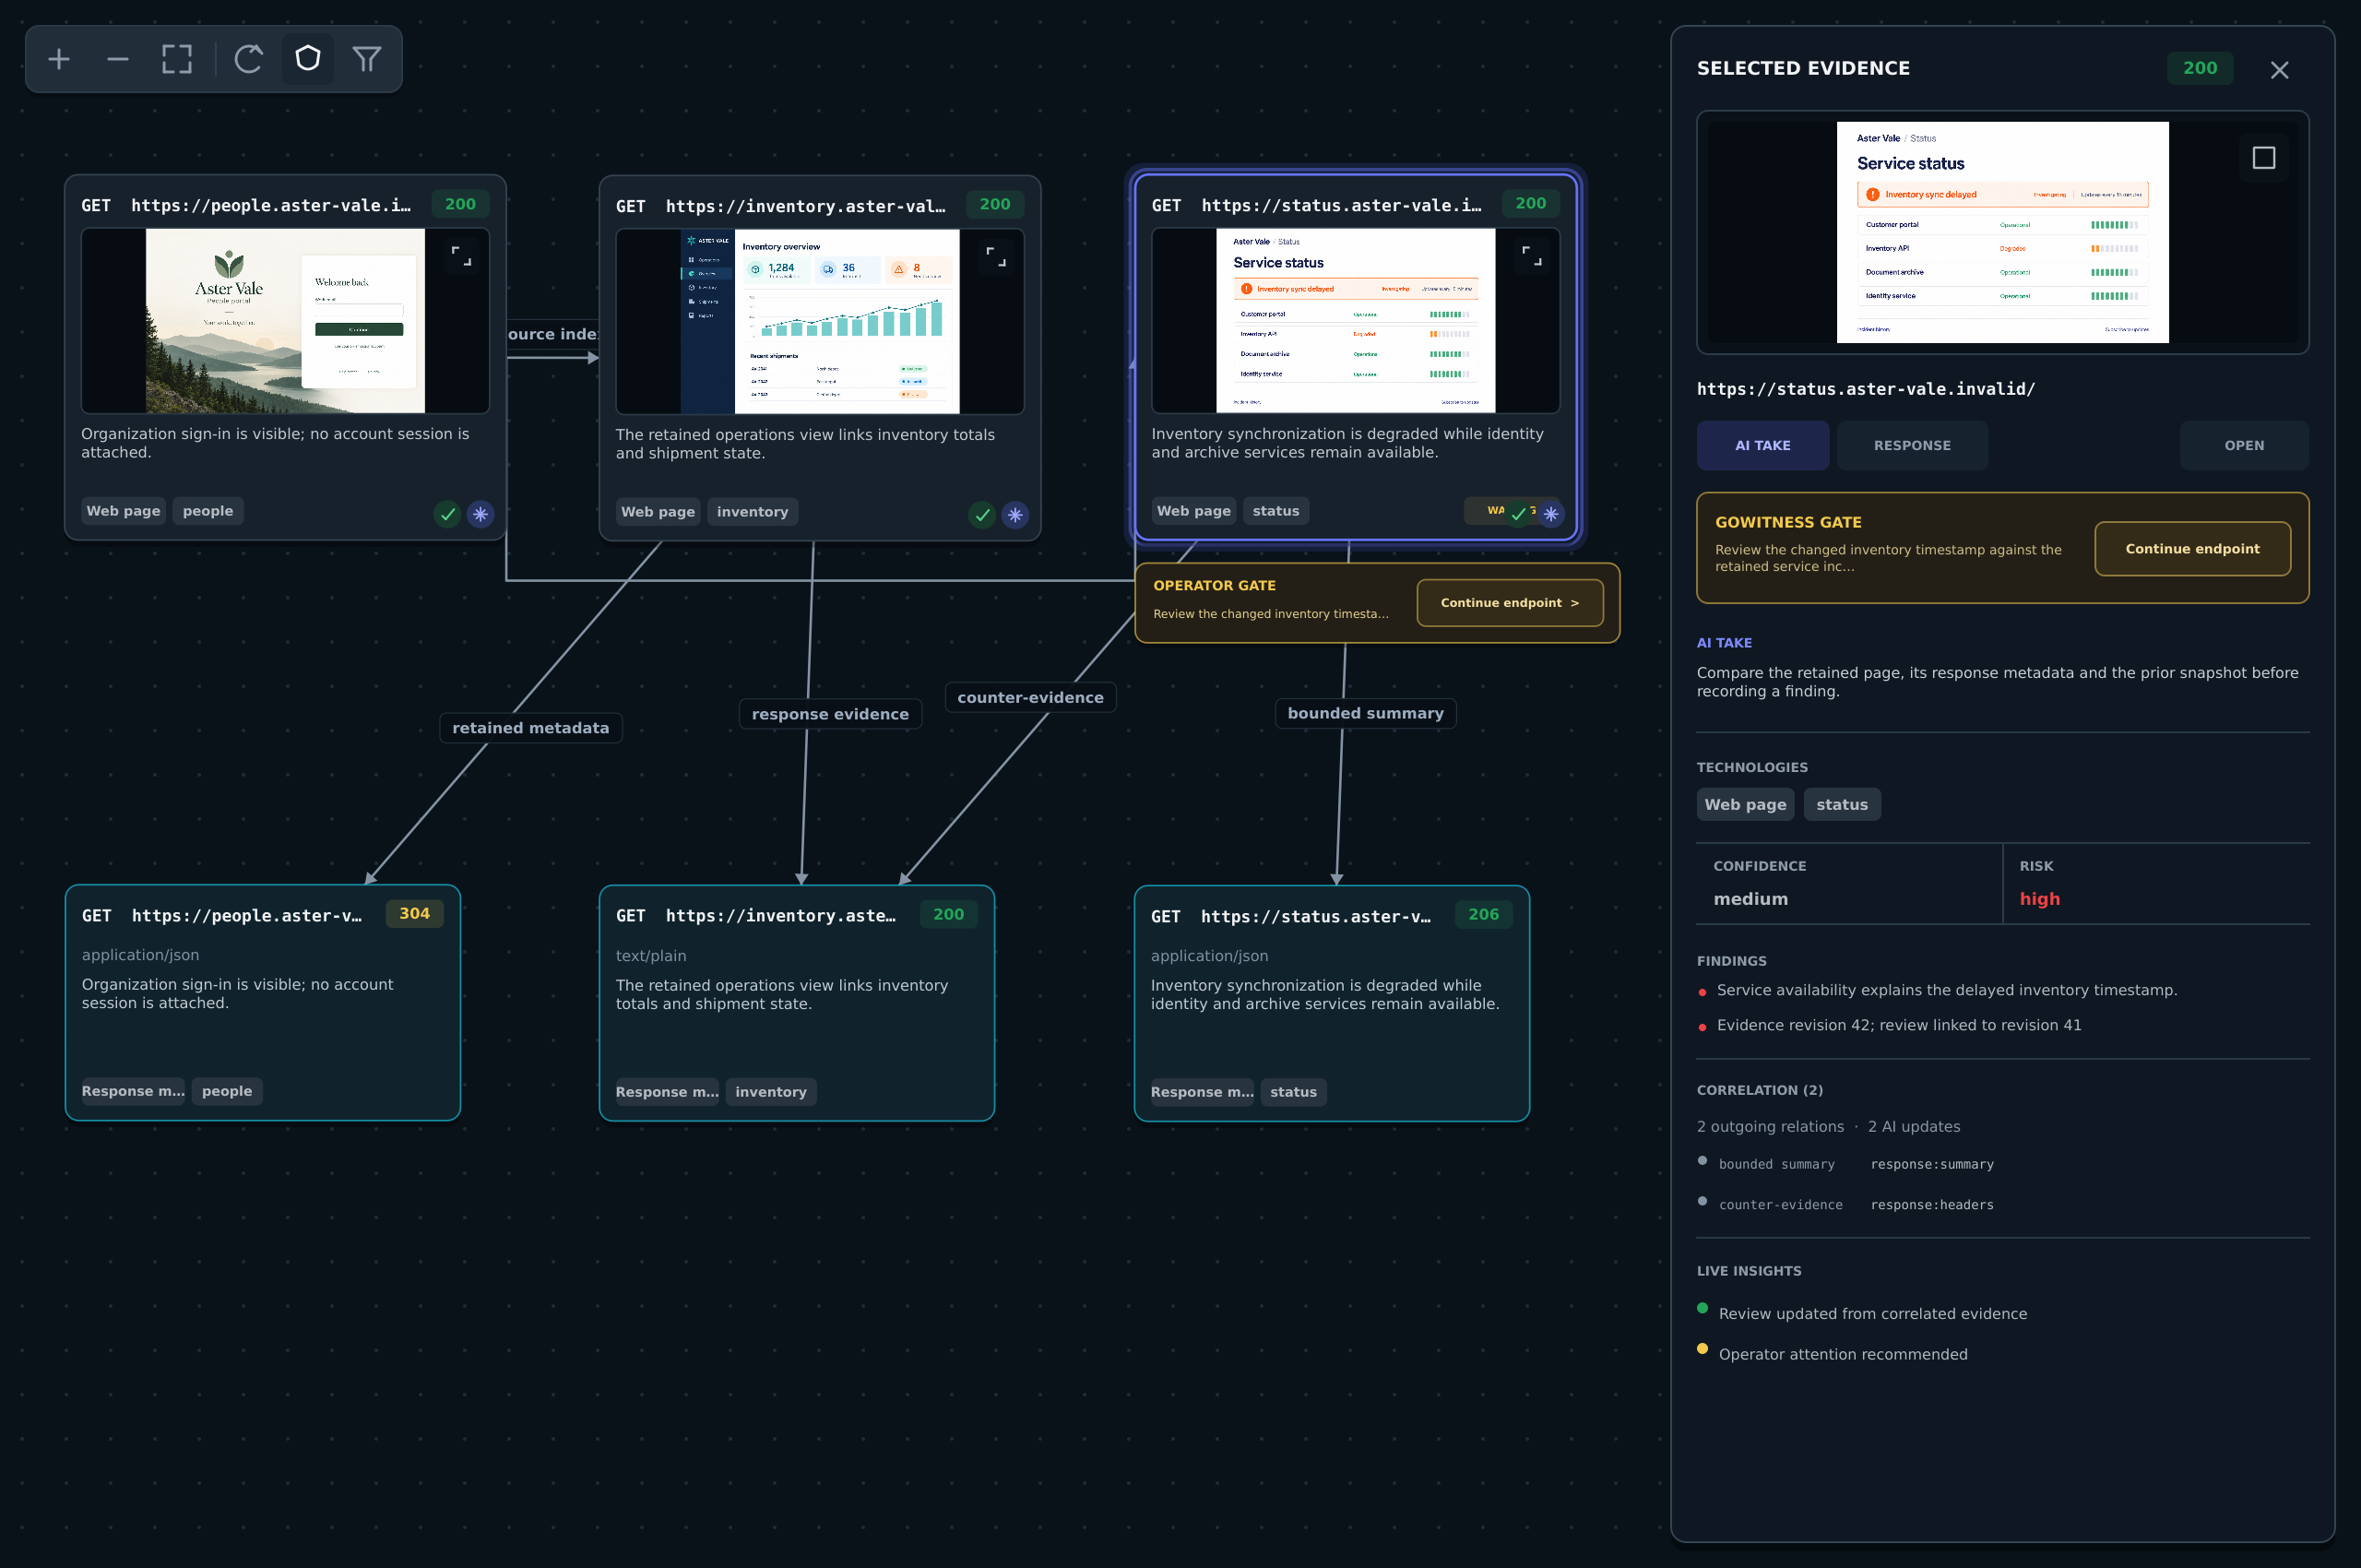
Make the pending decision specific

A review state identifies the affected endpoint or branch and its supporting evidence. The operator can see what is waiting and where the decision applies.

WebRecon review and gate state

A displayed gate communicates scope. Enforcement is established by policy and lifecycle validation, beyond the screenshot.

Native interface
Make the pending decision specific — operator workspace
See the endpoint, scope and evidence behind a pending review.
Native interface

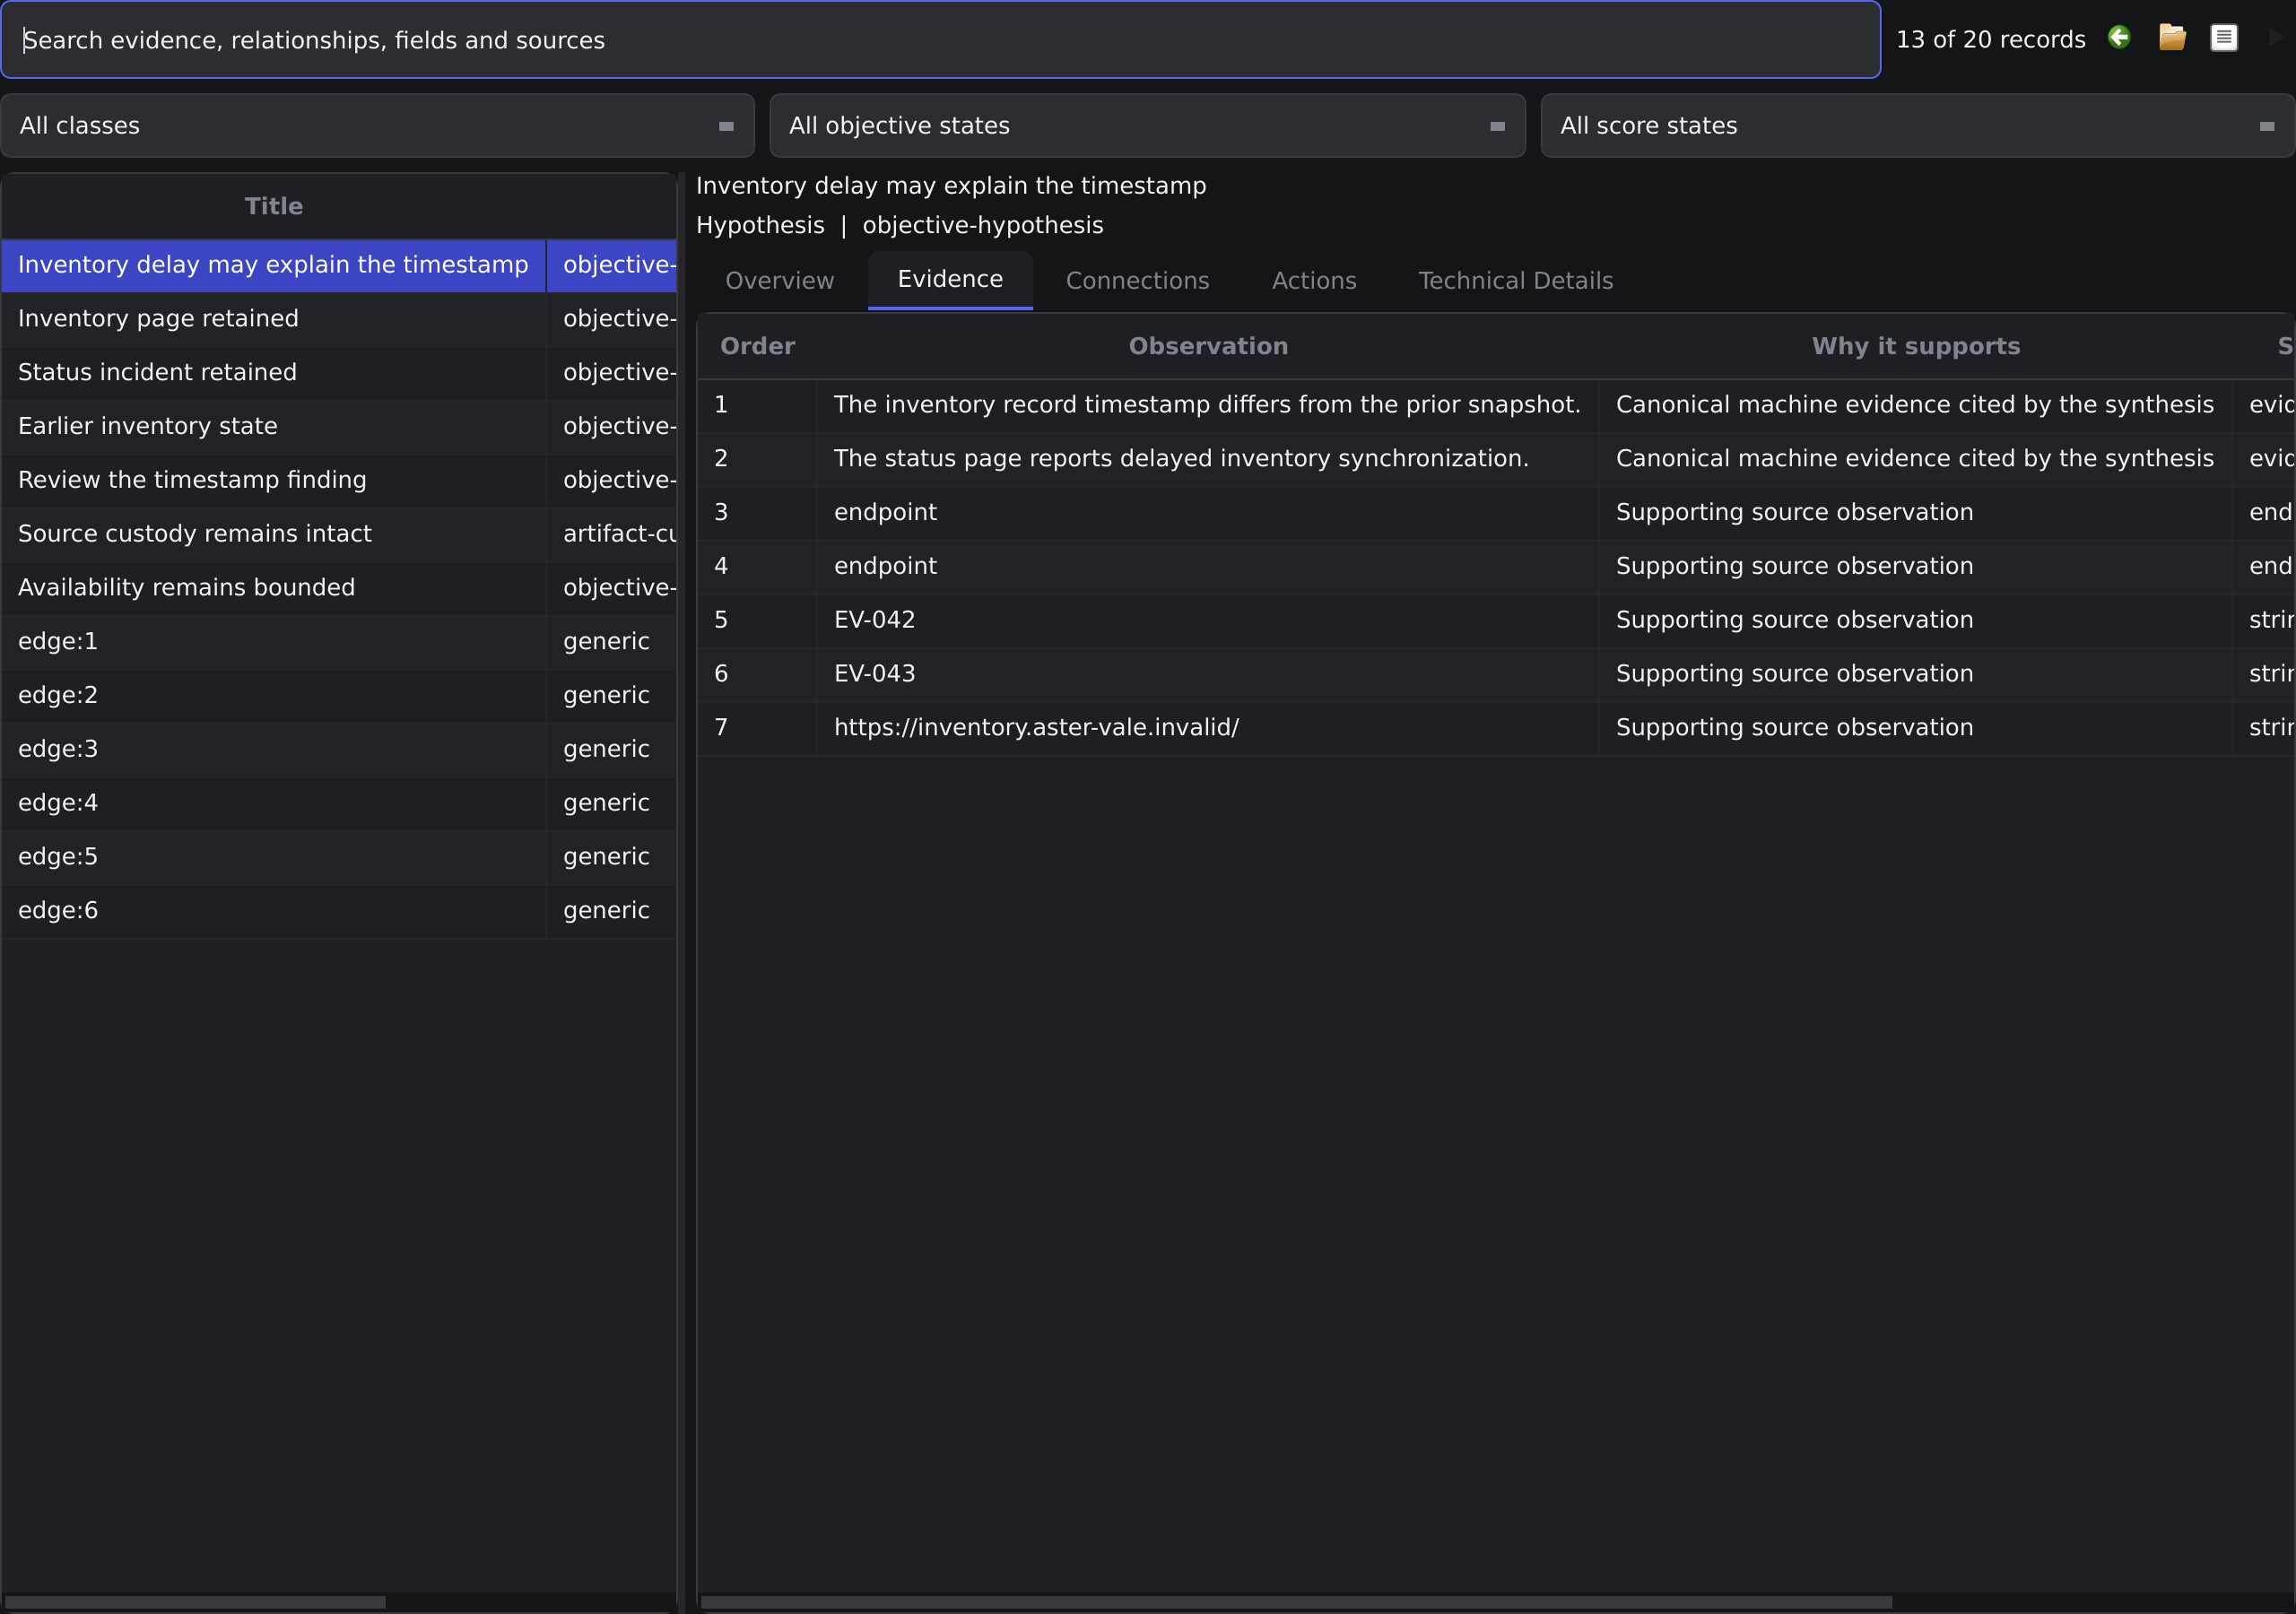
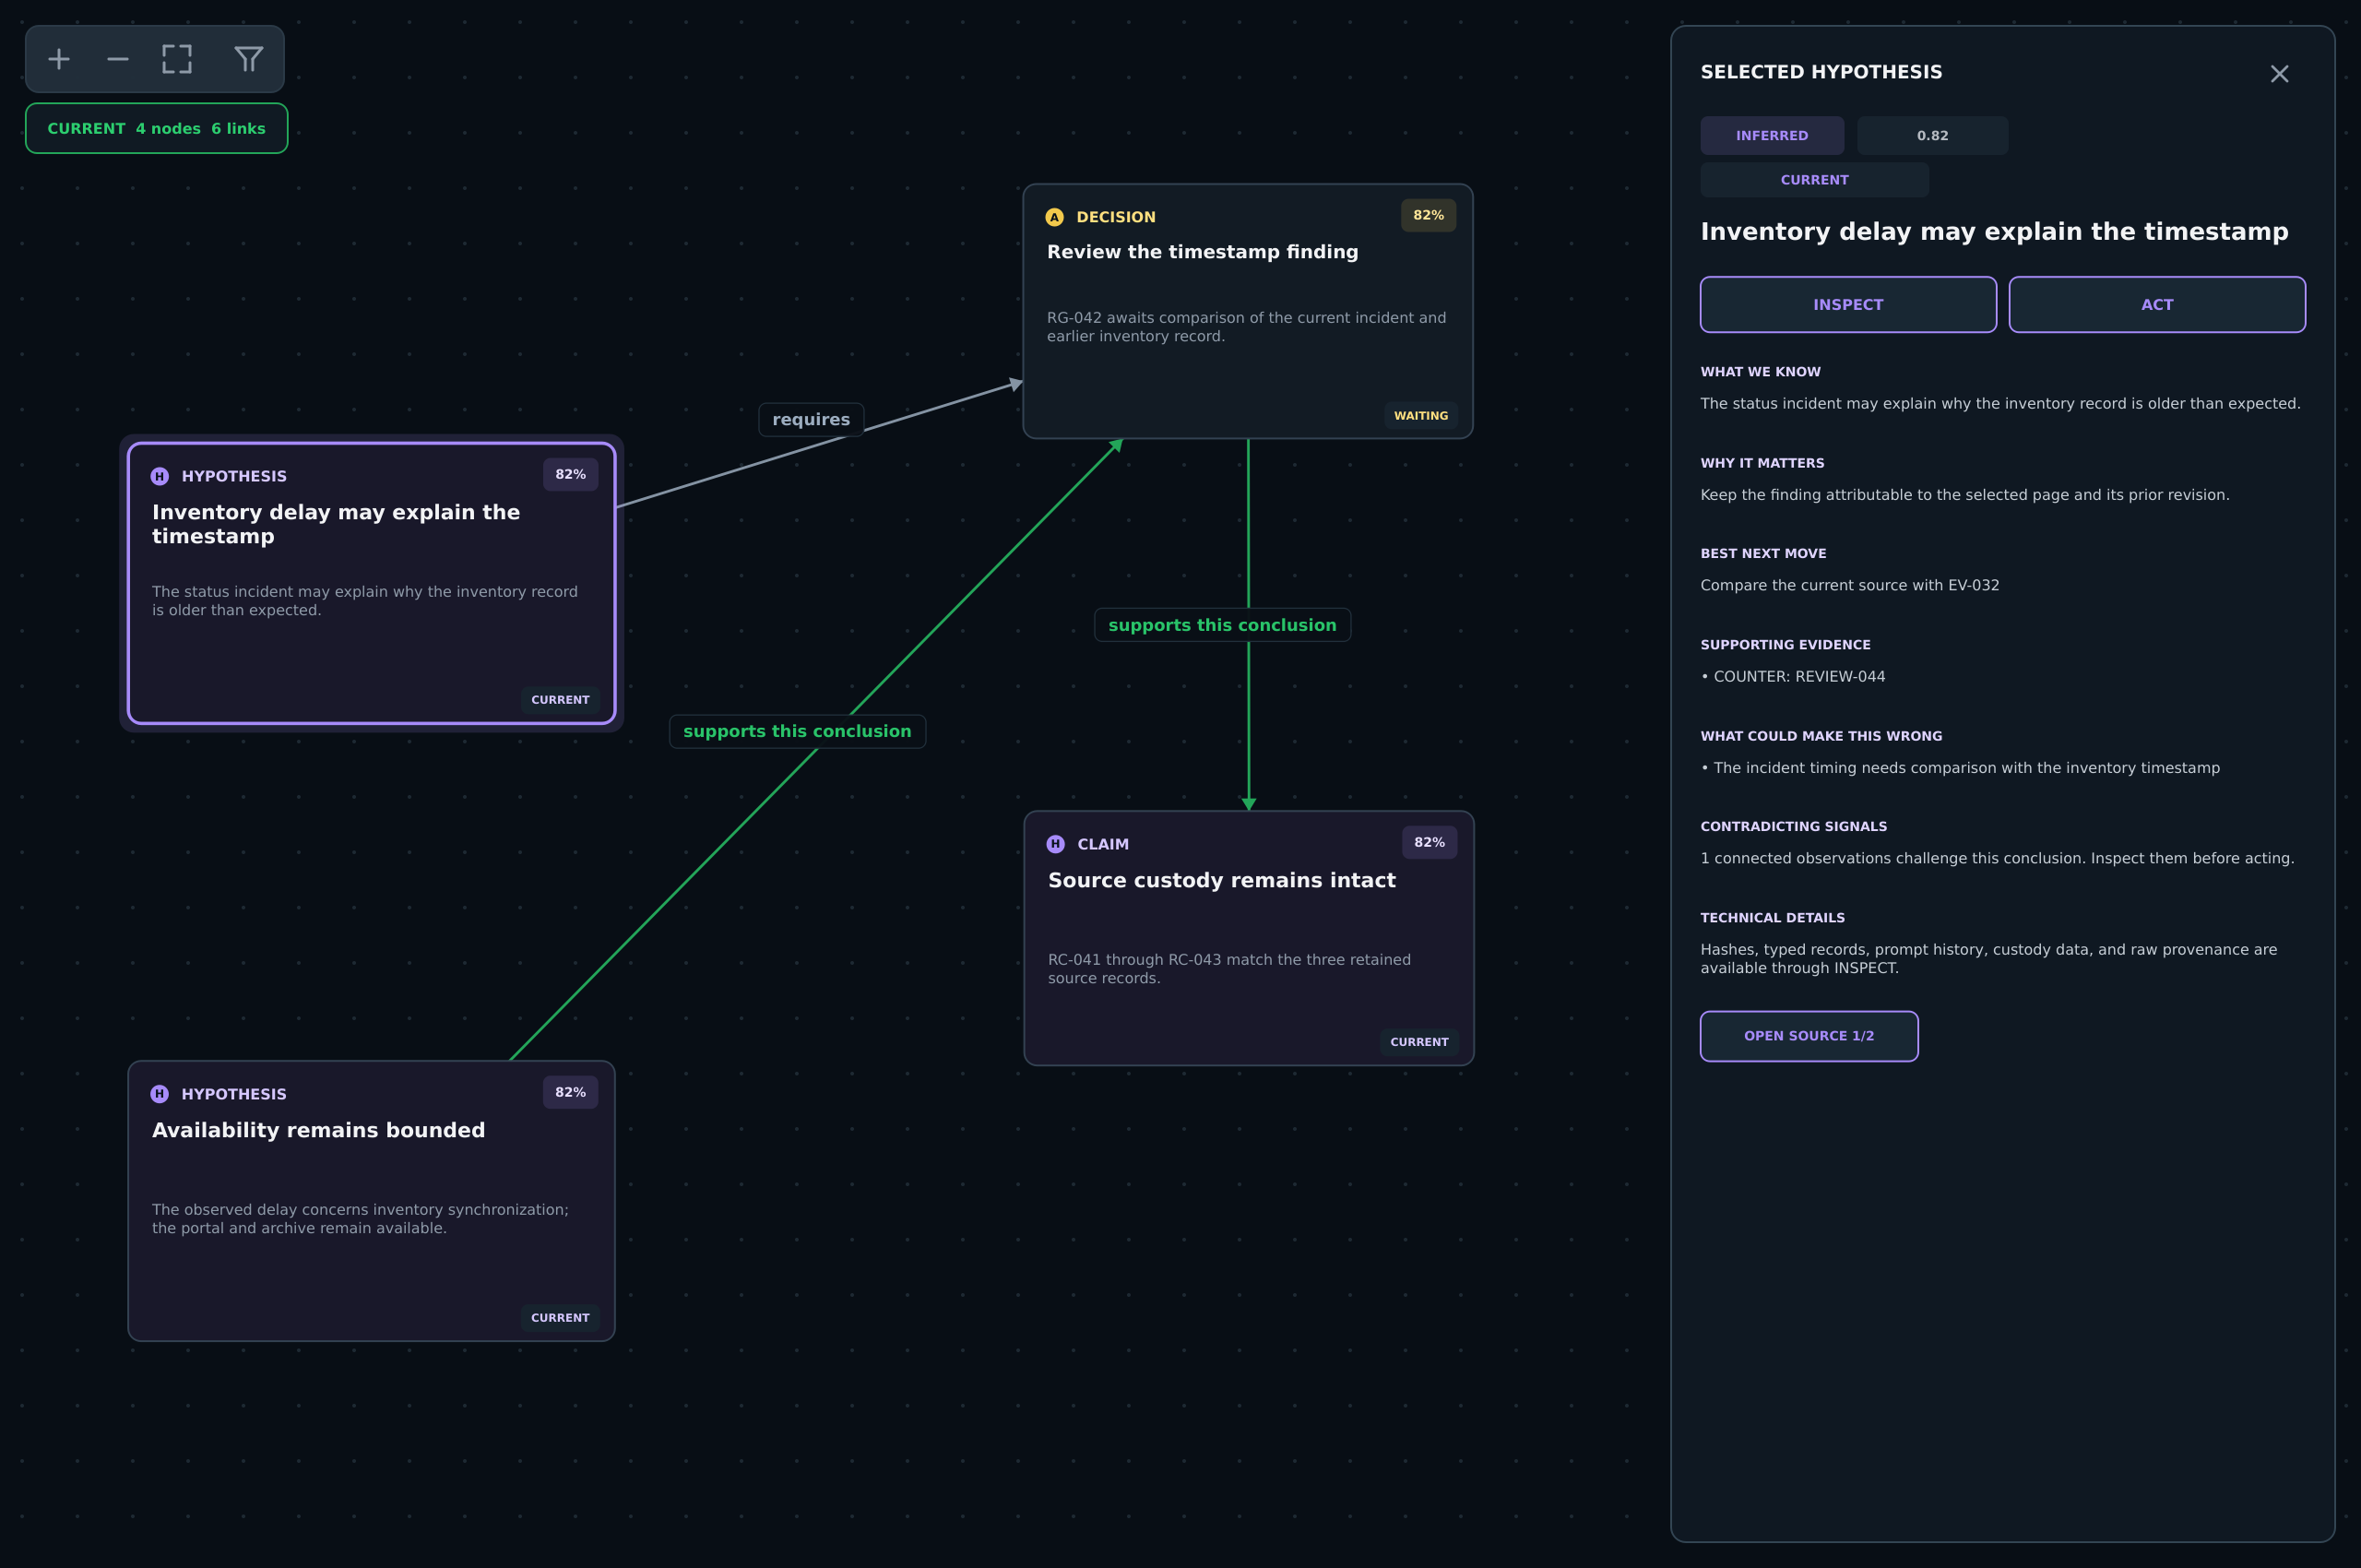
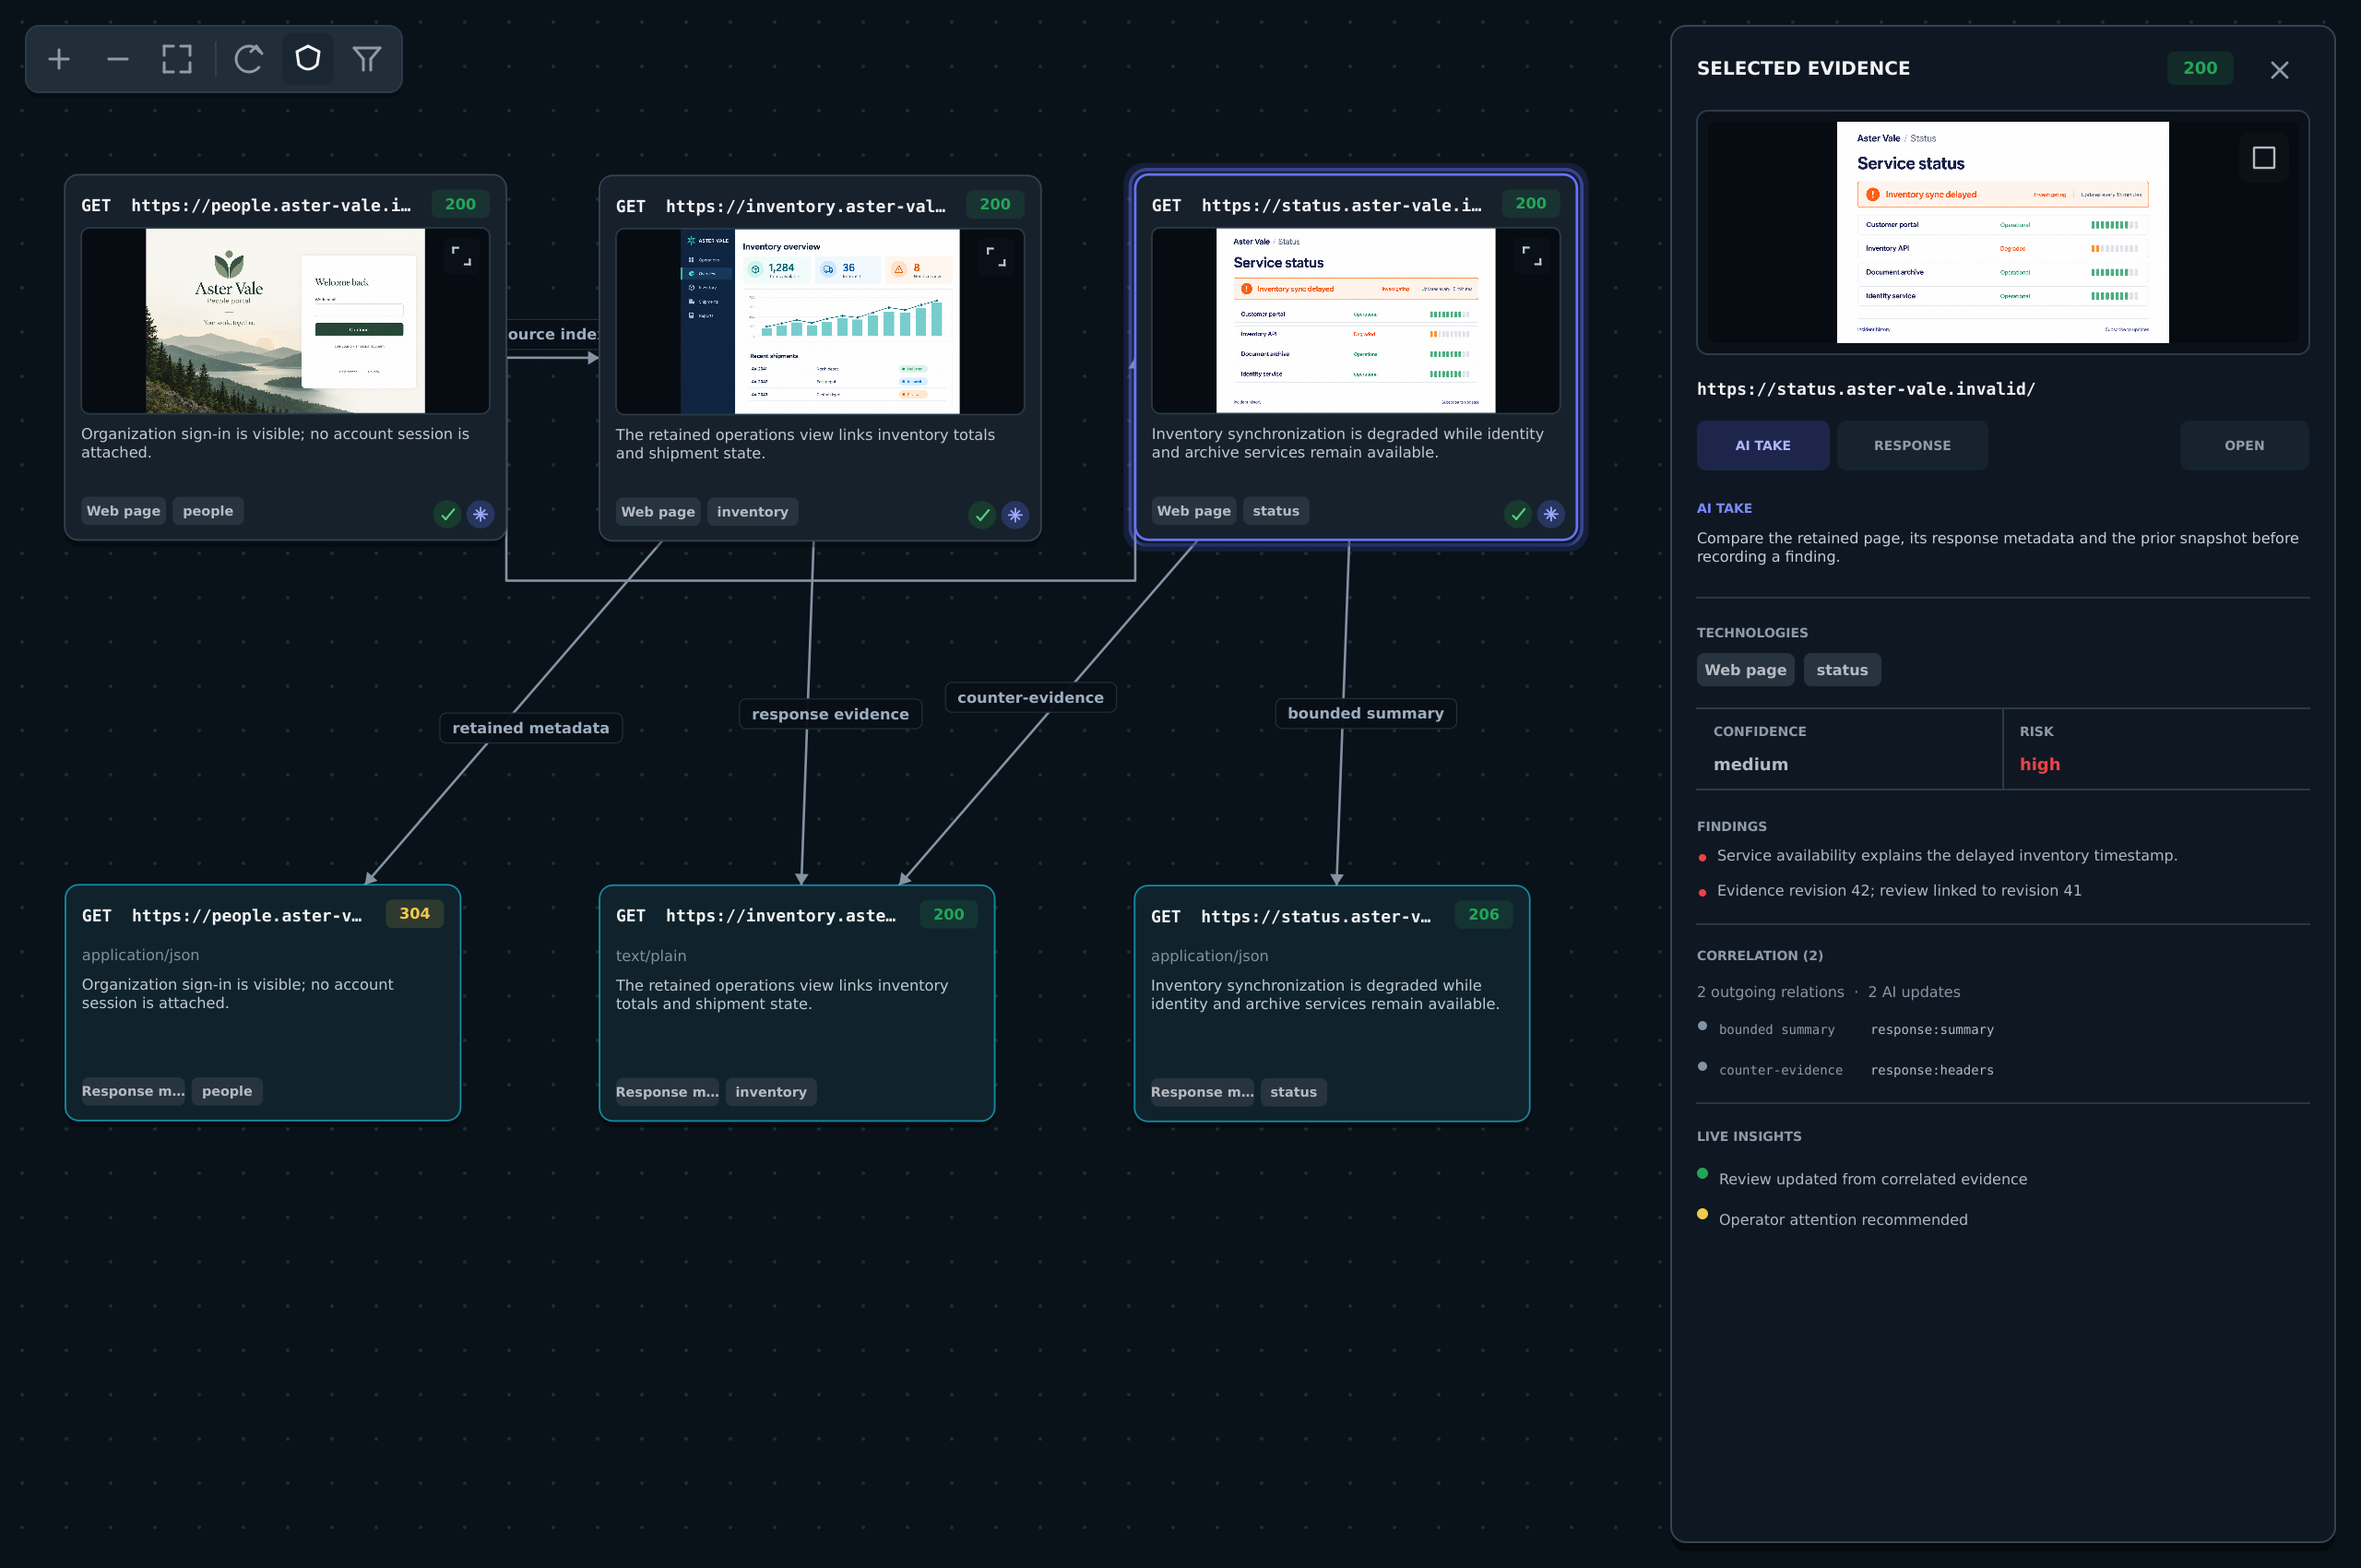
Trace a hypothesis to its observations

Investigation Graph arranges evidence and interpretations as relationships. Detail views retain the source references needed to examine a hypothesis.

Investigation Graph

The graph offers an overview while the workbench carries fuller records. Observations remain distinct from their interpretation.

Native interface
Trace a hypothesis to its observations — operator workspace
Trace each conclusion through support, counter-evidence and review.
Native interface

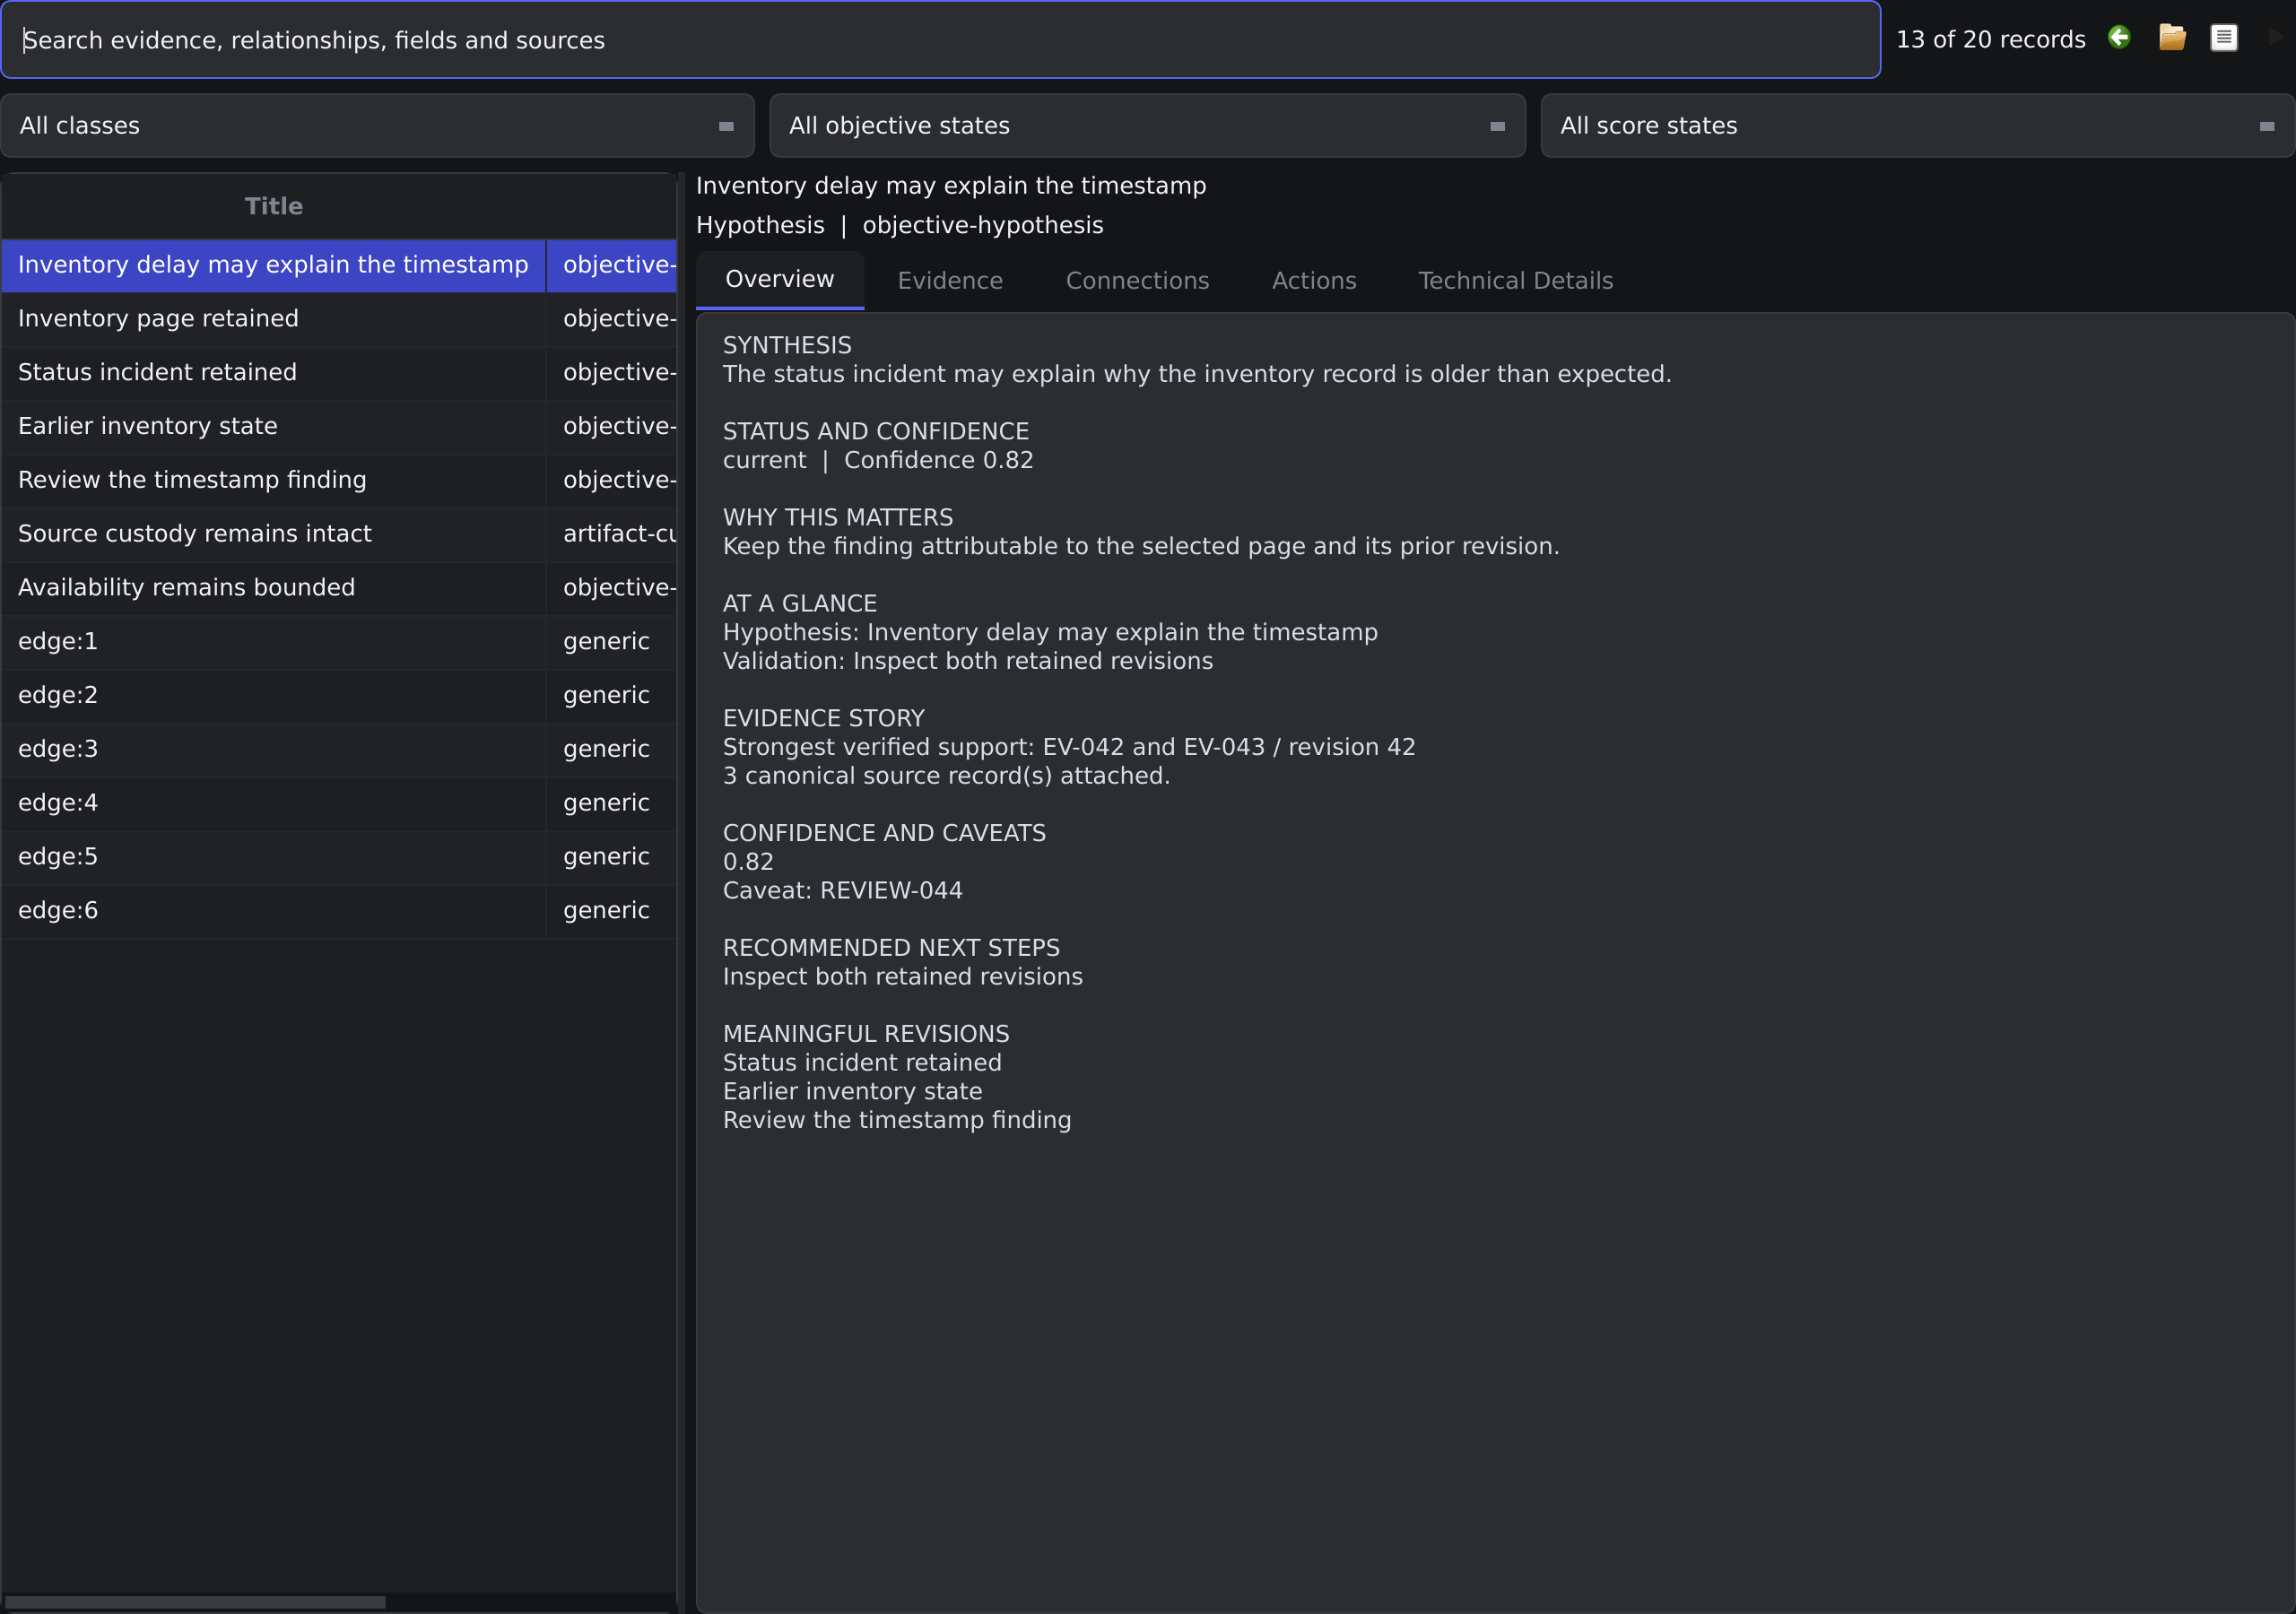
Give difficult evidence room

The Investigation Workbench provides a dedicated surface for source references, context and available continuation. Selection exposes detail without forcing every field into a graph node.

Investigation Workbench

Review source references, competing observations and the current revision together. Open the image to inspect the record in detail.

Native interface
Give difficult evidence room — operator workspace
Compare canonical records and the sources behind the current revision.
Native interface

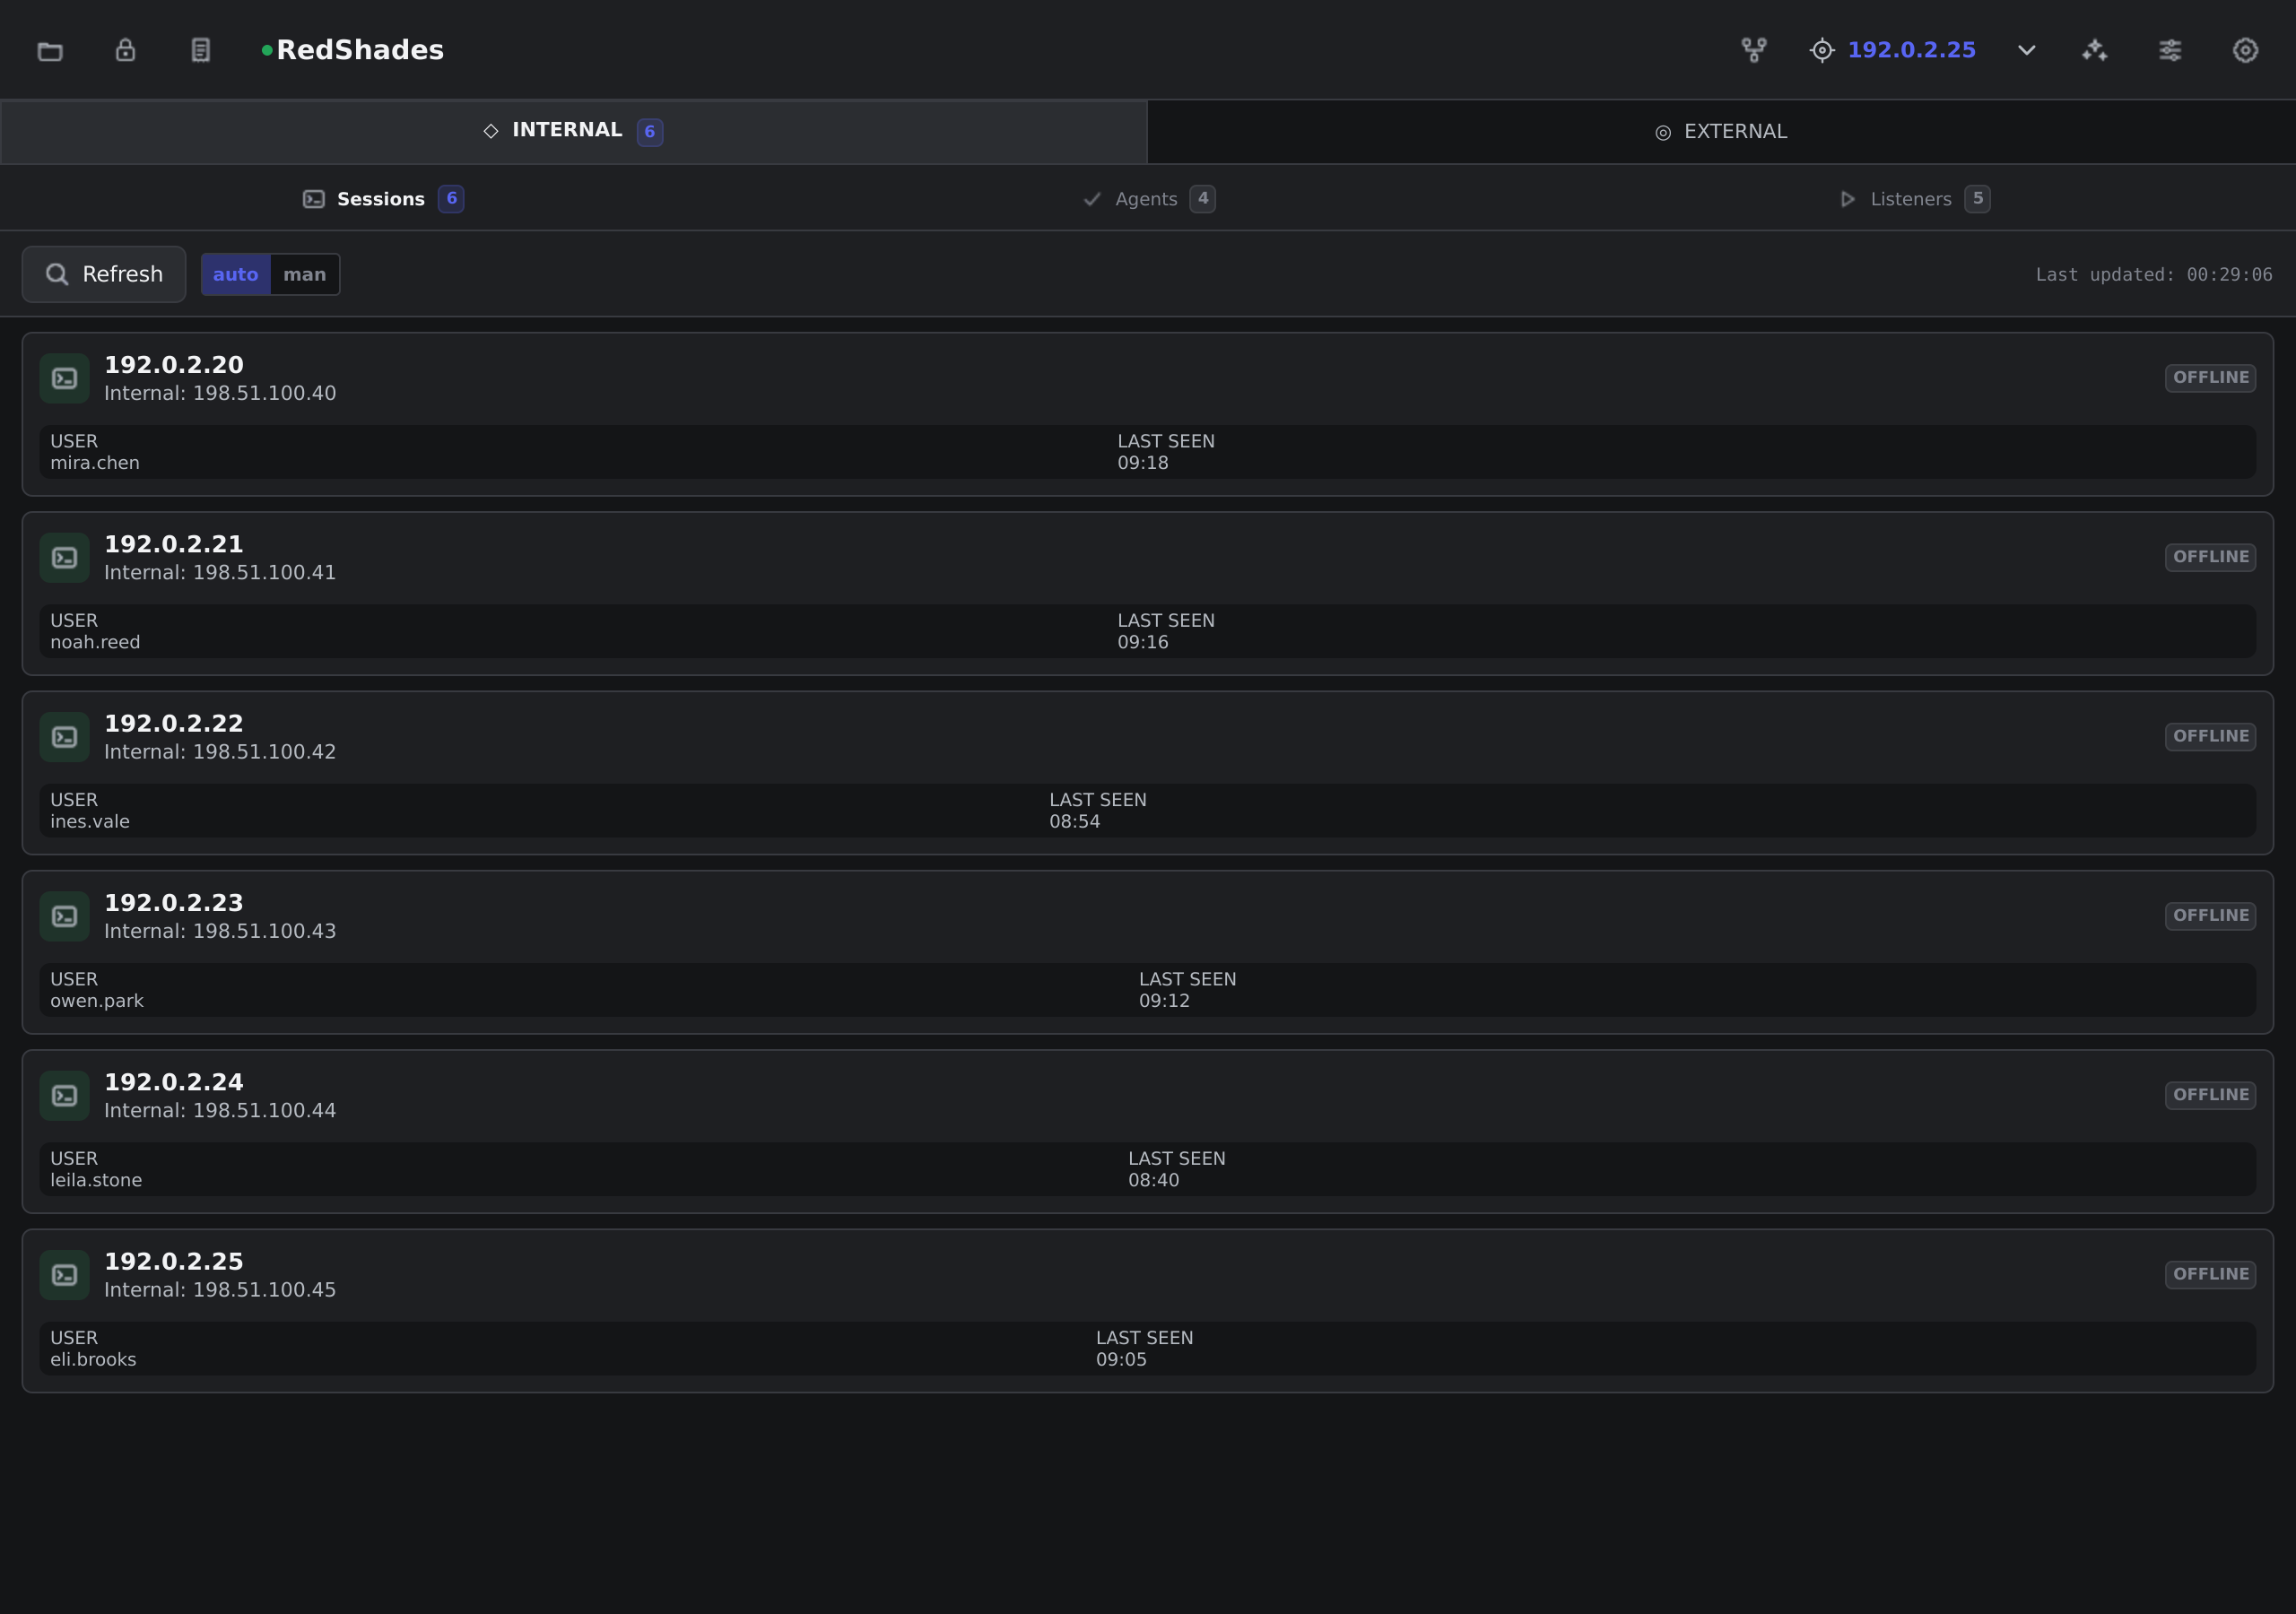
Distinguish a record from availability

Session and artifact views place stored records, versioned builds and observed availability together. Offline and unknown states remain visible alongside selected detail.

Session and artifact surfaces

Host identity, recorded state and artifact history help an operator distinguish stored records from current availability.

Native interface
Distinguish a record from availability — operator workspace
Review host identity and recorded availability before continuing work.
Native interface

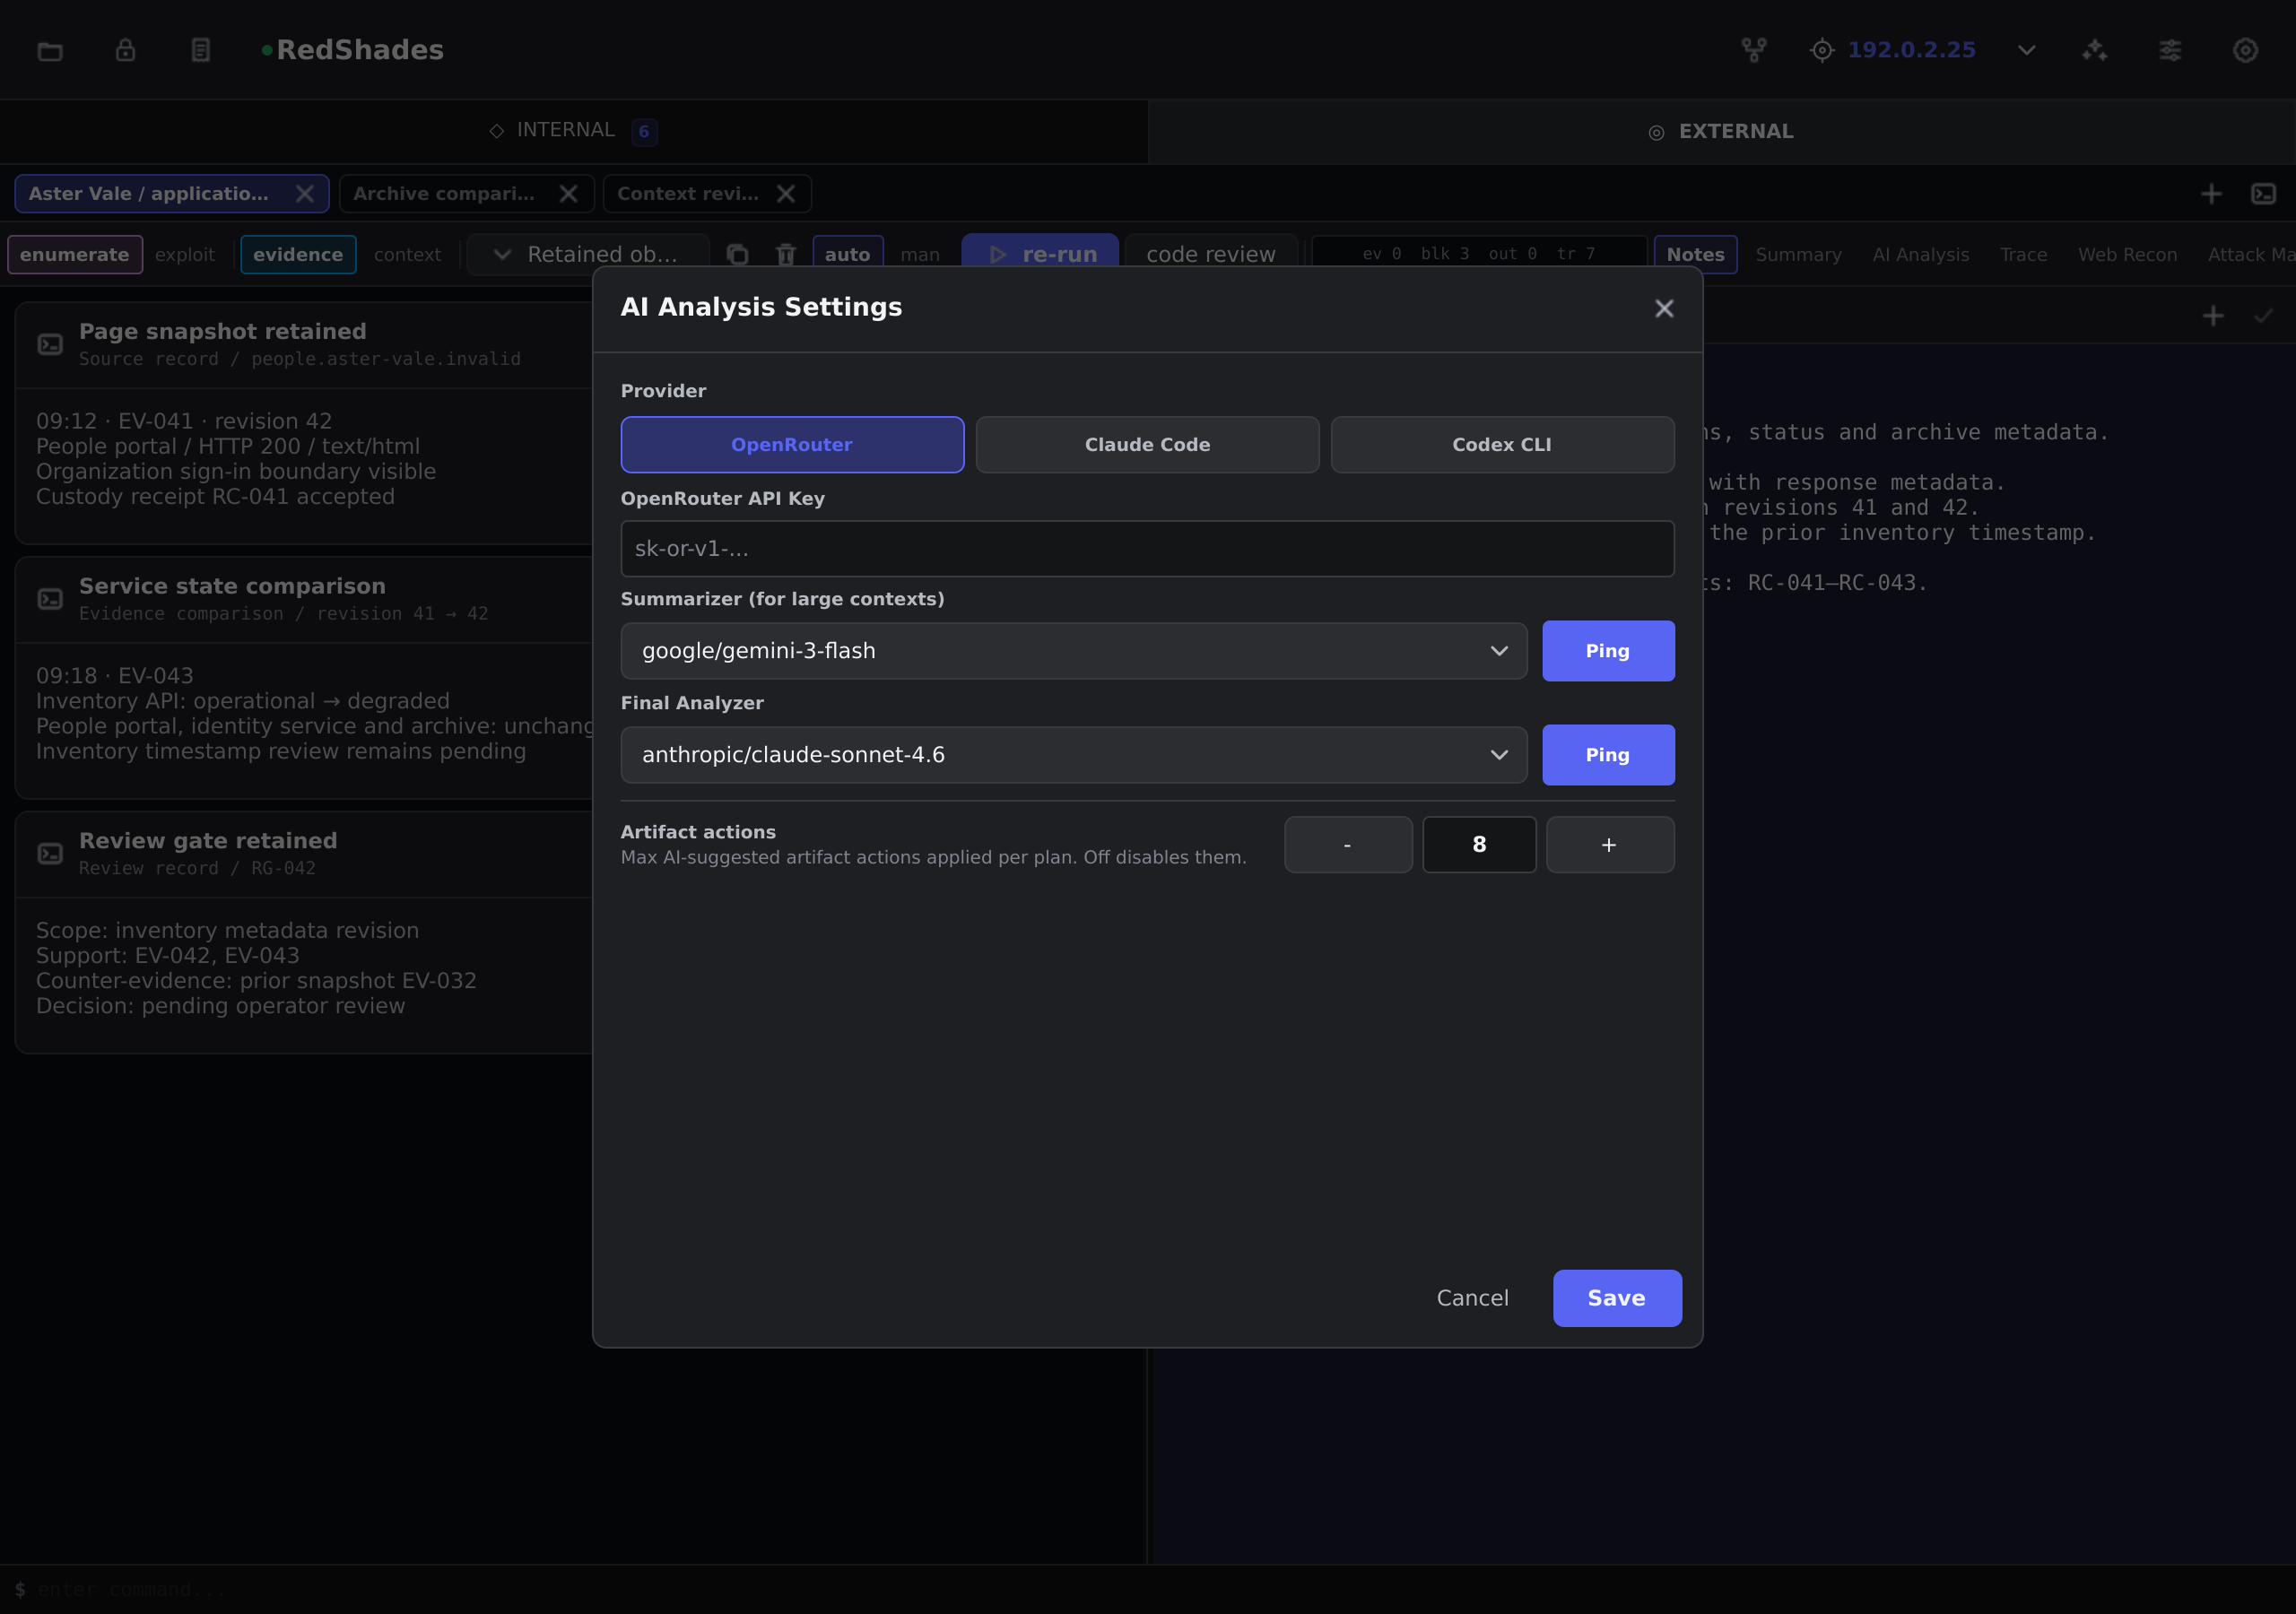
Configuration within reach of the work

Model and runtime controls remain accessible alongside the investigation. They expose the choices an operator needs to review without leaving the native workspace.

Model and runtime controls

Configuration expresses the selected policy. Runtime admission, attribution and accounting establish how that policy is applied.

Native interface
Configuration within reach of the work — operator workspace
Review model selection and bounded provider settings.
Validation and demonstrated outcomes

What the evidence supports

Implemented

Match the claim to the check

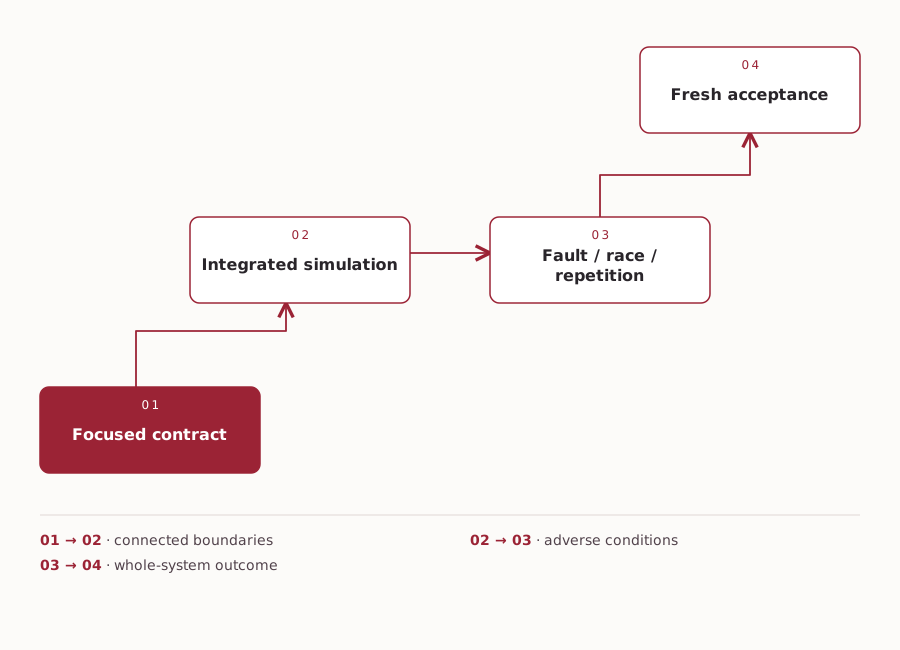
Focused contracts, integrated simulations, race checks, repetition, fuzzing and fault injection examine different failure modes. The Mega and Ultra acceptance suites organize that work.

Verification coverage

Revision-bound receipts connect checks to commands and outputs. A component result supports its tested boundary; whole-system reliability needs integrated evidence.

Implemented
Verification coverage — source-derived relationship diagram
Verification coverage · overview.
Retained study

A vocabulary that can be tested on new material

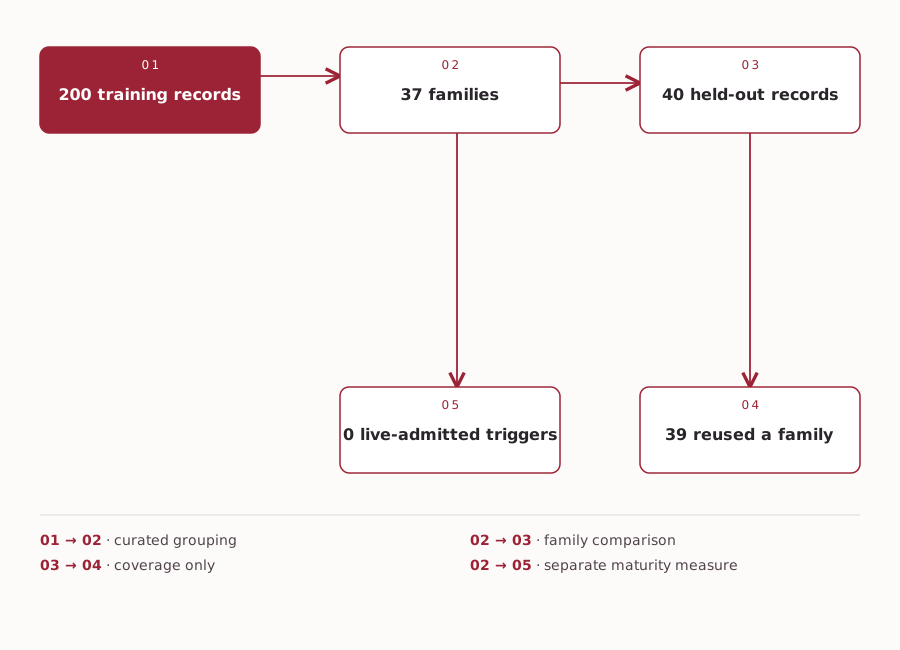
The Trigger Methodology Graph study grouped 200 public disclosures into 37 recurring families. Of 40 identity-disjoint held-out disclosures, 39 belonged to a represented family.

Disclosure study

This measures family coverage in a curated study. It does not count discoveries made by the product. Synthetic calibration recorded 600 activations; no candidates were live-exercised or admitted in the reported study.

Retained study
Disclosure study — source-derived relationship diagram
Disclosure study · overview.
Implemented

A useful hypothesis names the missing fact

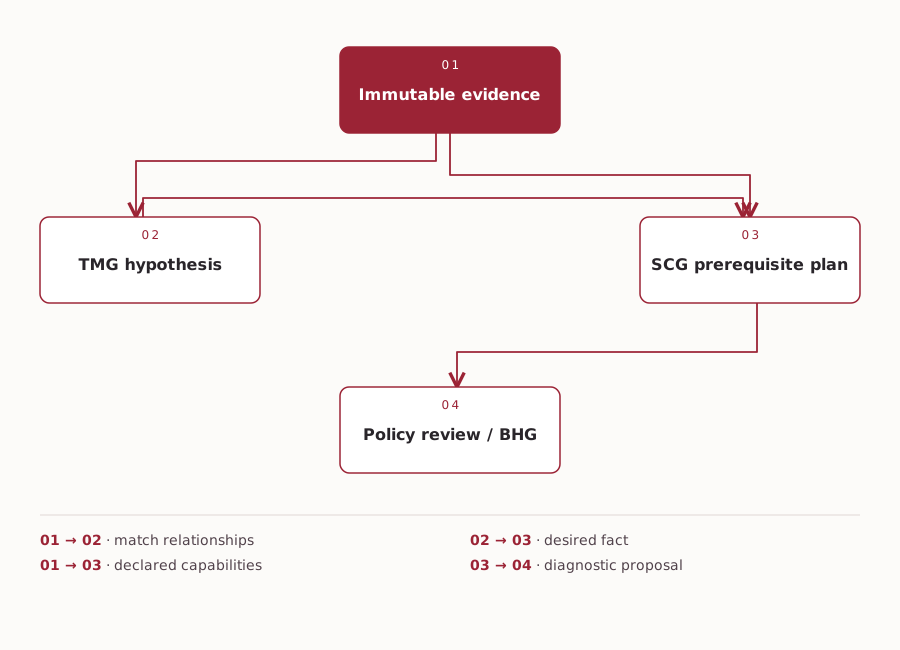
Trigger Methodology Graph produces evidence-bound hypotheses. Shadow Capability Graph examines missing prerequisites from an immutable snapshot. Policy gates retain review over proposed hypotheses.

Evidence-gap analysis

The result identifies uncertainty and the evidence needed to resolve it. A diagnostic suggestion does not acquire scheduling authority.

Implemented
Evidence-gap analysis — source-derived relationship diagram
Evidence-gap analysis · overview.
Evaluation history

An evaluation history across more than 691 CTF labs

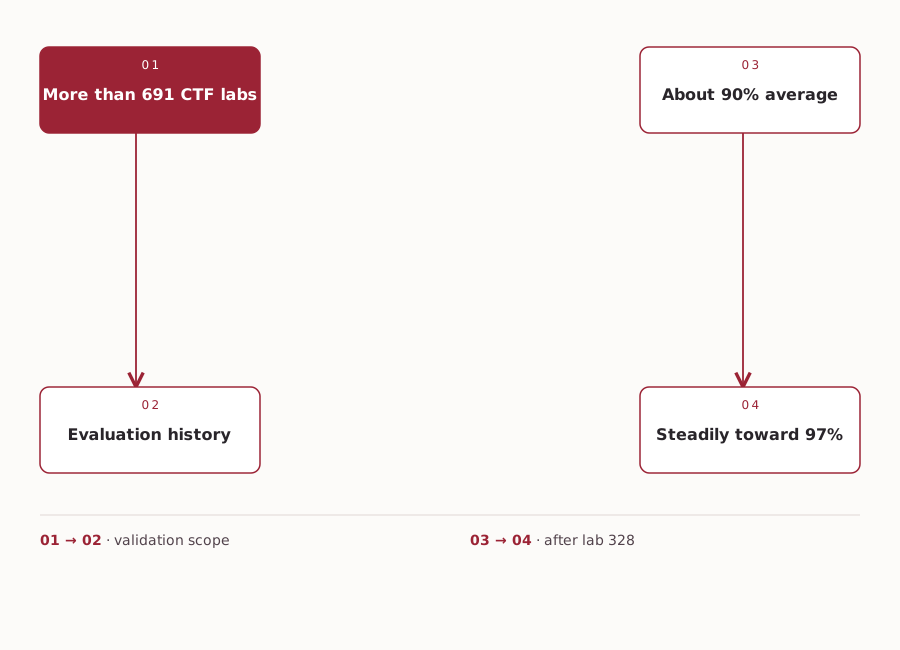
Validation spans more than 691 CTF labs. The learning curve averaged about 90% after lab 328 and rose steadily toward 97%.

CTF validation

Successive evaluations connect model learning with the practical demands of sustained technical work. The history complements the platform’s component, integration and fault-testing program.

Evaluation history
CTF validation — source-derived relationship diagram
CTF validation · overview.
THE AUTOMATIC STAGE ATLAS

The Core, by responsibility

Validated Core

The 88 Core stages are grouped below by the work they contribute. Each has its own evidence requirements; the scheduler selects the path as observations change. Search by name or explore a family.

88 stages
Artifact and session work · 1 stages

Artifacts into recorded context

Versioned material and session records meet here. Admission and observed context determine which responsibilities are available.

Artifact and session workimplant deployment Validated Coreimplant_deployment

implant deployment.

Input class
Admitted artifact and authorized context
Evidence class
Artifact/session records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Directory analysis · 5 stages

Read identity as a set of relationships

Directory observations and graph material support related investigations while preserving their distinct evidence requirements.

Directory analysisACL operator review (post-summary) Validated Coreacl_operator_action

ACL operator review (post-summary).

Input class
Directory evidence and operator review
Evidence class
Review record

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Directory analysisAD compositional capability planning Validated Coread_capability_planning

AD compositional capability planning.

Input class
Directory evidence
Evidence class
Directory analysis records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Directory analysisAD effective capability discovery Validated Coread_capability_discovery

AD effective capability discovery.

Input class
Directory evidence
Evidence class
Directory analysis records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Directory analysisBloodHound collection Validated Corebloodhound_collection

BloodHound collection.

Input class
Directory context
Evidence class
Graph analysis material

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Directory analysisCross-realm Kerberos service-ticket custody Validated Coread_cross_realm_kerberos

Cross-realm Kerberos service-ticket custody.

Input class
Directory evidence
Evidence class
Directory analysis records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Discovery · 4 stages

Establish the surroundings

Network and public-source observations provide the starting context for more specific analysis.

Discoverymasscan discovery Validated Corediscovery_masscan

masscan discovery.

Input class
Scope and observation context
Evidence class
Network observations

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Discoverynmap service and OS scan Validated Corediscovery_nmap

nmap service and OS scan.

Input class
Scope and observation context
Evidence class
Network observations

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Discoverypassive OSINT (WHOIS / DNS / ASN) Validated Coreosint_passive

passive OSINT (WHOIS / DNS / ASN).

Input class
Scope and public observations
Evidence class
Context evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Discoveryquery discovered ports Validated Corediscovery_ports

query discovered ports.

Input class
Scope and observation context
Evidence class
Network observations

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigation · 12 stages

Follow the evidence further

Session and artifact context can make deeper investigation relevant within the engagement’s existing scope.

Extended investigationBloodHound ACL attack path analysis Validated Corepost_acl_analysis

BloodHound ACL attack path analysis.

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationchisel SOCKS5 reverse pivot Validated Corepost_pivot_chisel

chisel SOCKS5 reverse pivot.

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationDCSync domain hash dump Validated Corepost_dcsync

DCSync domain hash dump.

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationDisabled legacy advisory handoff Validated Corepost_nopac

Disabled legacy advisory handoff.

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationDPAPI artifact analysis (operator action) Validated Corepost_dpapi

DPAPI artifact analysis (operator action).

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationFinal assessment report Validated Corepost_pwndoc_export

Final assessment report.

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationLinux privilege escalation enumeration Validated Corepost_linux_privesc

Linux privilege escalation enumeration.

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationpass-the-hash sweep Validated Corepost_pth

pass-the-hash sweep.

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationpass-the-ticket (golden/silver ticket) Validated Corepost_ptt

pass-the-ticket (golden/silver ticket).

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationsecretsdump credential harvest Validated Corepost_secretsdump

secretsdump credential harvest.

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationSMB binary credential extraction Validated Corepost_smb_binary_analysis

SMB binary credential extraction.

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Extended investigationWindows privilege escalation enumeration Validated Corepost_windows_privesc

Windows privilege escalation enumeration.

Input class
Session, artifact or investigation context
Evidence class
Attributed investigation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysis · 16 stages

Resolve who and where

Identity observations travel with their service context so later analysis can distinguish plausible candidates.

Identity analysisAD coercion (PrinterBug/PetitPotam/DFSCoerce) Validated Coreidentity_coerce

AD coercion (PrinterBug/PetitPotam/DFSCoerce).

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysiscertipy AD CS Validated Coreidentity_certipy

certipy AD CS.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysiscertipy AD CS exploitation (ESC1/ESC4/ESC8) Validated Coreidentity_certipy_exploit

certipy AD CS exploitation (ESC1/ESC4/ESC8).

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysisenum4linux-ng Validated Coreidentity_enum4linux

enum4linux-ng.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysisGetNPUsers Validated Coreidentity_getnpusers

GetNPUsers.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysisGetUserSPNs Validated Coreidentity_getuserspns

GetUserSPNs.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysishash cracking Validated Coreidentity_hash_cracking

hash cracking.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysiskerbrute Validated Coreidentity_kerbrute

kerbrute.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysisLAPS password dump Validated Coreidentity_laps

LAPS password dump.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysisldapdomaindump Validated Coreidentity_ldapdomaindump

ldapdomaindump.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysislookupsid Validated Coreidentity_lookupsid

lookupsid.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysisNTLM relay (ntlmrelayx) Validated Coreidentity_ntlm_relay

NTLM relay (ntlmrelayx).

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysisnxc null/guest enumeration Validated Coreidentity_nxc_guest

nxc null/guest enumeration.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysisResponder NTLM hash capture Validated Coreidentity_ntlm_capture

Responder NTLM hash capture.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysistargeted credential spray Validated Coreidentity_credential_spray

targeted credential spray.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Identity analysisusername permutation generation Validated Coreidentity_username_anarchy

username permutation generation.

Input class
Identity and service context
Evidence class
Identity evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Investigation · 1 stages

Investigation

Scoped observations determine which work is eligible.

Investigationcredential reuse sweep Validated Corecredential_reuse_sweep

credential reuse sweep.

Input class
Scoped evidence
Evidence class
Attributed records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Platform adaptation · 1 stages

Fit the observed environment

Platform context informs adaptation work without turning one environment into a permanent default.

Platform adaptationExecution context: network path and domain time Validated Coreenvironment_adaptation

Execution context: network path and domain time.

Input class
Environment context
Evidence class
Adaptation records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Remote services · 6 stages

Give each protocol its own context

Service-specific work shares the engagement record while retaining the evidence particular to each protocol.

Remote servicesconditional mssqlclient Validated Coreremote_mssqlclient

conditional mssqlclient.

Input class
Service and authorized session context
Evidence class
Protocol evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Remote servicesconditional smbclient Validated Coreremote_smbclient

conditional smbclient.

Input class
Service and authorized session context
Evidence class
Protocol evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Remote servicesKerberos ticket-backed WinRM validation Validated Coreremote_kerberos_winrm

Kerberos ticket-backed WinRM validation.

Input class
Service and authorized session context
Evidence class
Protocol evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Remote servicesMSSQL linked server ADIDNS poisoning Validated Coremssql_linked_server_poison

MSSQL linked server ADIDNS poisoning.

Input class
Database context
Evidence class
Database evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Remote servicesSMB file harvest Validated Coreremote_smb_harvest

SMB file harvest.

Input class
Service and authorized session context
Evidence class
Protocol evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Remote servicessmbmap share enumeration Validated Coreremote_smbmap

smbmap share enumeration.

Input class
Service and authorized session context
Evidence class
Protocol evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Reporting · 1 stages

Bring the findings back together

The report draws on retained investigation evidence and its attribution.

Reportingdeterministic operator report Validated Coresummary

deterministic operator report.

Input class
Retained investigation evidence
Evidence class
Report projection

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysis · 13 stages

Characterize the exposed service

Observed services supply the inputs for more precise analysis and interpretation.

Service analysisDNS zone transfer drill Validated Coreservice_dns_axfr

DNS zone transfer drill.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisdnsx Validated Coreservice_dnsx

dnsx.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisFTP anonymous Validated Coreservice_ftp_anon

FTP anonymous.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisIPMI enumeration and hash extraction Validated Coreservice_ipmi

IPMI enumeration and hash extraction.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisMySQL probe Validated Coreservice_mysql

MySQL probe.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisNFS enumeration Validated Coreservice_nfs

NFS enumeration.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisRedis enumeration Validated Coreservice_redis

Redis enumeration.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisservice CVE candidate sweep Validated Coreservice_searchsploit_sweep

service CVE candidate sweep.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisservice CVE workbench Validated Coreservice_cve_workbench

service CVE workbench.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisSMTP user enumeration Validated Coreservice_smtp_user_enum

SMTP user enumeration.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisSNMP enumeration Validated Coreservice_snmp_enum

SNMP enumeration.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysisssh-audit Validated Coreservice_ssh_audit

ssh-audit.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Service analysissubfinder Validated Coreservice_subfinder

subfinder.

Input class
Service observations
Evidence class
Service evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Session work · 2 stages

Continue from a known session

Available interaction and remote desktop work depend on an authorized execution context.

Session workcredential to shell attempts Validated Coreshell_attempts

credential to shell attempts.

Input class
Authorized execution context
Evidence class
Session-related records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Session workxfreerdp RDP session Validated Corerdp_session

xfreerdp RDP session.

Input class
Authorized session context
Evidence class
Session records

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigation · 26 stages

Follow the web surface in detail

Web observations and scoped reviews support related branches. Each responsibility retains its own inputs and output evidence.

Web investigationCMS scanning Validated Coreweb_cms_scan

CMS scanning.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationCMS/app-server RCE (Tomcat/Jenkins/Drupal) Validated Coreweb_cms_exploit

CMS/app-server RCE (Tomcat/Jenkins/Drupal).

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationCVE PoC workbench review Validated Coreweb_cve_poc_workbench

CVE PoC workbench review.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationGoWitness endpoint review Validated Coreweb_screenshot

GoWitness endpoint review.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationHTTP verb tampering Validated Coreweb_verb_tampering

HTTP verb tampering.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationIDOR / parameter enumeration Validated Coreweb_idor_probe

IDOR / parameter enumeration.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationLFI exploitation Validated Coreweb_lfi_exploit

LFI exploitation.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationnuclei parallel Validated Coreweb_nuclei

nuclei parallel.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationOS command injection probe Validated Coreweb_cmdi_probe

OS command injection probe.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationpost-auth CVE PoC workbench review Validated Coreweb_post_auth_poc_workbench

post-auth CVE PoC workbench review.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationpost-auth exploit probes Validated Coreweb_post_auth_exploit_probes

post-auth exploit probes.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationpost-auth surface harvest Validated Coreweb_post_auth_harvest

post-auth surface harvest.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationSQLi OS shell (--os-cmd / --os-shell) Validated Coreweb_sqli_post_exploit

SQLi OS shell (--os-cmd / --os-shell).

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationSQLi probe Validated Coreweb_sqli_probe

SQLi probe.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationSSTI probe Validated Coreweb_ssti_probe

SSTI probe.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationtarget-specific password generation Validated Coreweb_cewl

target-specific password generation.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationweb content analysis Validated Coreweb_content_analysis

web content analysis.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationweb file upload attack Validated Coreweb_file_upload_attack

web file upload attack.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationweb fingerprint + wafw00f Validated Coreweb_whatweb_waf

web fingerprint + wafw00f.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationweb fuzzing (vhost+dir+ext) Validated Coreweb_fuzz

web fuzzing (vhost+dir+ext).

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationweb login brute force Validated Coreweb_login_bruteforce

web login brute force.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationweb RCE candidate correlation Validated Coreweb_rce_candidate_correlation

web RCE candidate correlation.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationweb RCE confirmation Validated Coreweb_rce_confirm

web RCE confirmation.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationweb RCE deployment preparation Validated Coreweb_rce_deployment_prepare

web RCE deployment preparation.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationXSS probe Validated Coreweb_xss_probe

XSS probe.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage
Web investigationXXE probe Validated Coreweb_xxe_probe

XXE probe.

Input class
Web observations and scoped review
Evidence class
Web evidence

Returns attributed results to the scheduler; eligibility remains policy and evidence dependent.

Link to stage

Stage families group related responsibilities. Results retain their source attribution and return to evidence-driven scheduling.

13 C2 CONTINUATION STAGES

Session work follows platform-specific branches

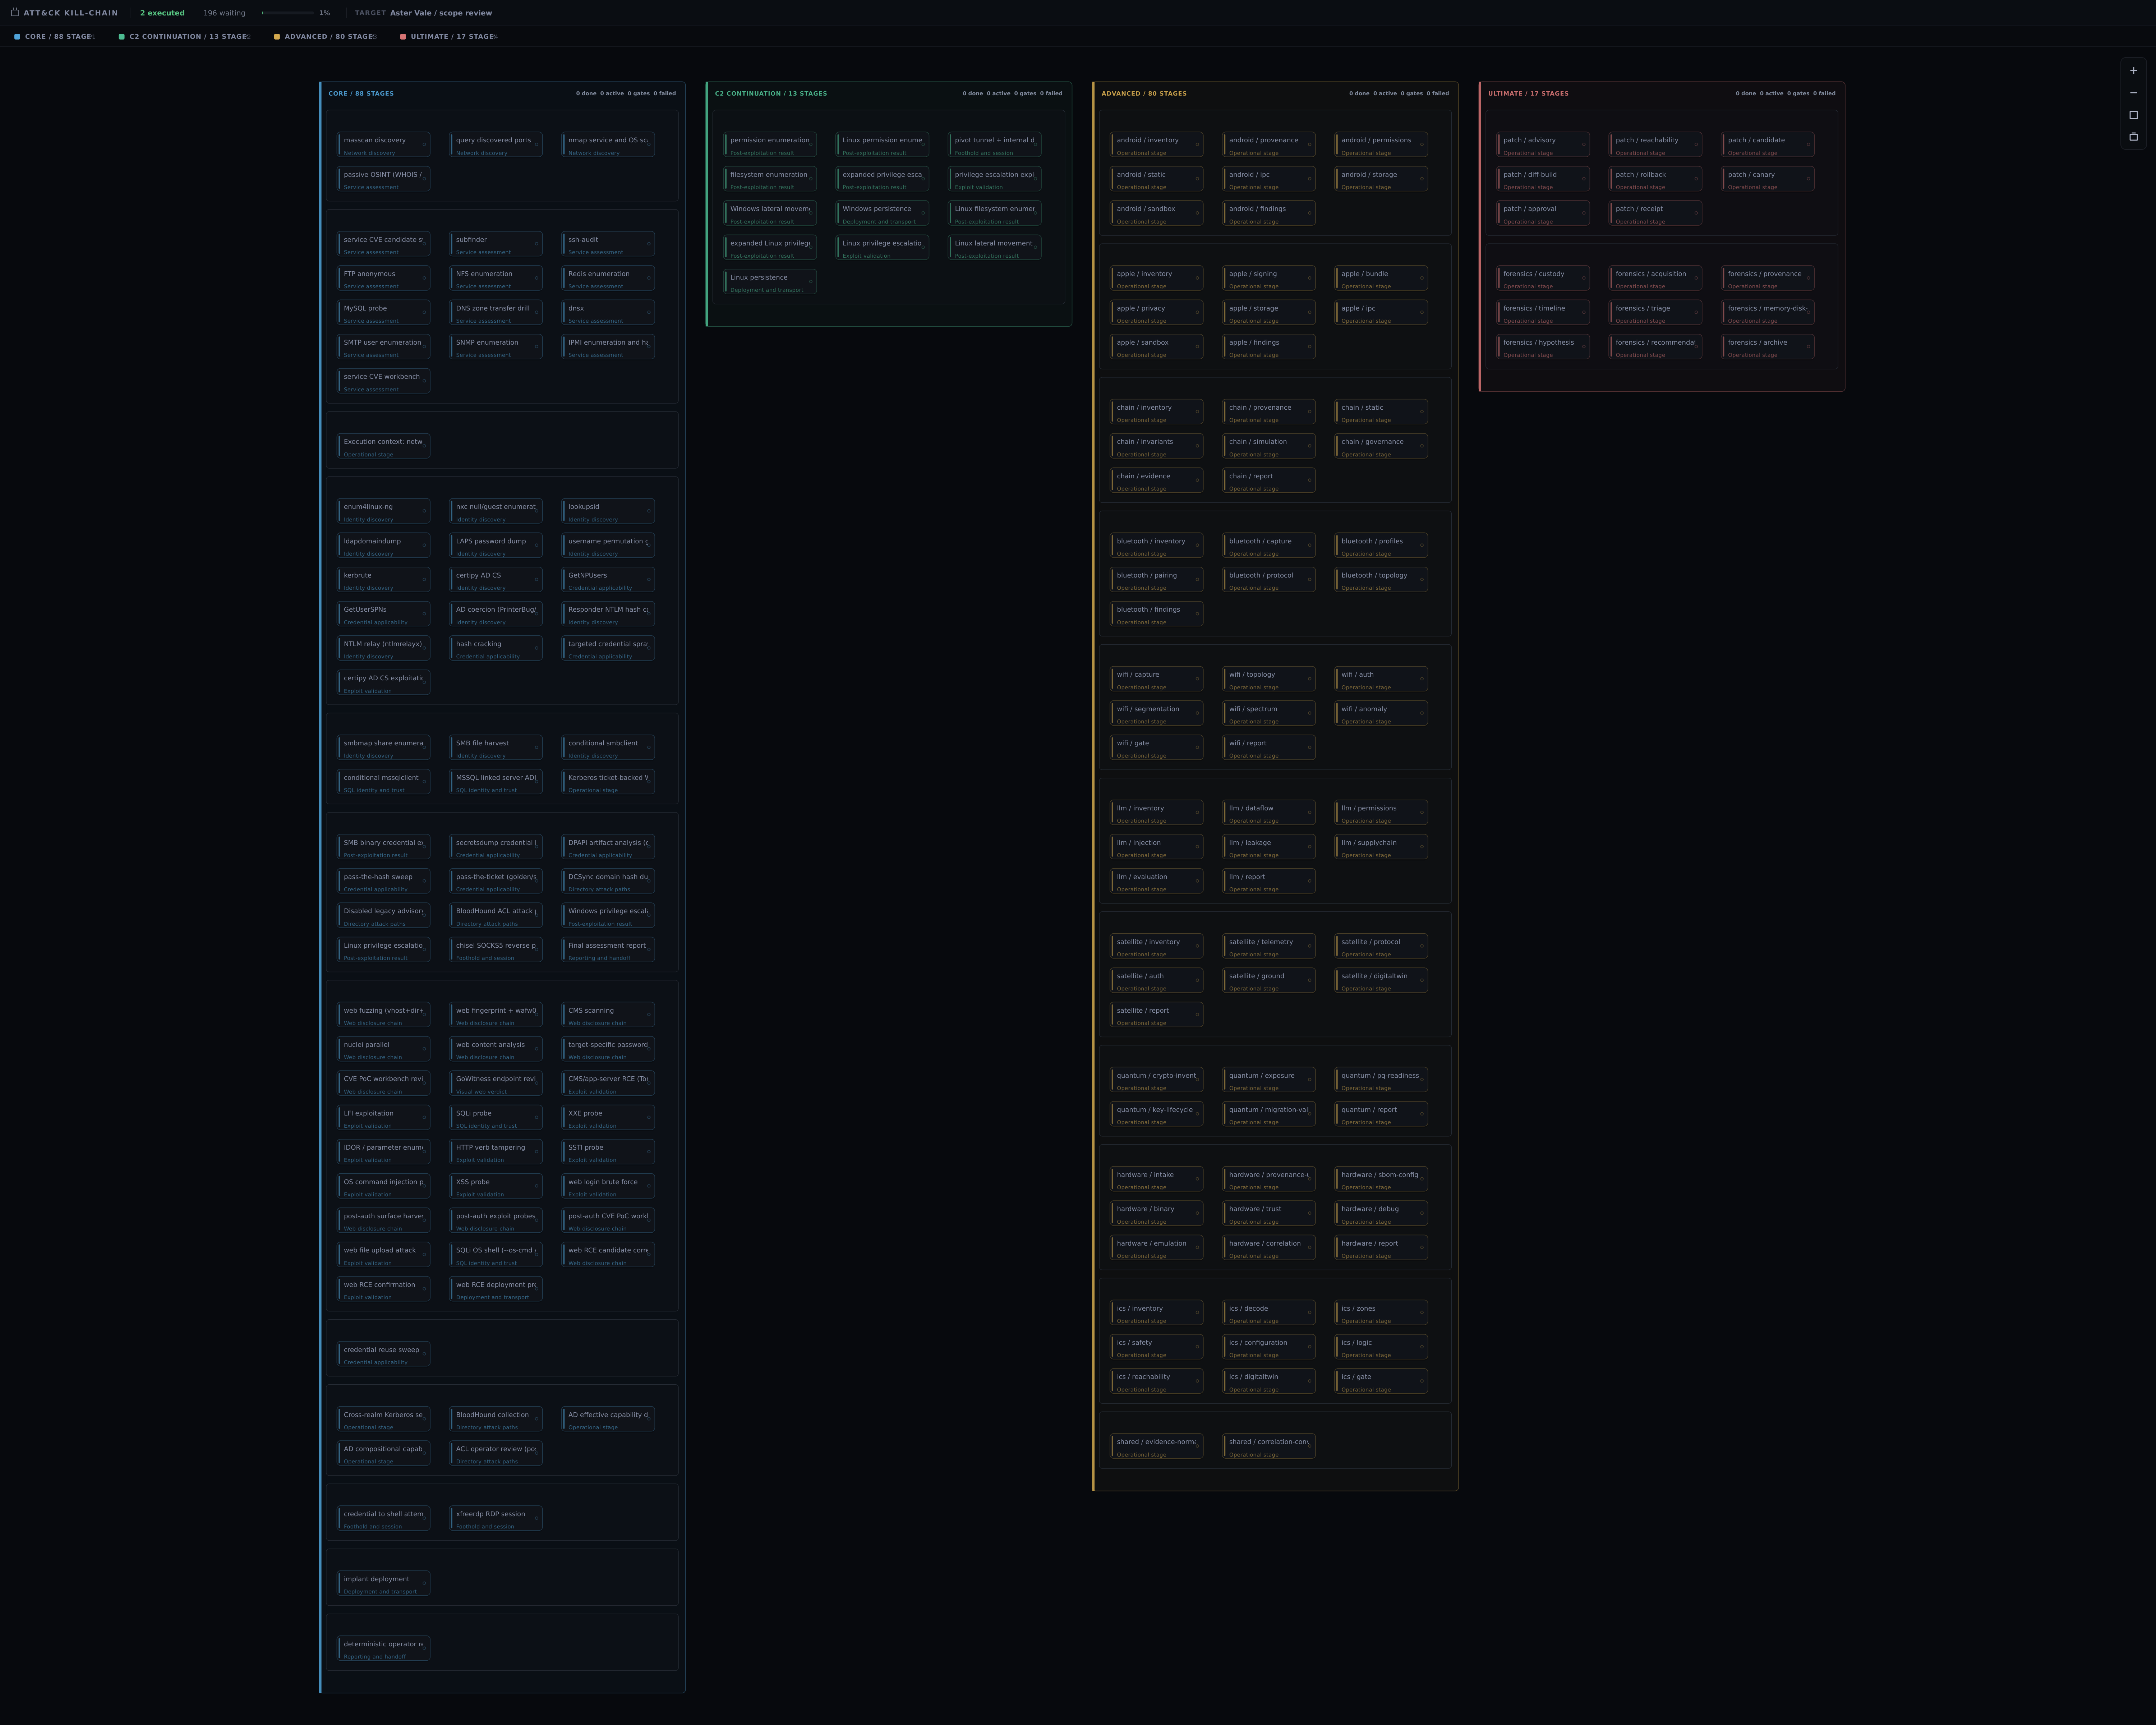
The C2 continuation inventory adds 13 stages to the 88-stage Validated Core. Registered session context determines the applicable Windows, Linux and shared work. These stages are included in the 198-stage catalog total.

permission enumerationwindowswindows_permission_enum
Linux permission enumerationlinuxlinux_permission_enum
pivot tunnel + internal discoveryCross-platformpivot_tunnel
filesystem enumerationwindowswindows_filesystem_enum
expanded privilege escalation enumerationwindowswindows_privilege_escalation
privilege escalation exploitationwindowswindows_privilege_escalation_exploit
Windows lateral movementwindowswindows_lateral_movement
Windows persistencewindowswindows_persistence
Linux filesystem enumerationlinuxlinux_filesystem_enum
expanded Linux privilege escalation enumerationlinuxlinux_privilege_escalation
Linux privilege escalation exploitationlinuxlinux_privilege_escalation_exploit
Linux lateral movementlinuxlinux_lateral_movement
Linux persistencelinuxlinux_persistence
IMPLEMENTATION PROVENANCE

Own the integration. Credit the components.

Custom implementation

RedShades stage orchestration, evidence records, native operator views, ACP and AEP connect the workspace through shared state.

Vendored

Nuclei, gowitness, Cutter, Qiling and ILSpy; Ghidra and JADX MCP integration components. These open-source components retain their respective licenses and attribution.

97 EXPANSION STAGES · SHARED CAPABILITIES

Expansion builds on shared components

The expansion architecture contains 48 descriptors: 37 potential third-party package candidates, one external Apple toolchain and ten built-in or custom RedShades components. These are architecture entries, not 48 installed tools.

Domain counts include primary and alternative components and overlap through reuse. The evidence graph and reporting each serve all 12 domains; artifact intake serves 11. Cosign, Wireshark and Zeek each appear in five domains.

Cluster → capability → shared tool architecture
Domain clusterAnalysis capabilitiesPrimary and alternative components
Android / mobile8 stages · 10 referenced entriesartifact intake · provenance custody · configuration review · static analysis · topology modeling · evidence correlation · emulation simulation · reportingAndroguard · Apktool · Android bundletool · Cosign · JADX · Mobile Security Framework · RedShades artifact intake · RedShades typed evidence graph · RedShades policy and effect gate · RedShades evidence-backed reporting
Apple platforms8 stages · 8 referenced entriesartifact intake · provenance custody · binary decomposition · configuration review · static analysis · topology modeling · emulation simulation · reportingipsw · LLVM binary utilities · RedShades artifact intake · RedShades typed evidence graph · RedShades policy and effect gate · RedShades privacy/data-flow model · RedShades evidence-backed reporting · Apple codesign/security toolchain
Blockchain8 stages · 8 referenced entriesartifact intake · provenance custody · static analysis · evidence correlation · emulation simulation · topology modeling · reportingCosign · Echidna · Foundry · RedShades artifact intake · RedShades typed evidence graph · RedShades evidence-backed reporting · Slither · Solidity compiler
Bluetooth / BLE / NFC7 stages · 8 referenced entriesartifact intake · passive capture parsing · configuration review · evidence correlation · topology modeling · reportingBlueZ btmon · libnfc utilities · RedShades artifact intake · RedShades typed evidence graph · RedShades protocol observation normalizer · RedShades evidence-backed reporting · Wireshark/TShark · Zeek
Wi-Fi / RF8 stages · 9 referenced entriesartifact intake · topology modeling · passive capture parsing · static analysis · evidence correlation · policy gating · reportingGNU Radio · RedShades artifact intake · RedShades typed evidence graph · RedShades policy and effect gate · RedShades protocol observation normalizer · RedShades evidence-backed reporting · Suricata · Wireshark/TShark · Zeek
LLM / AI systems8 stages · 10 referenced entriesartifact intake · topology modeling · configuration review · emulation simulation · evidence correlation · supply chain analysis · reportinggarak · Inspect AI · OSV-Scanner · RedShades artifact intake · RedShades typed evidence graph · RedShades policy and effect gate · RedShades privacy/data-flow model · RedShades evidence-backed reporting · Syft · Trivy
Satellite / space7 stages · 10 referenced entriesartifact intake · passive capture parsing · configuration review · topology modeling · emulation simulation · reportingGNU Radio · gr-satellites · Orekit · RedShades artifact intake · RedShades typed evidence graph · RedShades protocol observation normalizer · RedShades evidence-backed reporting · RedShades OT/space safety model · Wireshark/TShark · Zeek
Quantum readiness6 stages · 6 referenced entriescryptographic inventory · evidence correlation · configuration review · topology modeling · emulation simulation · reportingCirq · Qiskit SDK · RedShades artifact intake · RedShades cryptographic evidence normalizer · RedShades typed evidence graph · RedShades evidence-backed reporting
Hardware / firmware9 stages · 11 referenced entriesartifact intake · binary decomposition · supply chain analysis · static analysis · configuration review · evidence correlation · emulation simulation · reportingBinwalk · Cosign · Ghidra · ipsw · LLVM binary utilities · QEMU · RedShades artifact intake · RedShades typed evidence graph · RedShades evidence-backed reporting · Syft · Trivy
ICS / SCADA9 stages · 11 referenced entriesartifact intake · passive capture parsing · topology modeling · safety modeling · configuration review · static analysis · evidence correlation · emulation simulation · policy gatingOpenSCAP · QEMU · RedShades artifact intake · RedShades typed evidence graph · RedShades policy and effect gate · RedShades protocol observation normalizer · RedShades evidence-backed reporting · RedShades OT/space safety model · Suricata · Wireshark/TShark · Zeek
Defensive patching8 stages · 9 referenced entriessupply chain analysis · evidence correlation · static analysis · reporting · policy gatingCosign · Grype · OSV-Scanner · RedShades typed evidence graph · RedShades defensive change planner · RedShades policy and effect gate · RedShades evidence-backed reporting · Syft · Trivy
Digital forensics9 stages · 12 referenced entriesprovenance custody · artifact intake · forensic analysis · evidence correlation · reportingCosign · Plaso · RedShades artifact intake · RedShades typed evidence graph · RedShades policy and effect gate · RedShades evidence-backed reporting · The Sleuth Kit · Velociraptor · Volatility 3 · Wireshark/TShark · YARA · Zeek
Shared Advanced helpers2 stages · 3 referenced entriesevidence correlationRedShades artifact intake · RedShades typed evidence graph · RedShades evidence-backed reporting

47 entries are referenced directly by stages; the remaining workflow router is a shared foundation. Specialist packaging and validation are pending. License badges identify upstream terms; redistribution review applies before packaging.

SPECIALIST TOOL ARCHITECTURE

Tool classifications and license sources

48 distinct tool and native component entries support the expansion architecture. Reuse connects domain-specific work to common evidence, parsing, analysis and reporting capabilities.

Specialist integrations are under testing or development. Packaging and admission remain pending for these expansion entries.

RedShades artifact intakeBuilt-in RedShades

LicenseRef-REDC2-Internal

artifact intake · provenance custody

Packaging pending · Validation pending

RedShades typed evidence graphBuilt-in RedShades

LicenseRef-REDC2-Internal

evidence correlation · topology modeling

Packaging pending · Validation pending

RedShades policy and effect gateBuilt-in RedShades

LicenseRef-REDC2-Internal

policy gating · safety modeling

Packaging pending · Validation pending

RedShades evidence-backed reportingBuilt-in RedShades

LicenseRef-REDC2-Internal

reporting

Packaging pending · Validation pending

RedShades typed workflow routerBuilt-in RedShades

LicenseRef-REDC2-Internal

policy gating · evidence correlation

Packaging pending · Validation pending

RedShades cryptographic evidence normalizerCustom implementation planned

LicenseRef-REDC2-Internal

cryptographic inventory

Packaging pending · Validation pending

RedShades OT/space safety modelCustom implementation planned

LicenseRef-REDC2-Internal

safety modeling · policy gating

Packaging pending · Validation pending

RedShades privacy/data-flow modelCustom implementation planned

LicenseRef-REDC2-Internal

topology modeling · configuration review

Packaging pending · Validation pending

RedShades defensive change plannerCustom implementation planned

LicenseRef-REDC2-Internal

evidence correlation · reporting · policy gating

Packaging pending · Validation pending

RedShades protocol observation normalizerCustom implementation planned

LicenseRef-REDC2-Internal

passive capture parsing · evidence correlation

Packaging pending · Validation pending

AndroguardOpen-source integration

Apache-2.0

artifact intake · static analysis

Packaging pending · Validation pending

License source ↗
JADXOpen-source integration

Apache-2.0

static analysis

Packaging pending · Validation pending

License source ↗
ApktoolOpen-source integration

Apache-2.0

binary decomposition · static analysis

Packaging pending · Validation pending

License source ↗
Android bundletoolOpen-source integration

Apache-2.0

artifact intake · binary decomposition

Packaging pending · Validation pending

License source ↗
Mobile Security FrameworkLicense review

GPL-3.0-only

static analysis · configuration review

Packaging pending · Validation pending

License source ↗
ipswOpen-source integration

MIT

artifact intake · binary decomposition · static analysis

Packaging pending · Validation pending

License source ↗
LLVM binary utilitiesOpen-source integration

Apache-2.0 WITH LLVM-exception

static analysis

Packaging pending · Validation pending

License source ↗
Apple codesign/security toolchainExternal toolchain

NOASSERTION

artifact intake · configuration review

Packaging pending · Validation pending

License source ↗
Solidity compilerLicense review

GPL-3.0-only

static analysis · binary decomposition

Packaging pending · Validation pending

License source ↗
SlitherLicense review

AGPL-3.0-only

static analysis · evidence correlation

Packaging pending · Validation pending

License source ↗
FoundryOpen-source integration

MIT OR Apache-2.0

emulation simulation · static analysis

Packaging pending · Validation pending

License source ↗
EchidnaLicense review

AGPL-3.0-only

emulation simulation · static analysis

Packaging pending · Validation pending

License source ↗
Wireshark/TSharkLicense review

GPL-2.0-or-later

passive capture parsing · evidence correlation

Packaging pending · Validation pending

License source ↗
ZeekOpen-source integration

BSD-3-Clause

passive capture parsing · evidence correlation

Packaging pending · Validation pending

License source ↗
BlueZ btmonLicense review

GPL-2.0-or-later

passive capture parsing

Packaging pending · Validation pending

License source ↗
libnfc utilitiesLicense review

LGPL-3.0-or-later

passive capture parsing

Packaging pending · Validation pending

License source ↗
SuricataLicense review

GPL-2.0-only

passive capture parsing · evidence correlation

Packaging pending · Validation pending

License source ↗
garakOpen-source integration

Apache-2.0

static analysis · emulation simulation

Packaging pending · Validation pending

License source ↗
Inspect AIOpen-source integration

MIT

emulation simulation · reporting

Packaging pending · Validation pending

License source ↗
GNU RadioLicense review

GPL-3.0-or-later

passive capture parsing · emulation simulation

Packaging pending · Validation pending

License source ↗
gr-satellitesLicense review

GPL-3.0-or-later

passive capture parsing

Packaging pending · Validation pending

License source ↗
OrekitOpen-source integration

Apache-2.0

emulation simulation · evidence correlation

Packaging pending · Validation pending

License source ↗
Qiskit SDKOpen-source integration

Apache-2.0

static analysis · emulation simulation

Packaging pending · Validation pending

License source ↗
CirqOpen-source integration

Apache-2.0

static analysis · emulation simulation

Packaging pending · Validation pending

License source ↗
BinwalkOpen-source integration

MIT

binary decomposition · static analysis

Packaging pending · Validation pending

License source ↗
GhidraOpen-source integration

Apache-2.0

static analysis

Packaging pending · Validation pending

License source ↗
QEMULicense review

GPL-2.0-only

emulation simulation

Packaging pending · Validation pending

License source ↗
SyftOpen-source integration

Apache-2.0

supply chain analysis · artifact intake

Packaging pending · Validation pending

License source ↗
OSV-ScannerOpen-source integration

Apache-2.0

supply chain analysis

Packaging pending · Validation pending

License source ↗
GrypeOpen-source integration

Apache-2.0

supply chain analysis

Packaging pending · Validation pending

License source ↗
TrivyOpen-source integration

Apache-2.0

supply chain analysis · configuration review

Packaging pending · Validation pending

License source ↗
OpenSCAPLicense review

LGPL-2.1-or-later

configuration review · reporting

Packaging pending · Validation pending

License source ↗
CosignOpen-source integration

Apache-2.0

provenance custody · supply chain analysis

Packaging pending · Validation pending

License source ↗
The Sleuth KitLicense review

CPL-1.0 AND IPL-1.0

forensic analysis · artifact intake

Packaging pending · Validation pending

License source ↗
Volatility 3License review

LicenseRef-Volatility-Software-License-1.0

forensic analysis

Packaging pending · Validation pending

License source ↗
PlasoOpen-source integration

Apache-2.0

forensic analysis · evidence correlation

Packaging pending · Validation pending

License source ↗
YARAOpen-source integration

BSD-3-Clause

static analysis · forensic analysis

Packaging pending · Validation pending

License source ↗
VelociraptorLicense review

AGPL-3.0-only

artifact intake · forensic analysis

Packaging pending · Validation pending

License source ↗
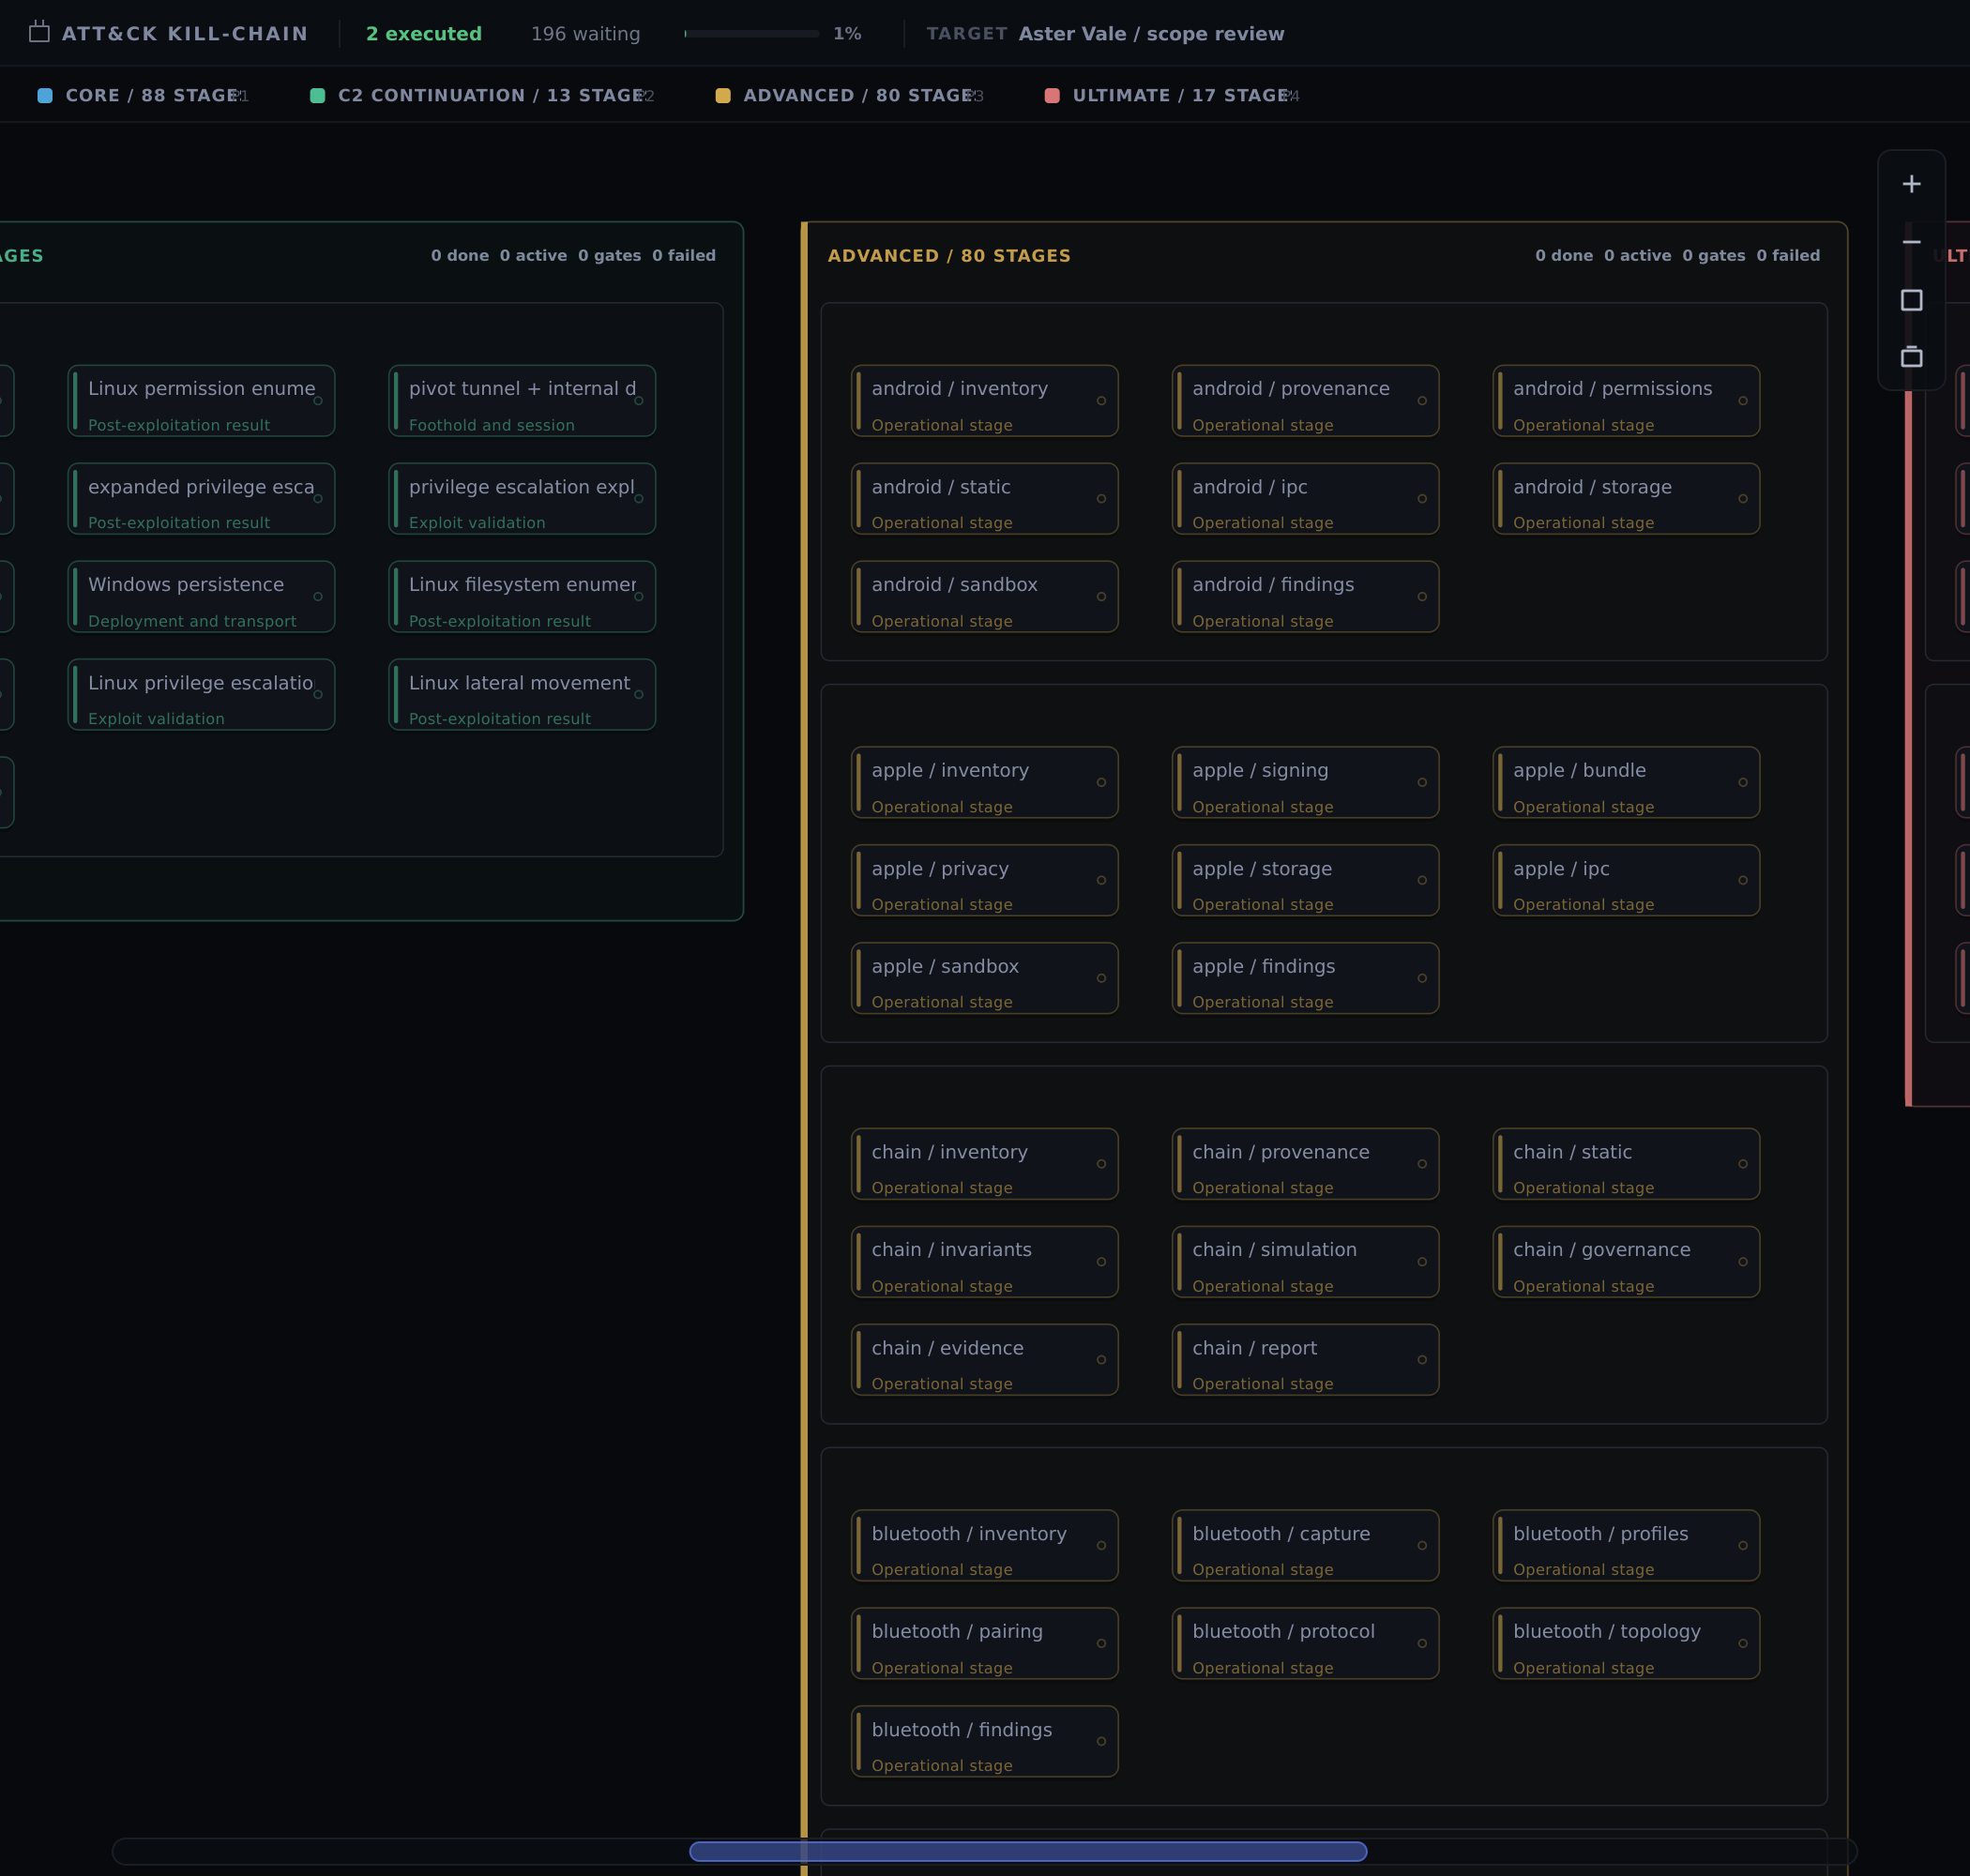
ADVANCED BUNDLE · 80 ADDITIONAL STAGES

Specialist scope, shared infrastructure

Under testing

The 78 domain stages and two shared Advanced helpers apply the Core’s evidence and routing model to specialist assessments. Domain-specific observations determine which analyses are eligible, and their findings return to the shared investigation record.

Android / mobile

8 stages
Under testing

Package metadata, permissions and storage observations give application review a concrete starting point. Device and transport evidence determine the applicable analysis.

Assessment scope
Mobile configuration, application metadata and transport review
Shared tool architecture
10 referenced entries · Androguard, Apktool, Android bundletool, Cosign, JADX, Mobile Security Framework. Native evidence and reporting components complete the cluster.

Apple platforms

8 stages
Under testing

Signing and entitlements connect application behavior to platform permissions. iOS, iPhone and macOS evidence also supports privacy and configuration review.

Assessment scope
Signing, entitlements, privacy settings and platform configuration
Shared tool architecture
8 referenced entries · ipsw, LLVM binary utilities, Apple codesign/security toolchain. Native evidence and reporting components complete the cluster.

Blockchain

8 stages
Under testing

Contract and transaction records support access-control, dependency and governance review. Provenance keeps each conclusion connected to the relevant artifact.

Assessment scope
Contract metadata, access controls and transaction provenance
Shared tool architecture
8 referenced entries · Cosign, Echidna, Foundry, Slither, Solidity compiler. Native evidence and reporting components complete the cluster.

Proximity / BLE / NFC

7 stages
Under testing

Captured advertisements, pairing observations and NFC records preserve the distinctions between protocols and device classes.

Assessment scope
Advertisement, pairing and NFC record analysis
Shared tool architecture
8 referenced entries · BlueZ btmon, libnfc utilities, Wireshark/TShark, Zeek. Native evidence and reporting components complete the cluster.

Wi-Fi / RF

8 stages
Under testing

Recorded traffic and wireless configuration support network, radio and authentication review. Spectrum records add context where the evidence provides it.

Assessment scope
Wireless posture, spectrum records and authentication configuration
Shared tool architecture
9 referenced entries · GNU Radio, Suricata, Wireshark/TShark, Zeek. Native evidence and reporting components complete the cluster.

LLM / AI systems

8 stages
Under testing

Evaluation artifacts connect model behavior to application permissions and data handling. Model, data and application boundaries receive separate attention.

Assessment scope
Evaluation artifacts, data handling and permission boundaries
Shared tool architecture
10 referenced entries · garak, Inspect AI, OSV-Scanner, Syft, Trivy. Native evidence and reporting components complete the cluster.

Satellite / space

7 stages
Under testing

Ground-system configuration and telemetry artifacts frame the assessment. Ground, link and telemetry evidence retain their different trust boundaries.

Assessment scope
Telemetry formats, asset configuration and trust boundaries
Shared tool architecture
10 referenced entries · GNU Radio, gr-satellites, Orekit, Wireshark/TShark, Zeek. Native evidence and reporting components complete the cluster.

Quantum readiness

6 stages
Under testing

A cryptographic asset inventory supports algorithm and dependency review, exposing the evidence needed to assess migration readiness.

Assessment scope
Cryptographic discovery and migration readiness analysis
Shared tool architecture
6 referenced entries · Cirq, Qiskit SDK. Native evidence and reporting components complete the cluster.

Hardware / firmware

9 stages
Under testing

Firmware images and component inventories support metadata, provenance and secure-boot review. Image, component and boot-policy evidence remain distinguishable.

Assessment scope
Firmware metadata, component provenance and secure-boot posture
Shared tool architecture
11 referenced entries · Binwalk, Cosign, Ghidra, ipsw, LLVM binary utilities, QEMU, Syft, Trivy. Native evidence and reporting components complete the cluster.

ICS / SCADA

9 stages
Under testing

Industrial asset and configuration records support protocol and segmentation review. Asset, protocol and zone context define the relevant branches.

Assessment scope
Configuration review, protocol records and segmentation posture
Shared tool architecture
11 referenced entries · OpenSCAP, QEMU, Suricata, Wireshark/TShark, Zeek. Native evidence and reporting components complete the cluster.

Shared Advanced orchestration

2 cross-domain helpers · Under testing

Evidence normalization gives domain observations a common representation. Correlation and convergence connect those normalized observations into a consistent assessment record.

Domain observations → shared normalization → correlation and convergence → assessment record

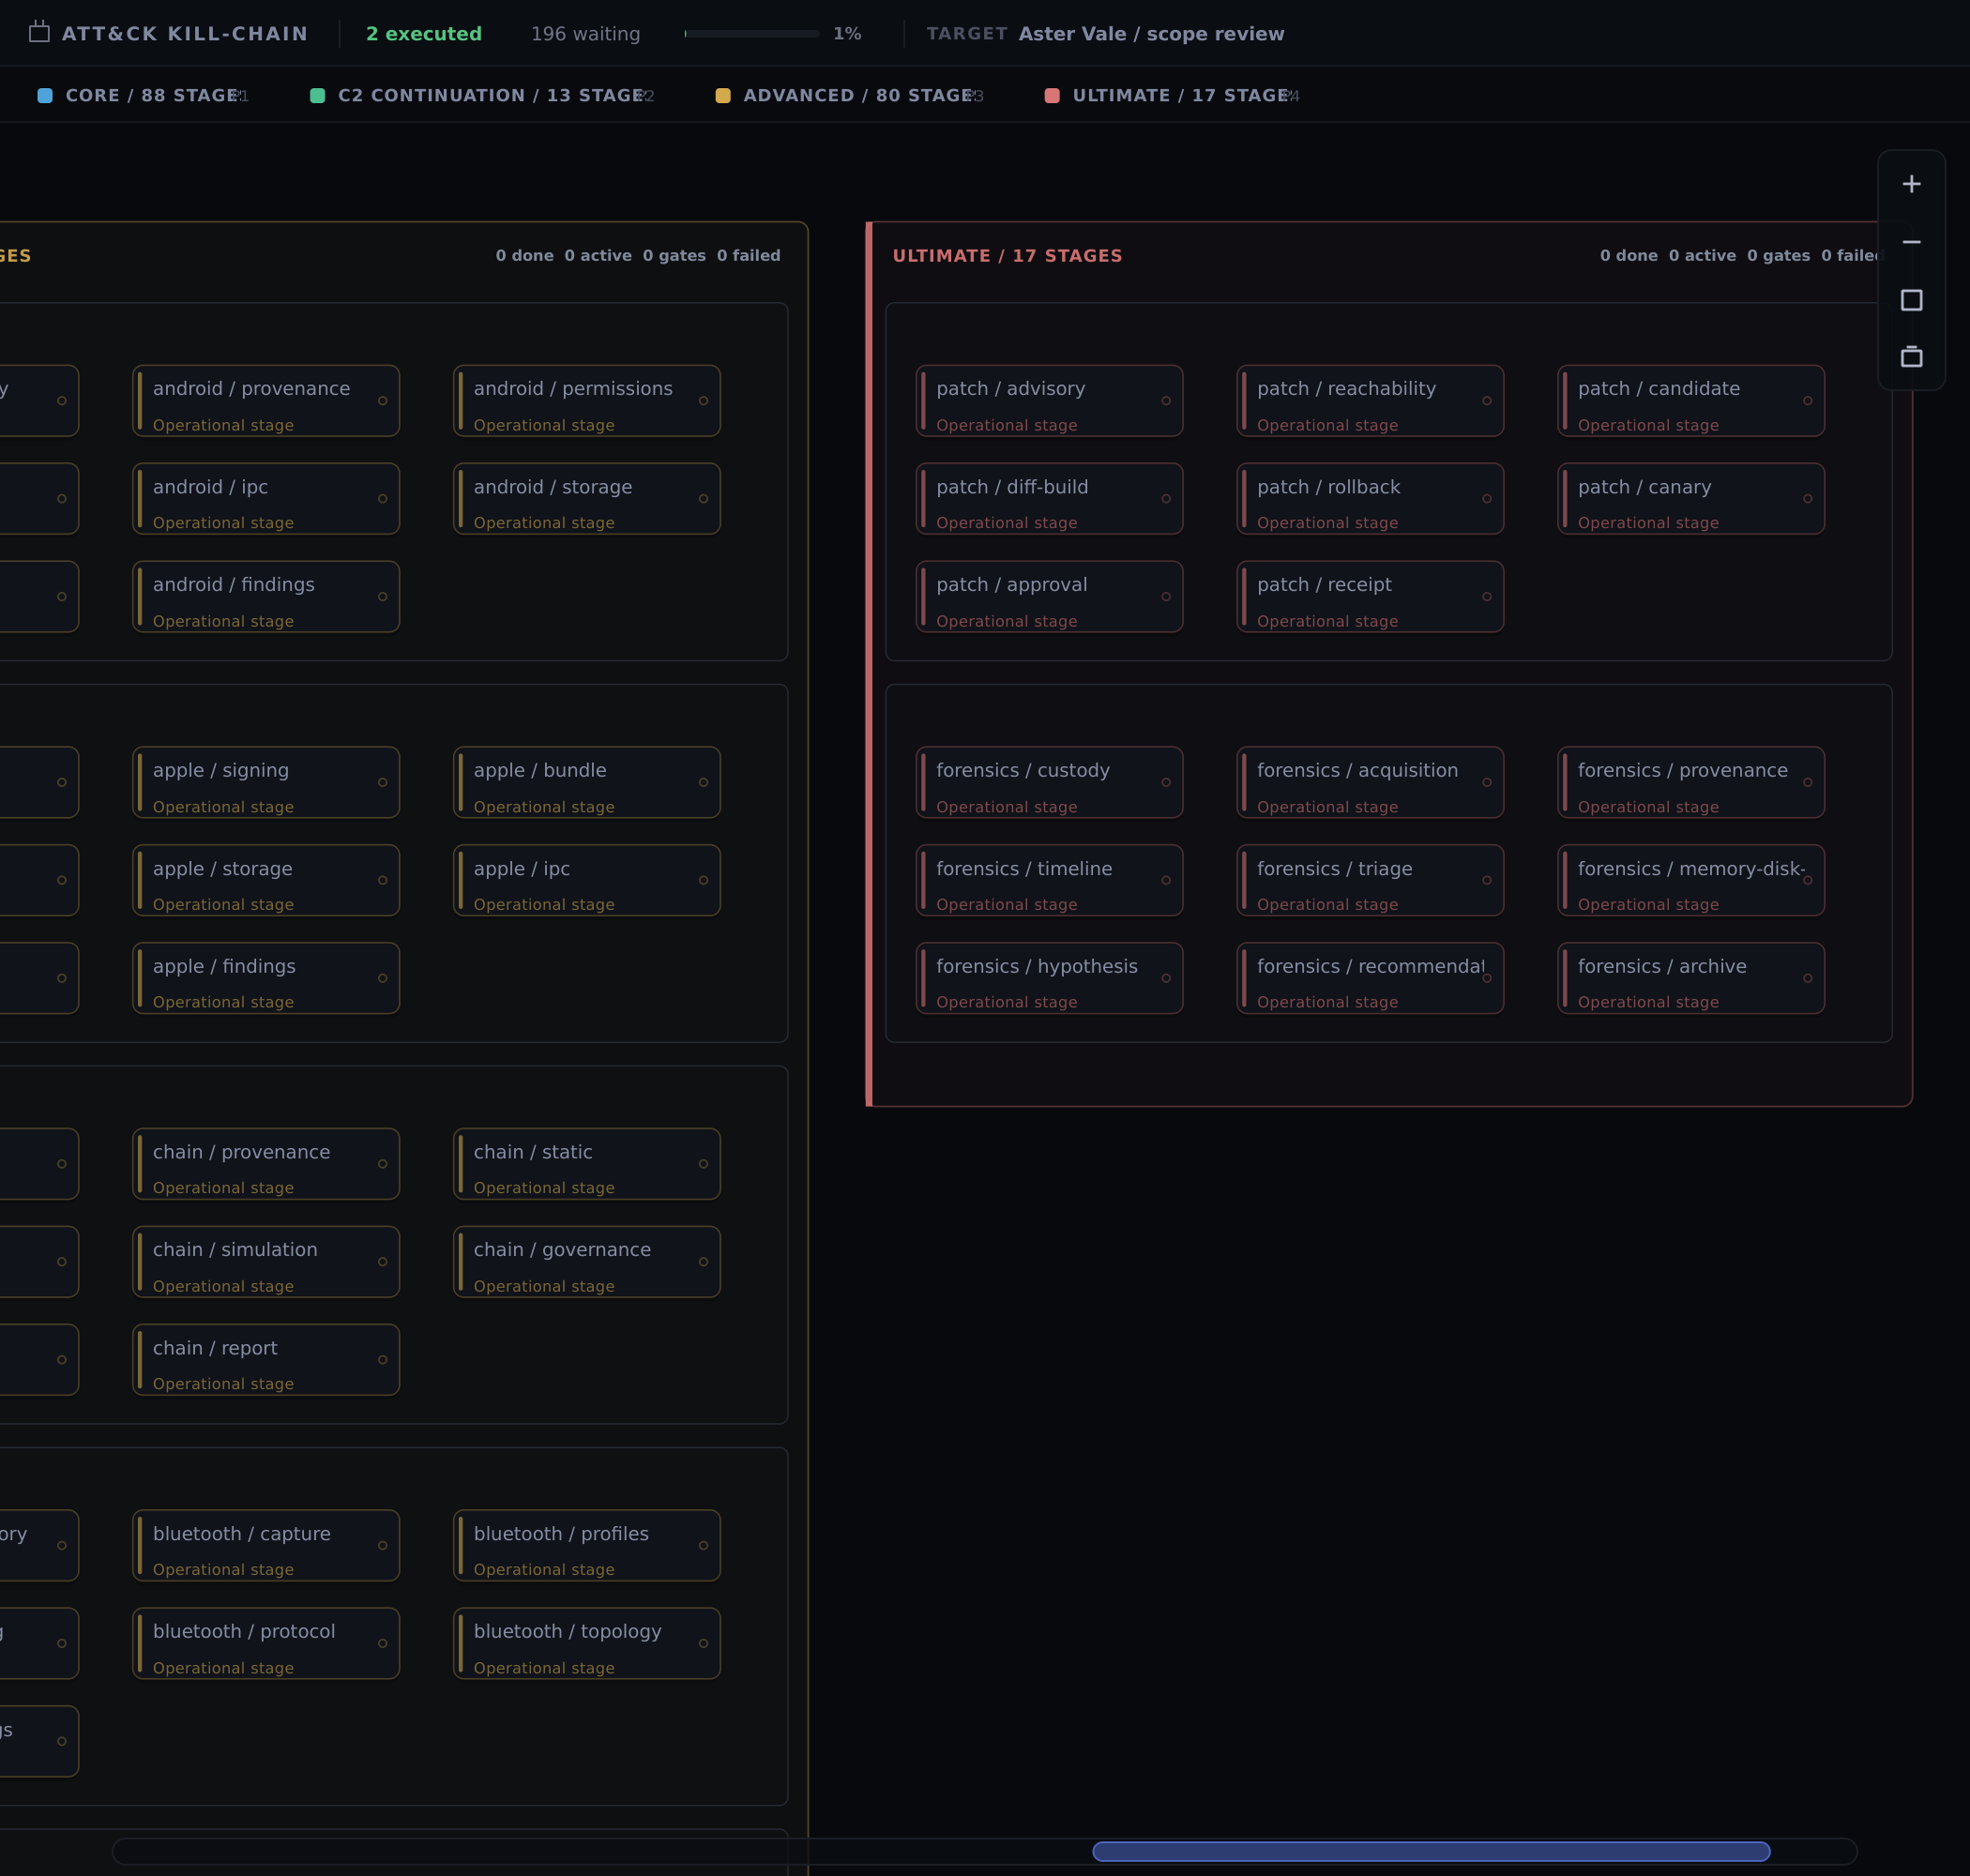
ULTIMATE BUNDLE · 17 ADDITIONAL STAGES

From assessment to remediation and custody

Under development

PurpleShades · Defensive patching

8 stages · Under development

Asset and finding intake opens parallel exposure, dependency and remediation analysis. A change plan brings the branches together with rollback criteria, canary observations and approval requirements.

Advisories → assessment branches → change proposal → rollback / canary criteria → approval → review packet

The workflow assembles a reviewed proposal and defines the evidence required to validate a future change.

Digital forensics

9 stages · Under development

Case intake establishes evidence identity and custody. Artifact, timeline and correlation branches preserve source attribution and converge into a reviewable case record.

Case intake → evidence preservation → analysis branches → correlation → review → case report

Integrity checks precede analysis. Incomplete or conflicting observations remain visible in the final evidence account.

PER-SEAT ANNUAL PRICING

The annual seat, and what it includes

Each annual seat brings the native workspace, integrated tool workflows and controlled model access together. Select the assessment scope and deployment entitlement that fit the work.

Core

Starting at$7,000/ year per seat

88 Core stages + 13 C2 continuation stages

Validated Core

100 fine-tuned specialist adapters for bounded stateless calls and code-review roles. Gated 30B3A Flash access includes 50,000 credits per week throughout the active annual subscription.

Advanced

Starting at$14,000/ year per seat

Core stage scope + 80 Advanced stages

Under testing

Fine-tuned 30B3A Flash model weights included under NDA for persistent higher-complexity sessions. The weights entitlement gives qualified deployments direct access to the model asset.

Ultimate

Starting at$20,000/ year per seat

Core and Advanced stage scope + 17 defensive and forensic stages

Under development

50,000 credits per week throughout the active annual subscription. The proprietary multi-encoder suite adds task-specific embedding and representation variants for defensive and forensic work; it is not an LLM. An optional additional $5,000 weights entitlement under NDA supports intensive parallel and large-network deployments.

Fine-tuned model and adapter access is controlled by subscription gates. Weights access is a separate, selective entitlement under NDA. Active subscriptions receive applicable weights and stage updates at least every six months.

198 stages across the full catalog: 88 Validated Core, 13 C2 continuation, 80 Advanced and 17 Ultimate. Advanced comprises 78 domain stages and two shared helpers.

The native workspace

Follow the evidence into detail

Explore the stage repertoire, source records and controls behind the investigation.

Explore 12 additional operator views
The complete repertoire
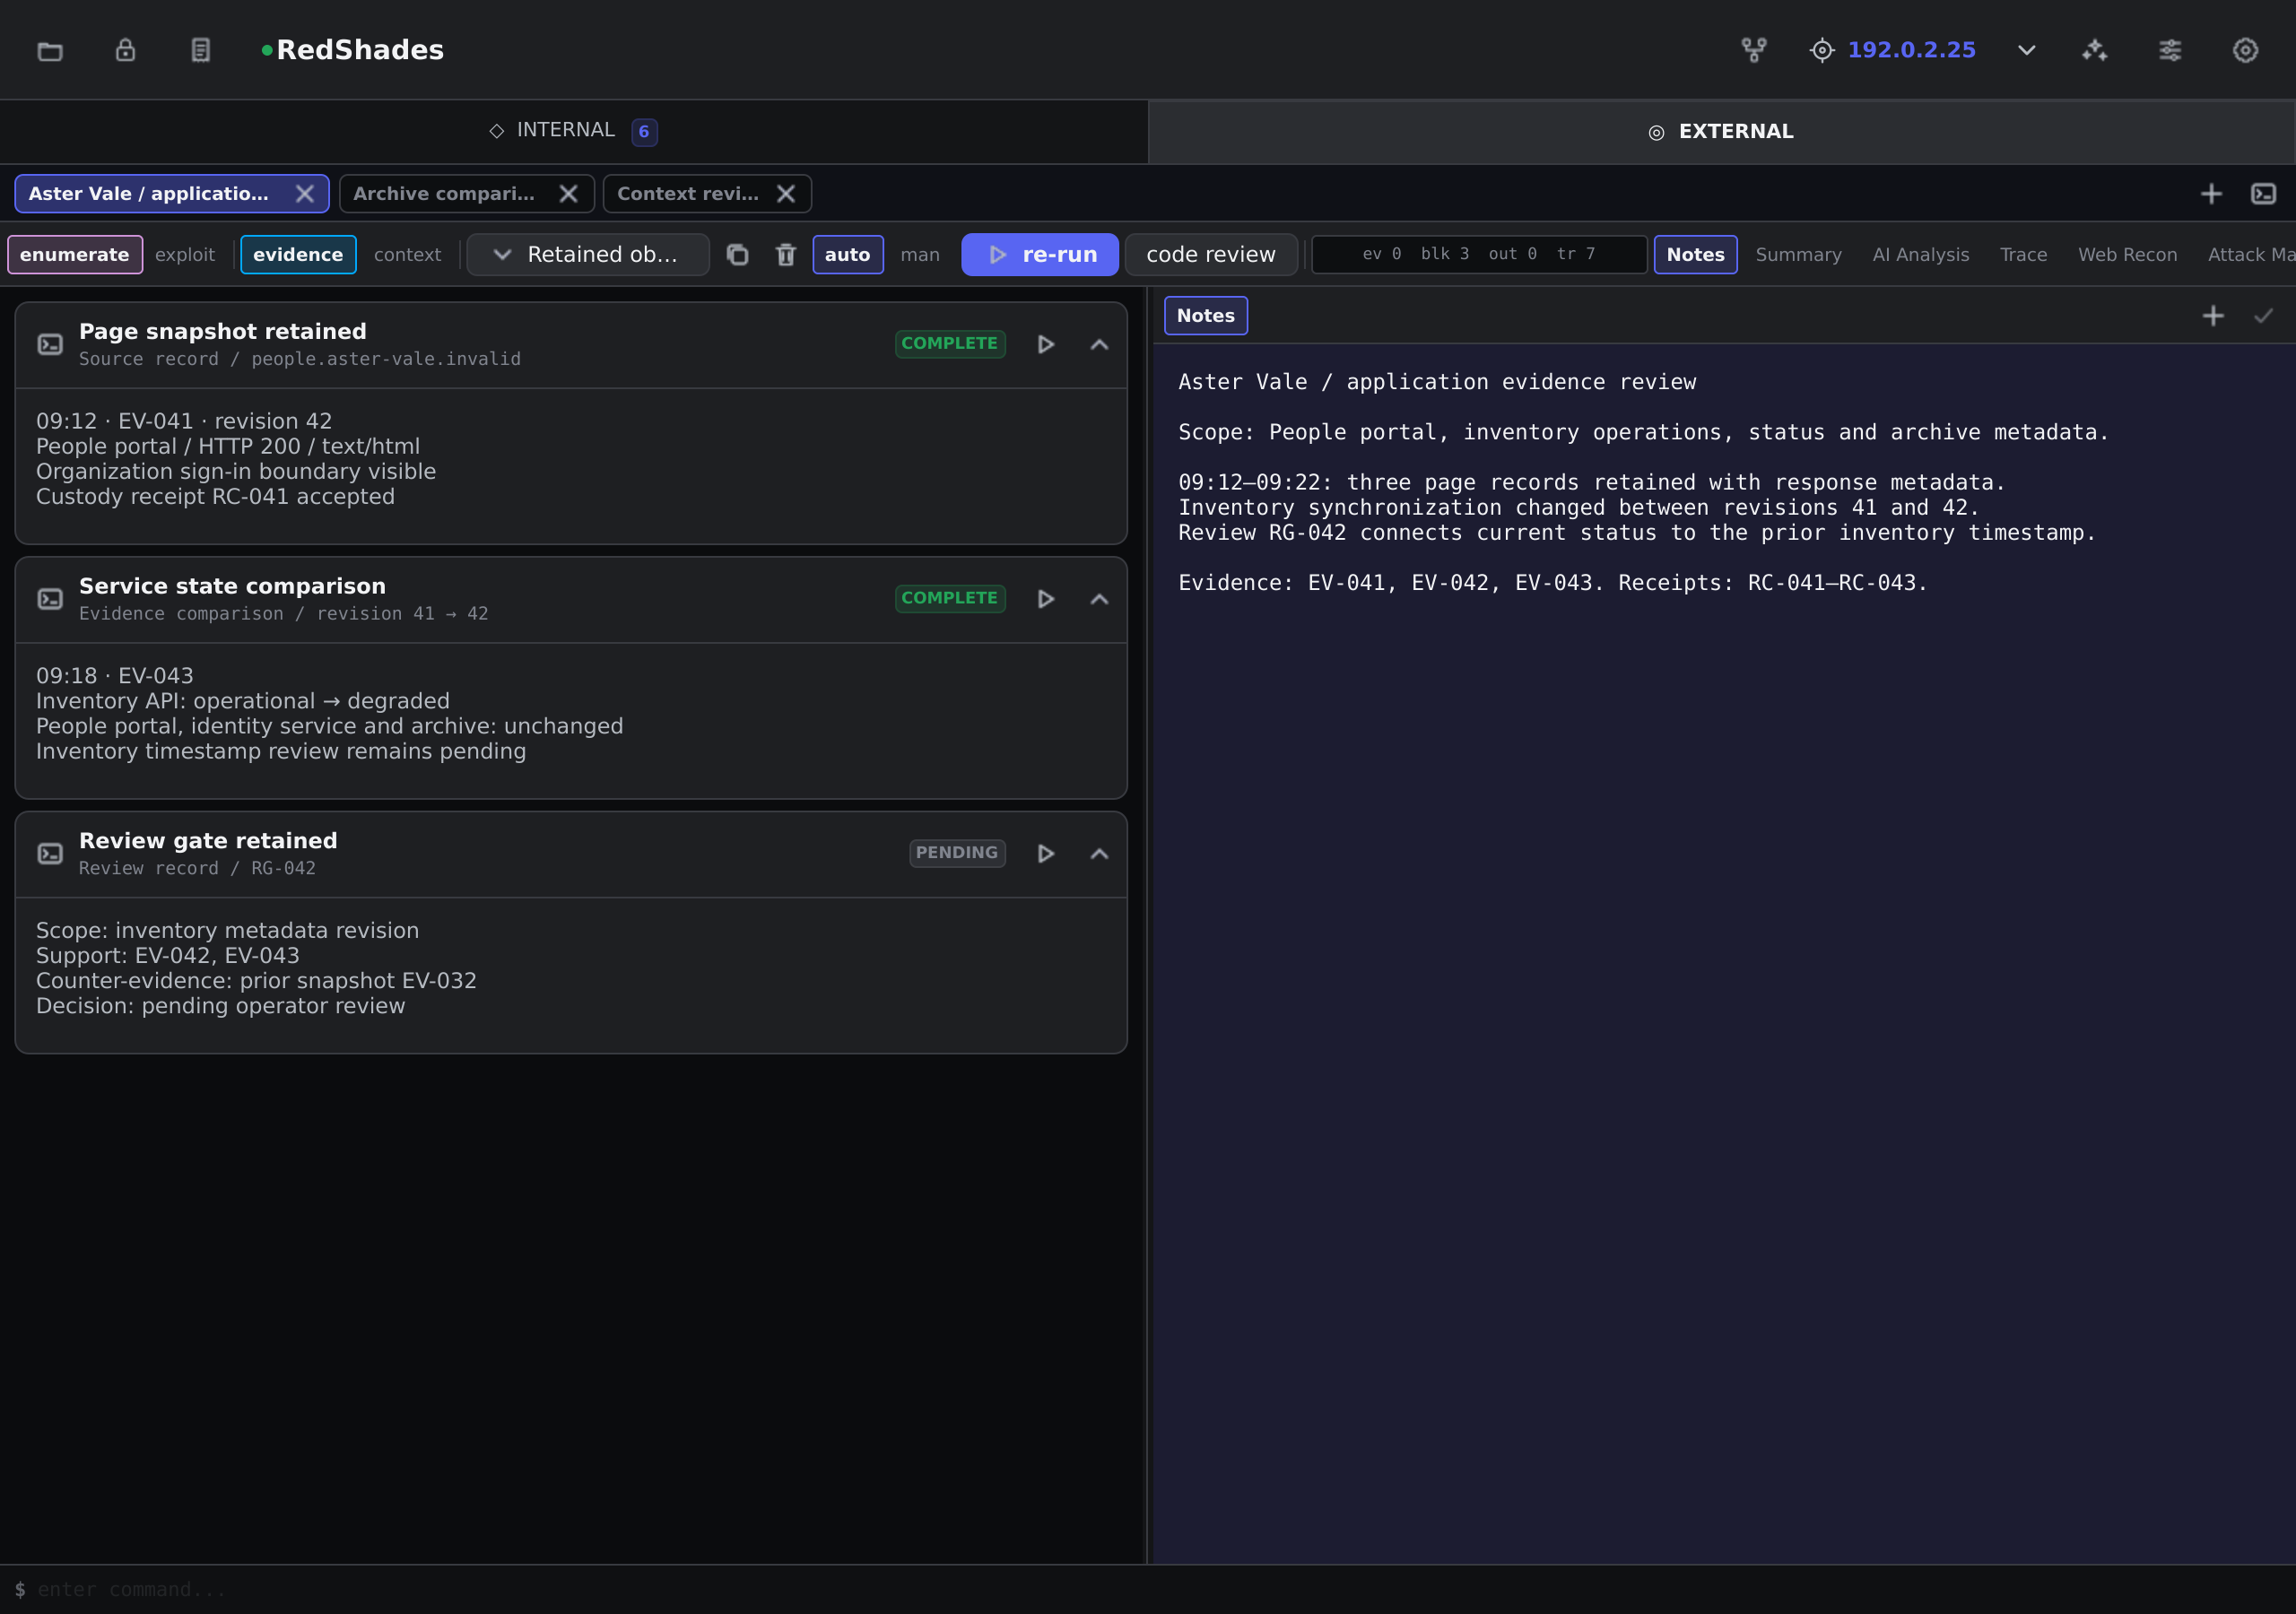
The complete repertoire198 stage declarations grouped by bundle and family. Open the full map to inspect every stage.
Specialist domains
Specialist domainsInspect grouped application and platform responsibilities.
Defensive and forensic work
Defensive and forensic workReview the responsibilities that connect remediation and evidence custody.
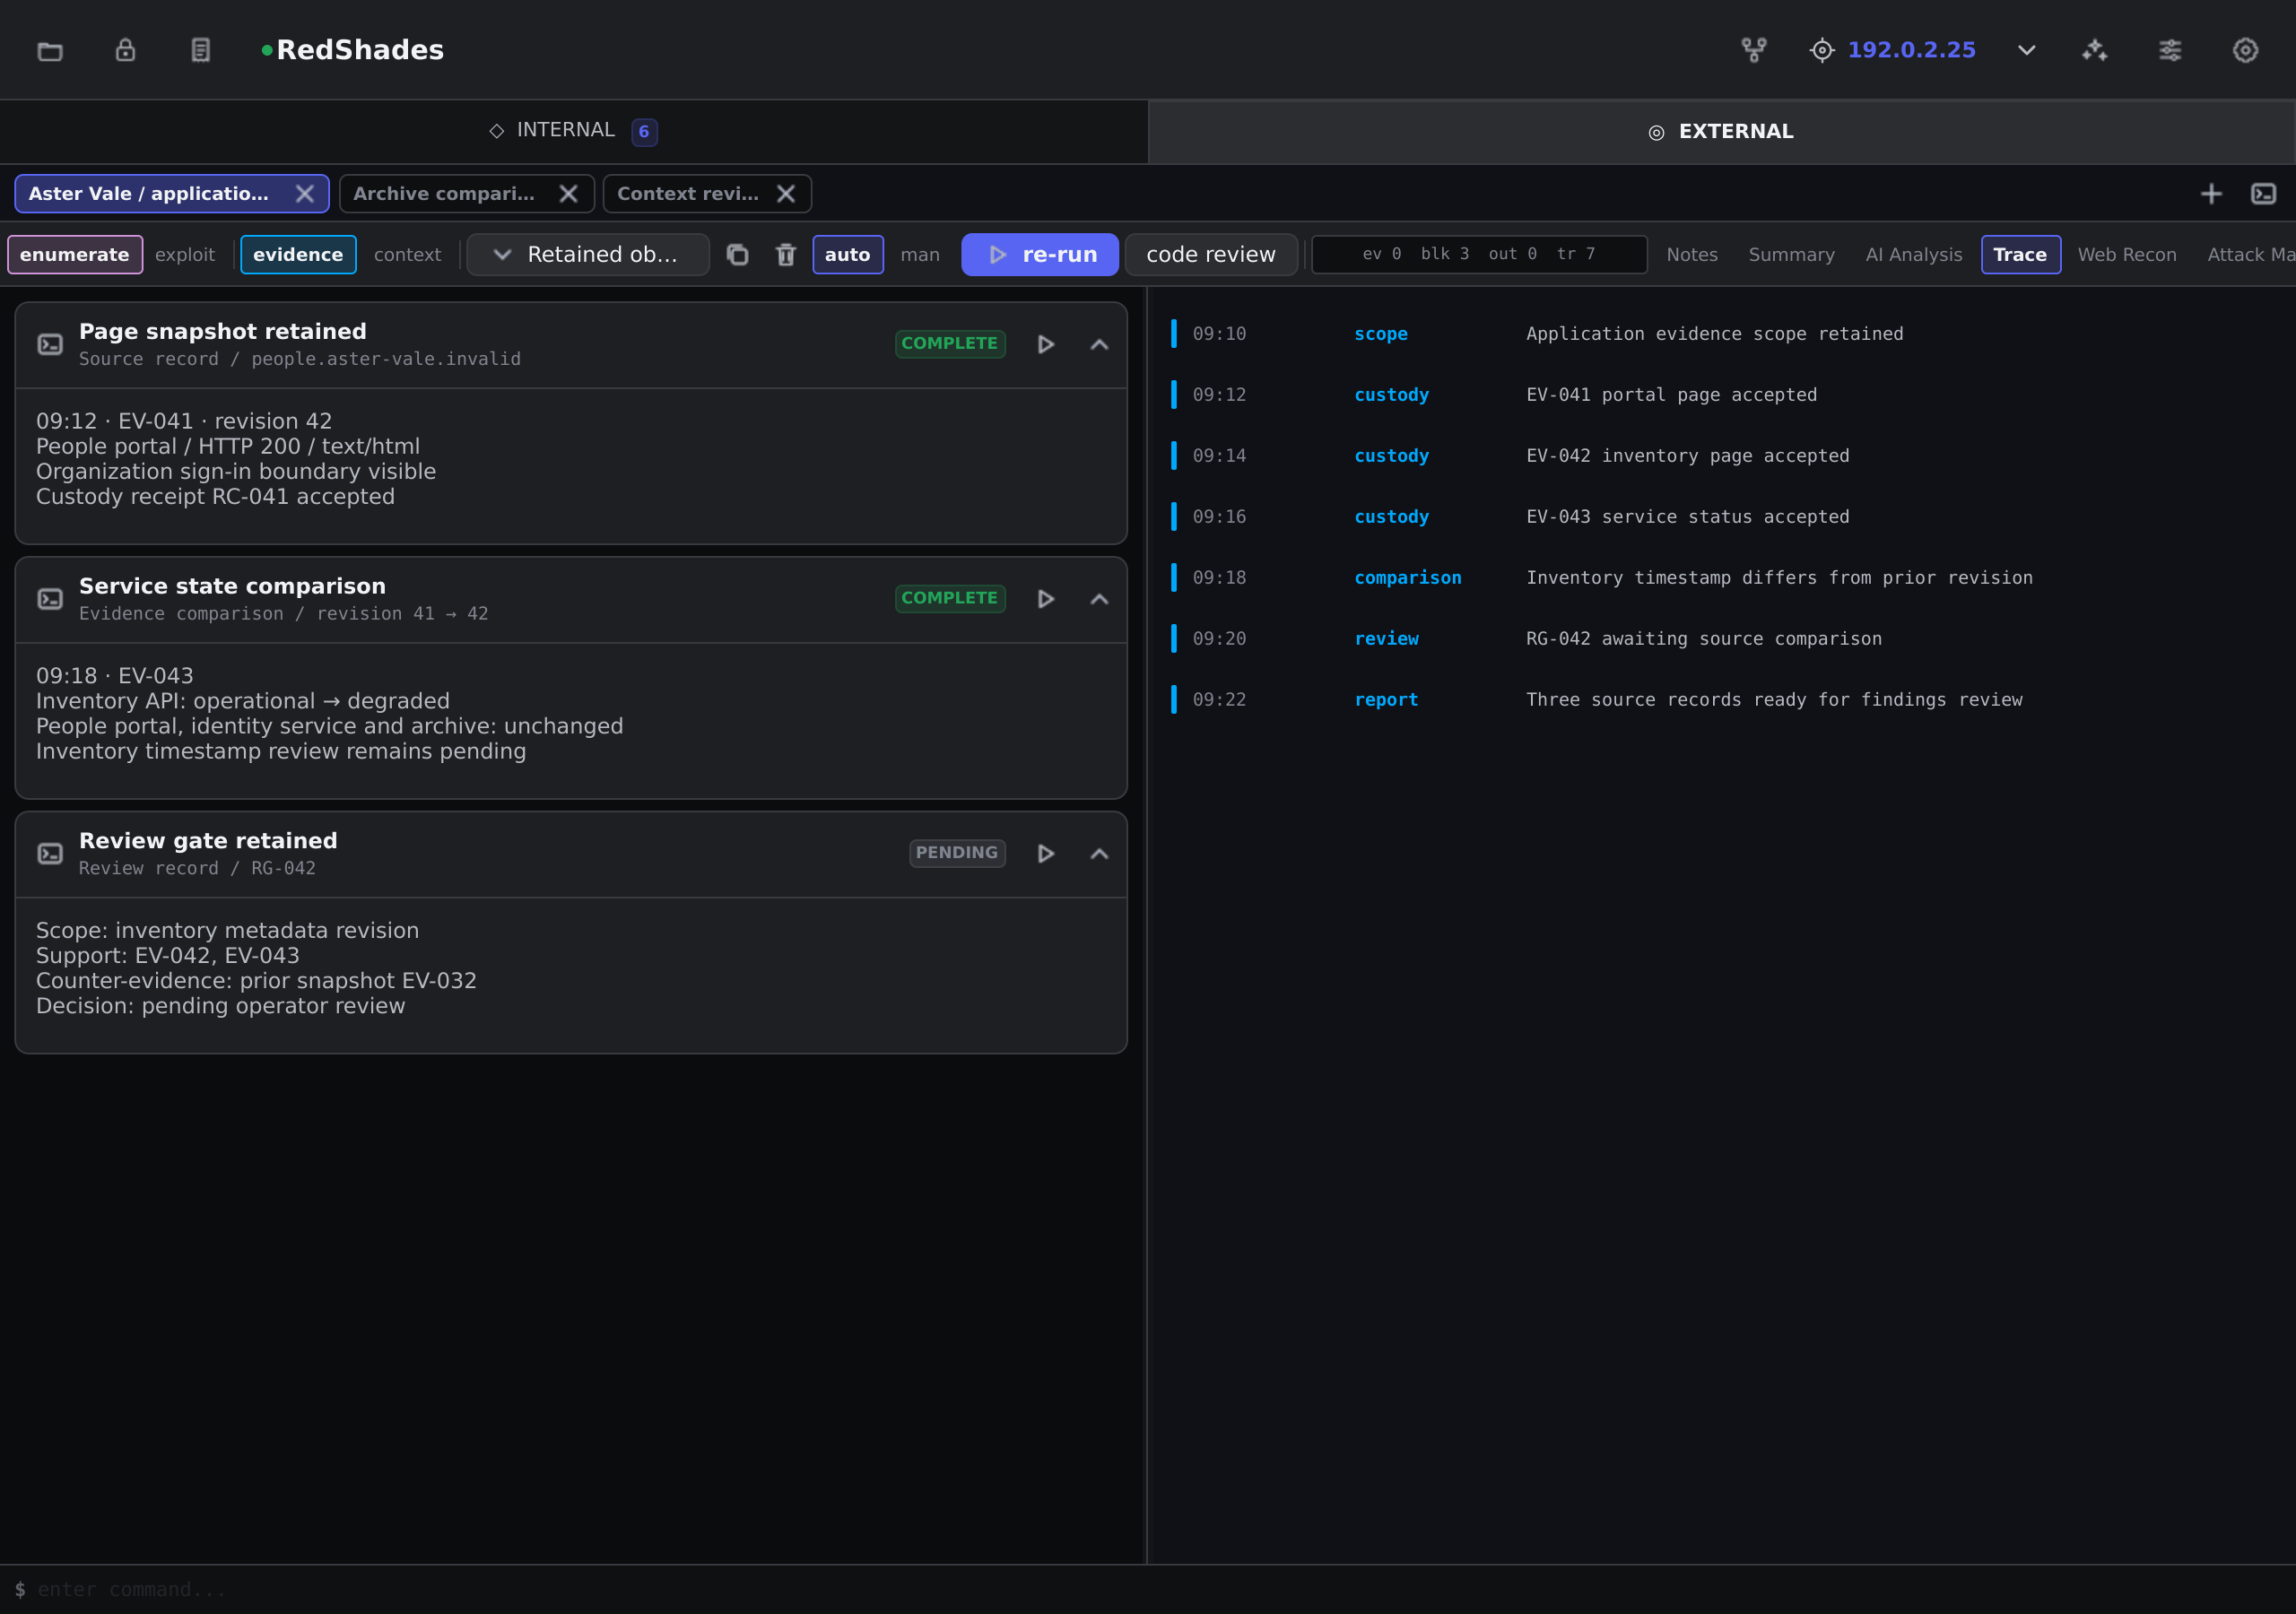
Execution history
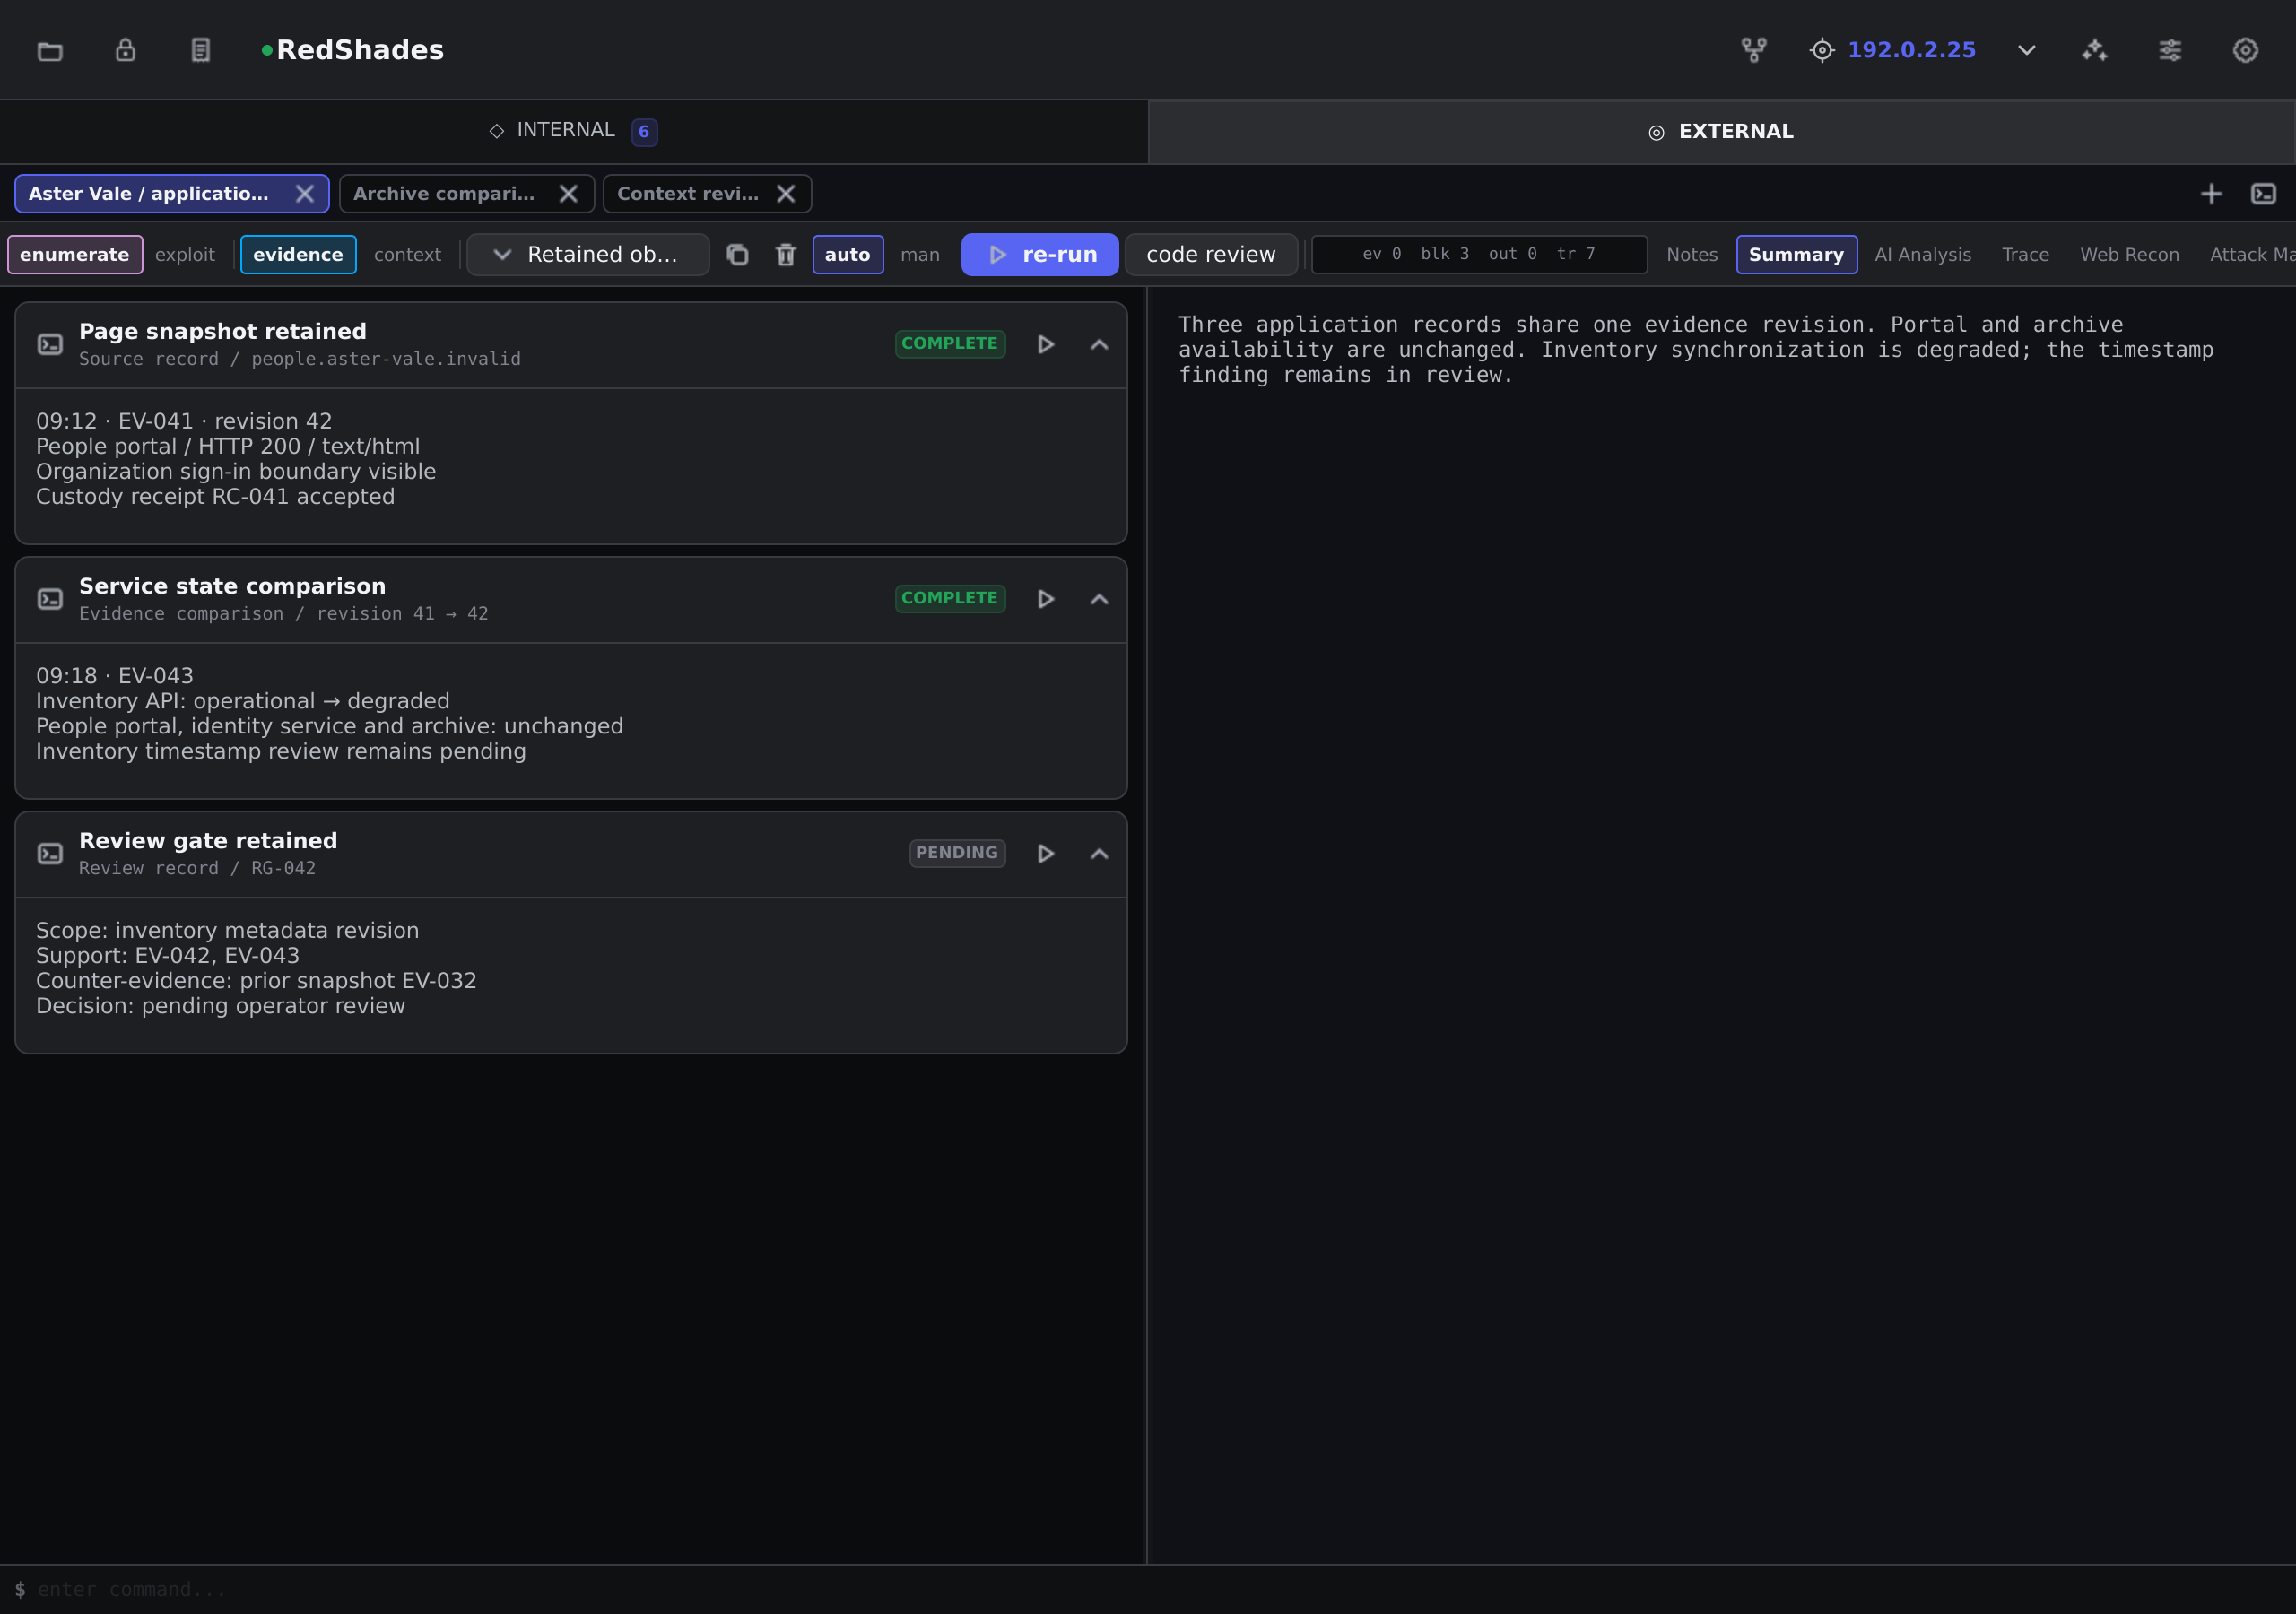
Execution historyFollow the timestamps connecting source retention, comparison and review.
Engagement summary
Engagement summaryKeep accepted observations beside the records that support them.
Interpretation and counter-evidence
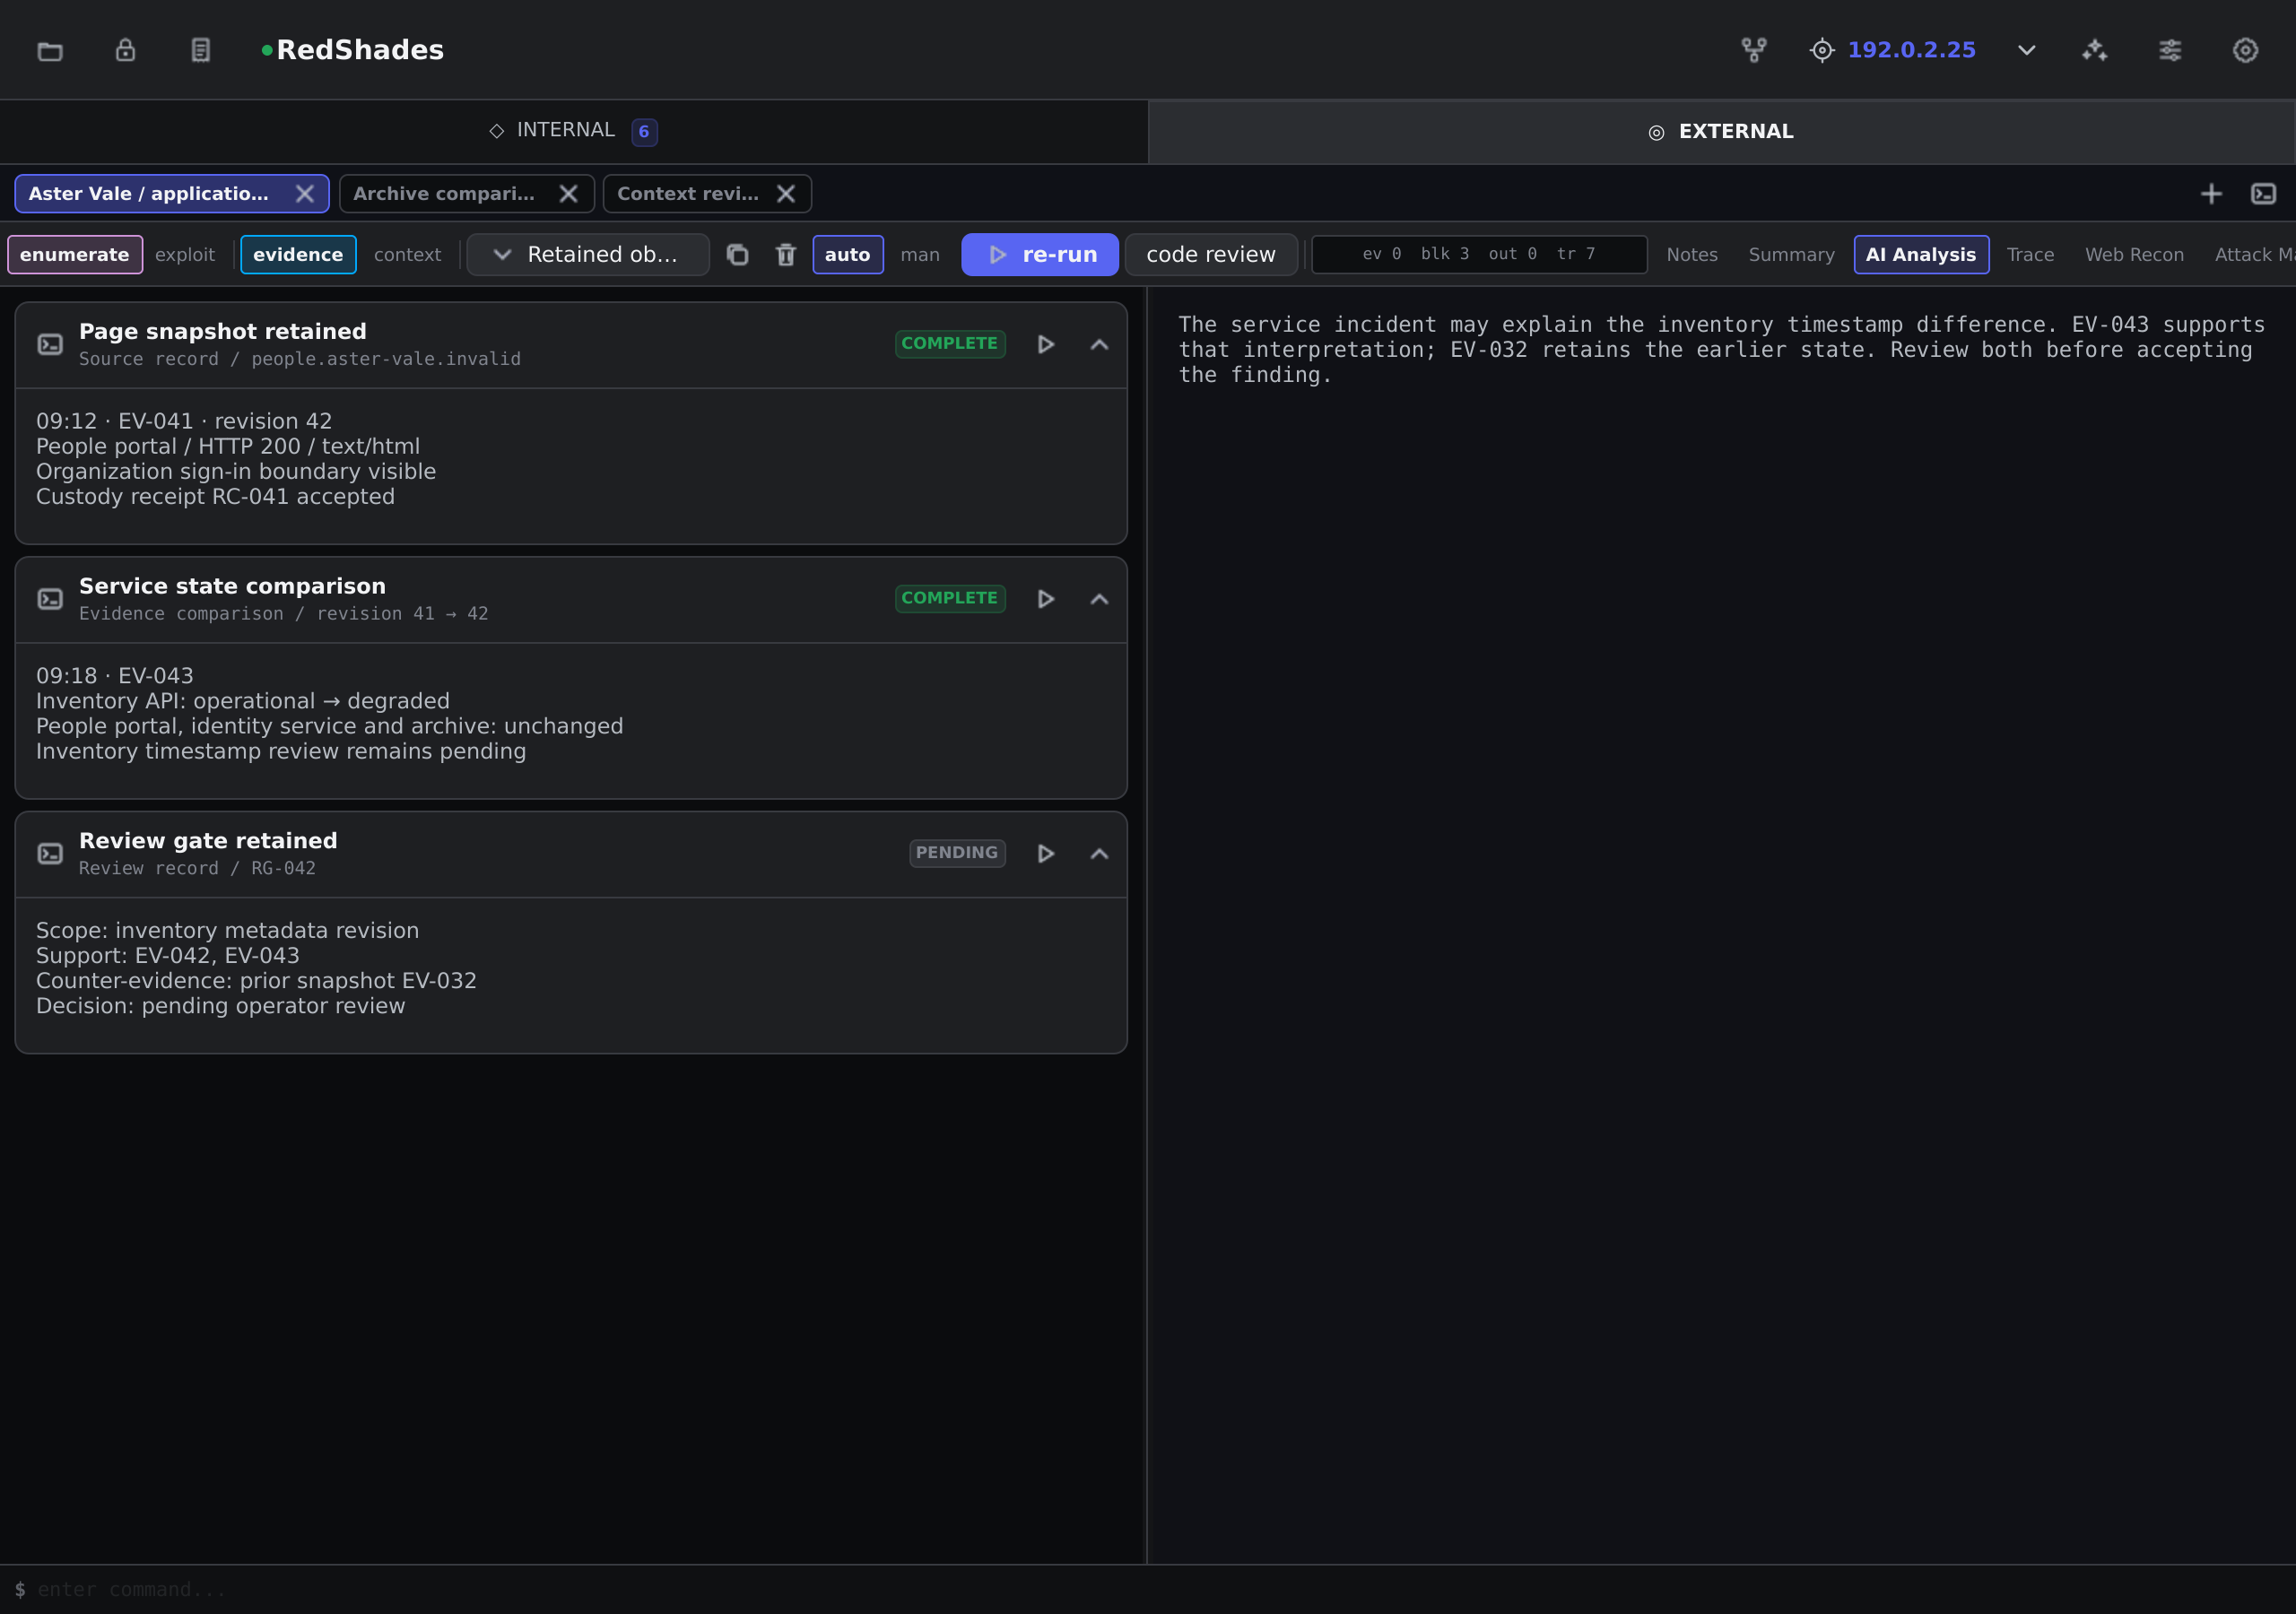
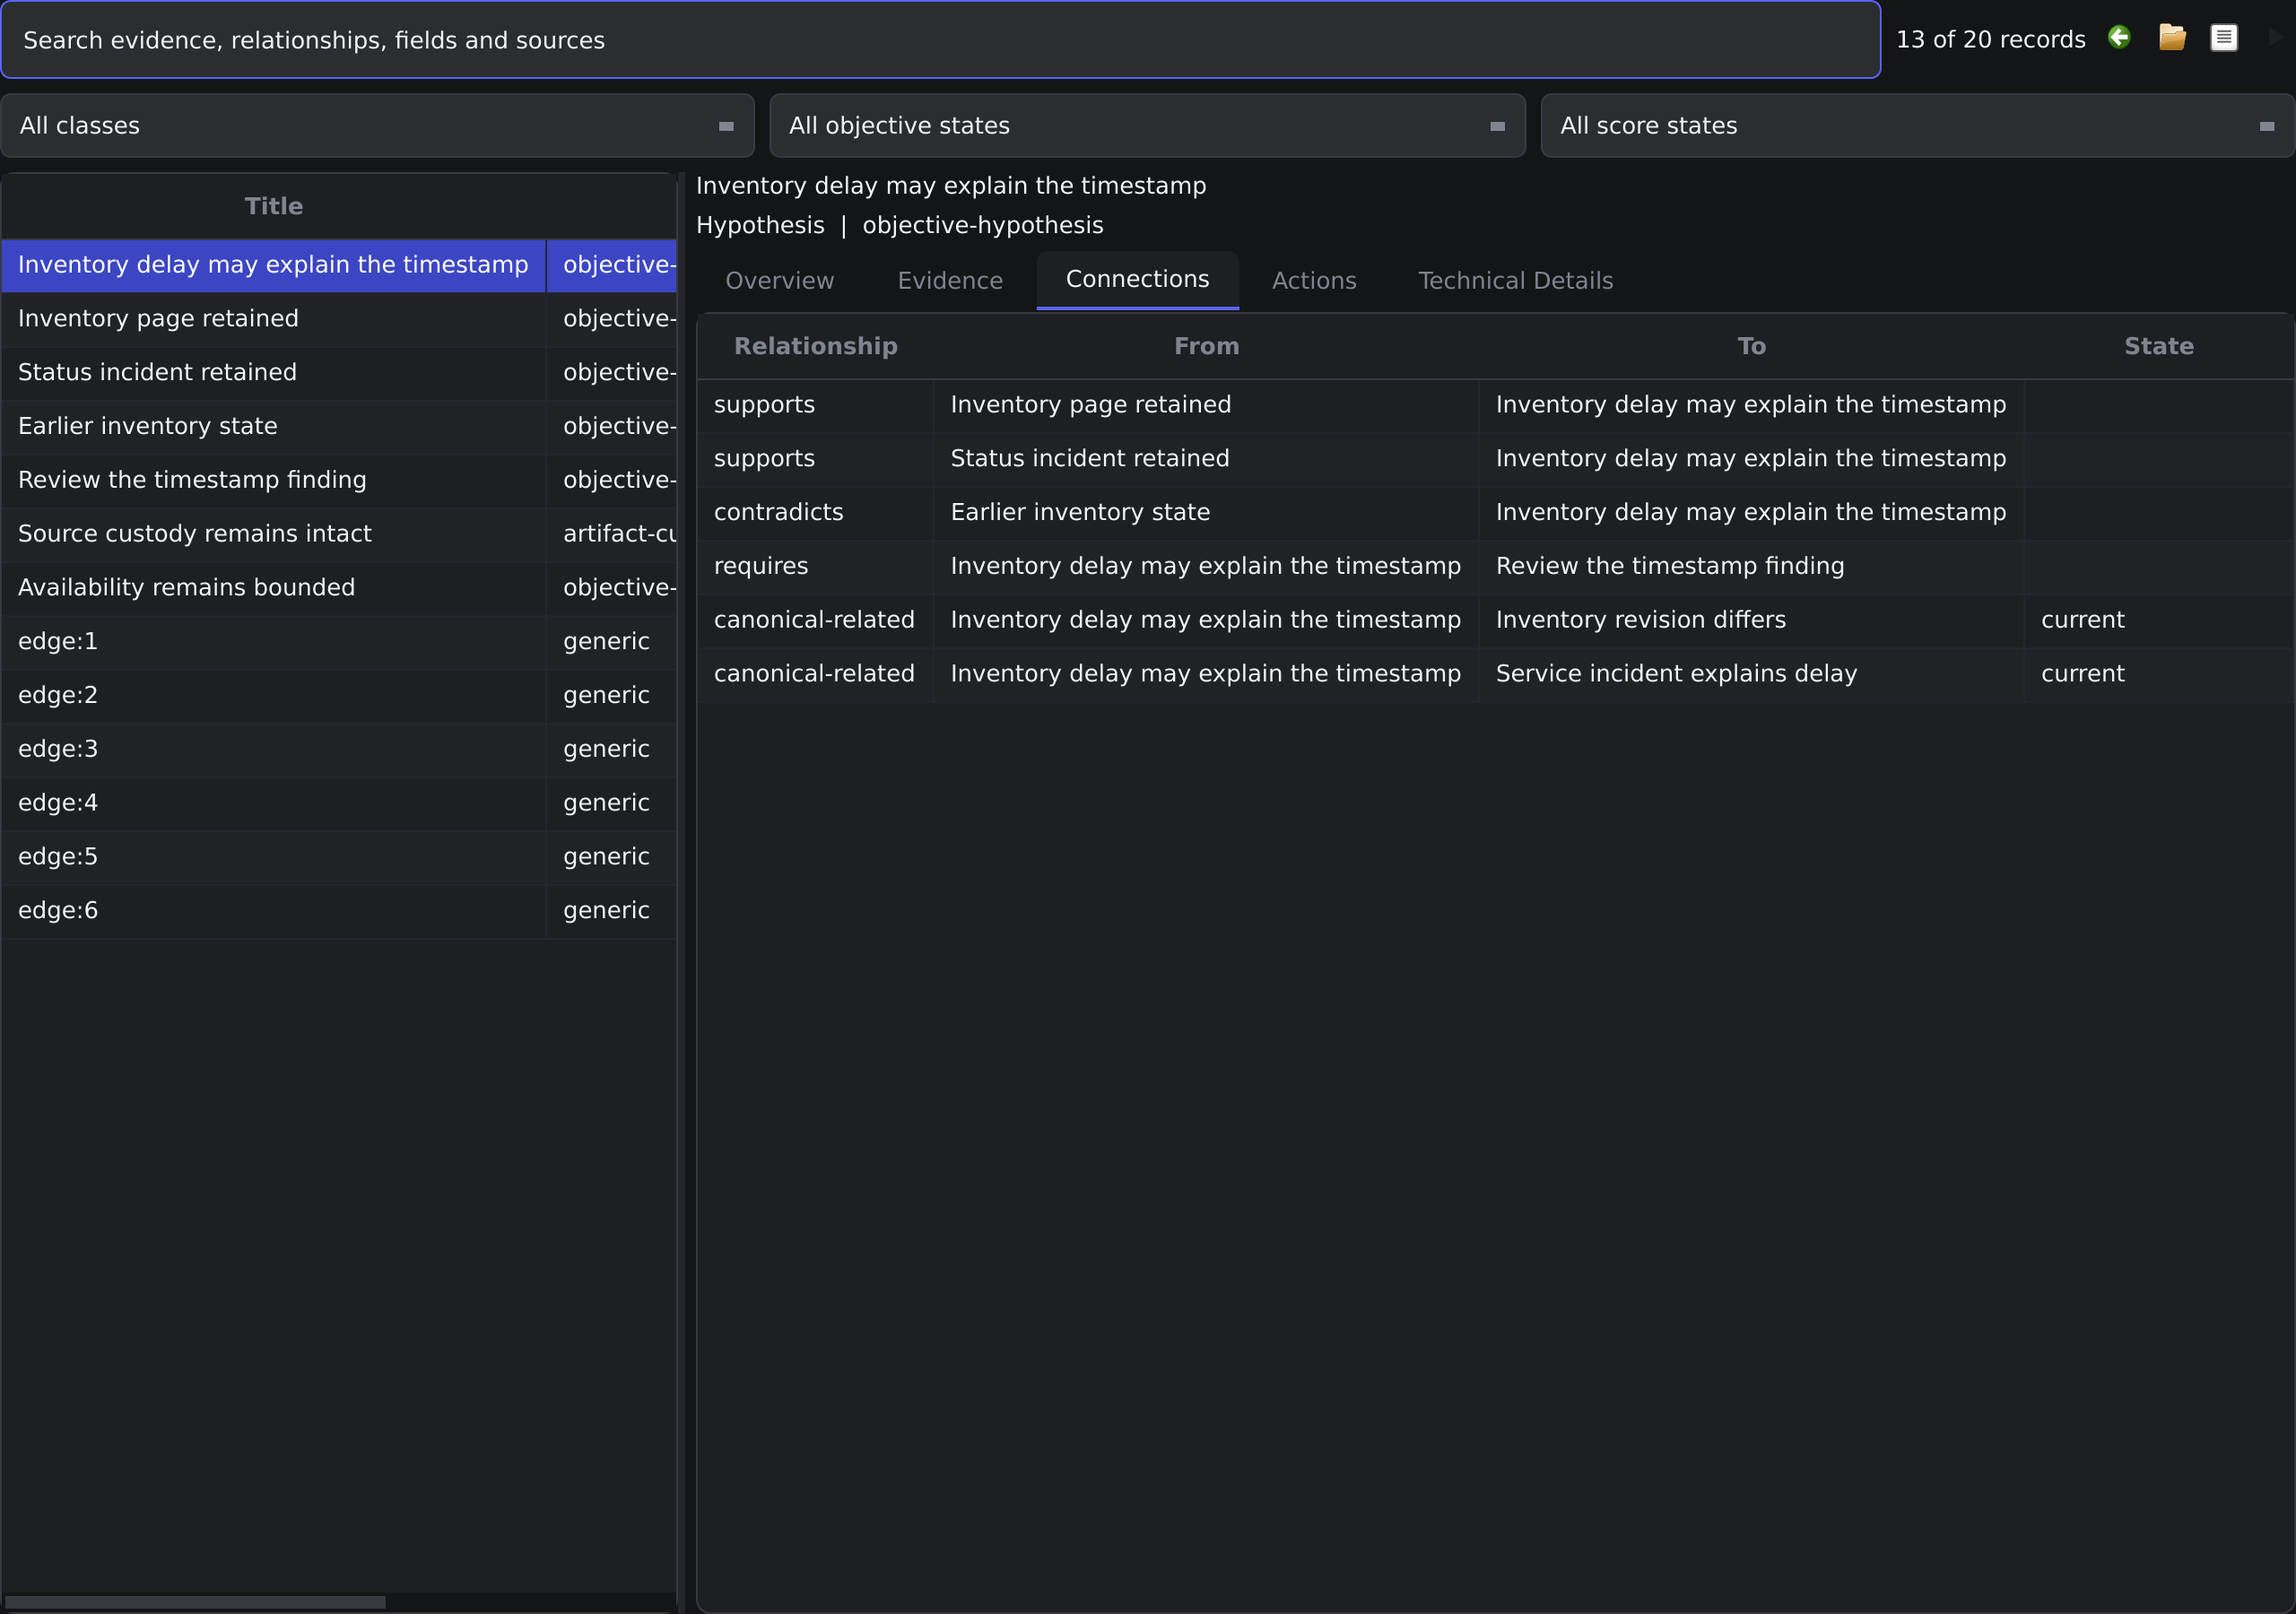
Interpretation and counter-evidenceCompare the current hypothesis with the earlier source revision.
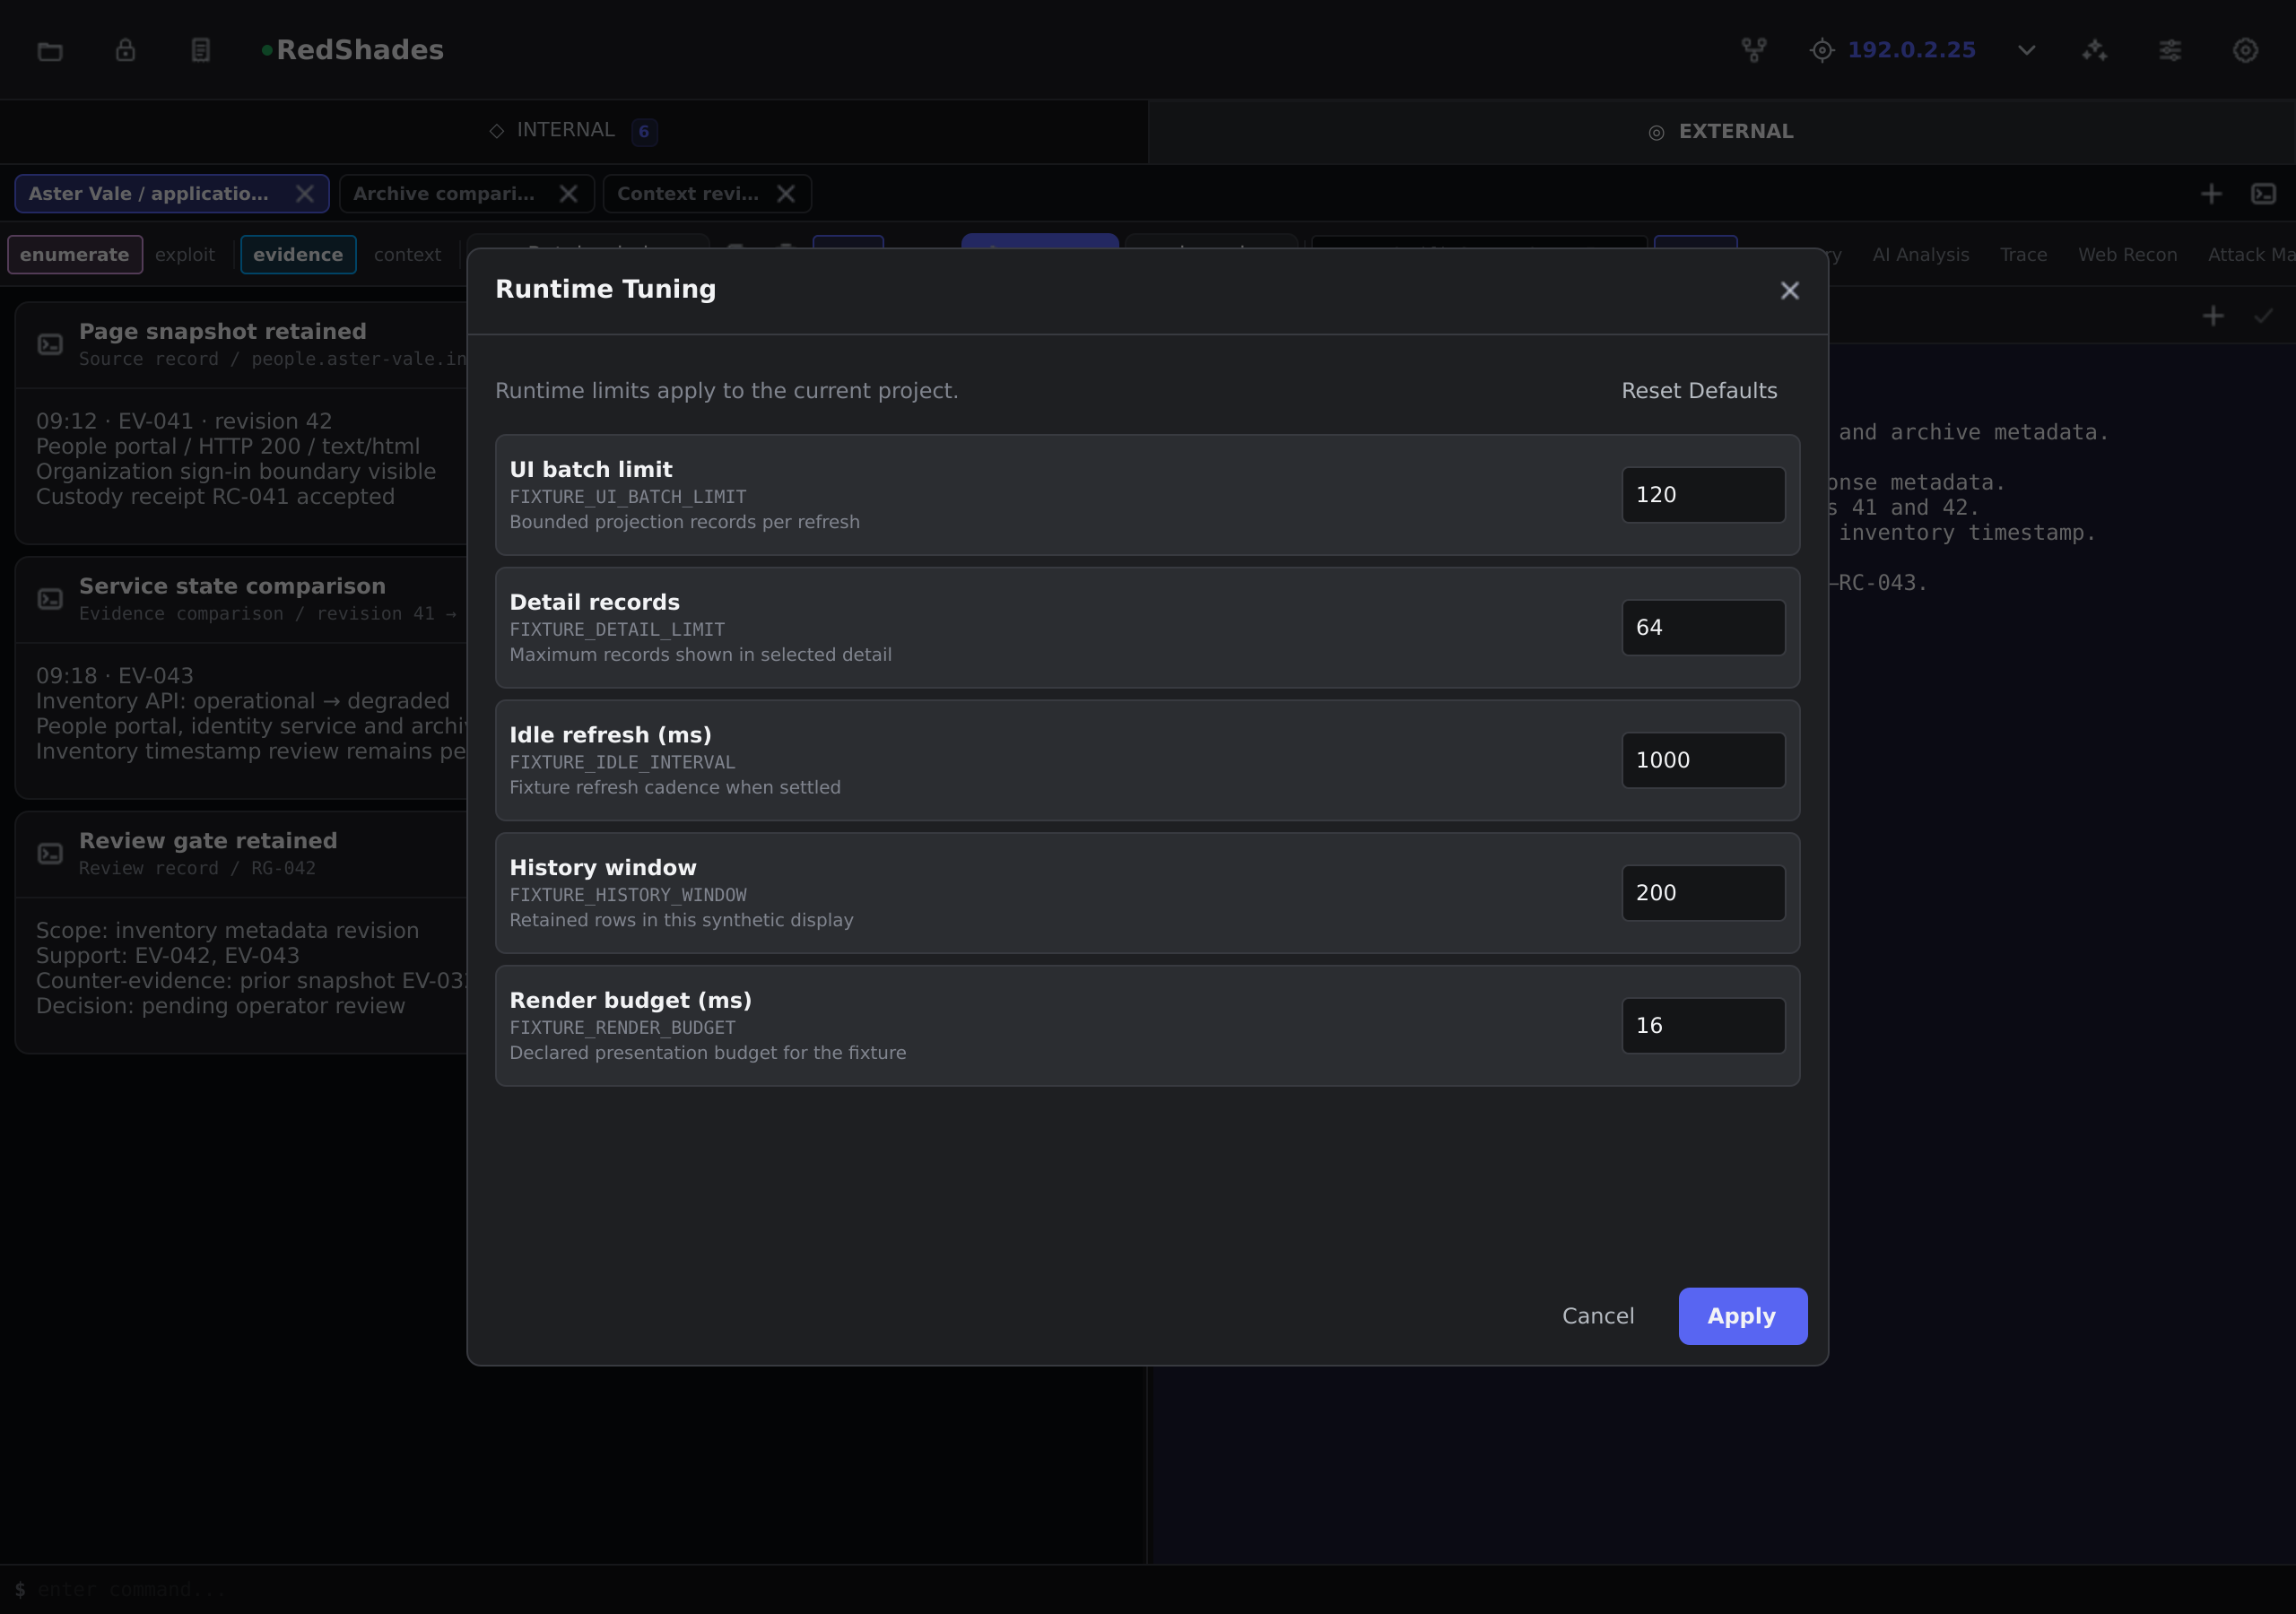
Runtime controls
Runtime controlsReview bounded display and runtime settings in the native workspace.
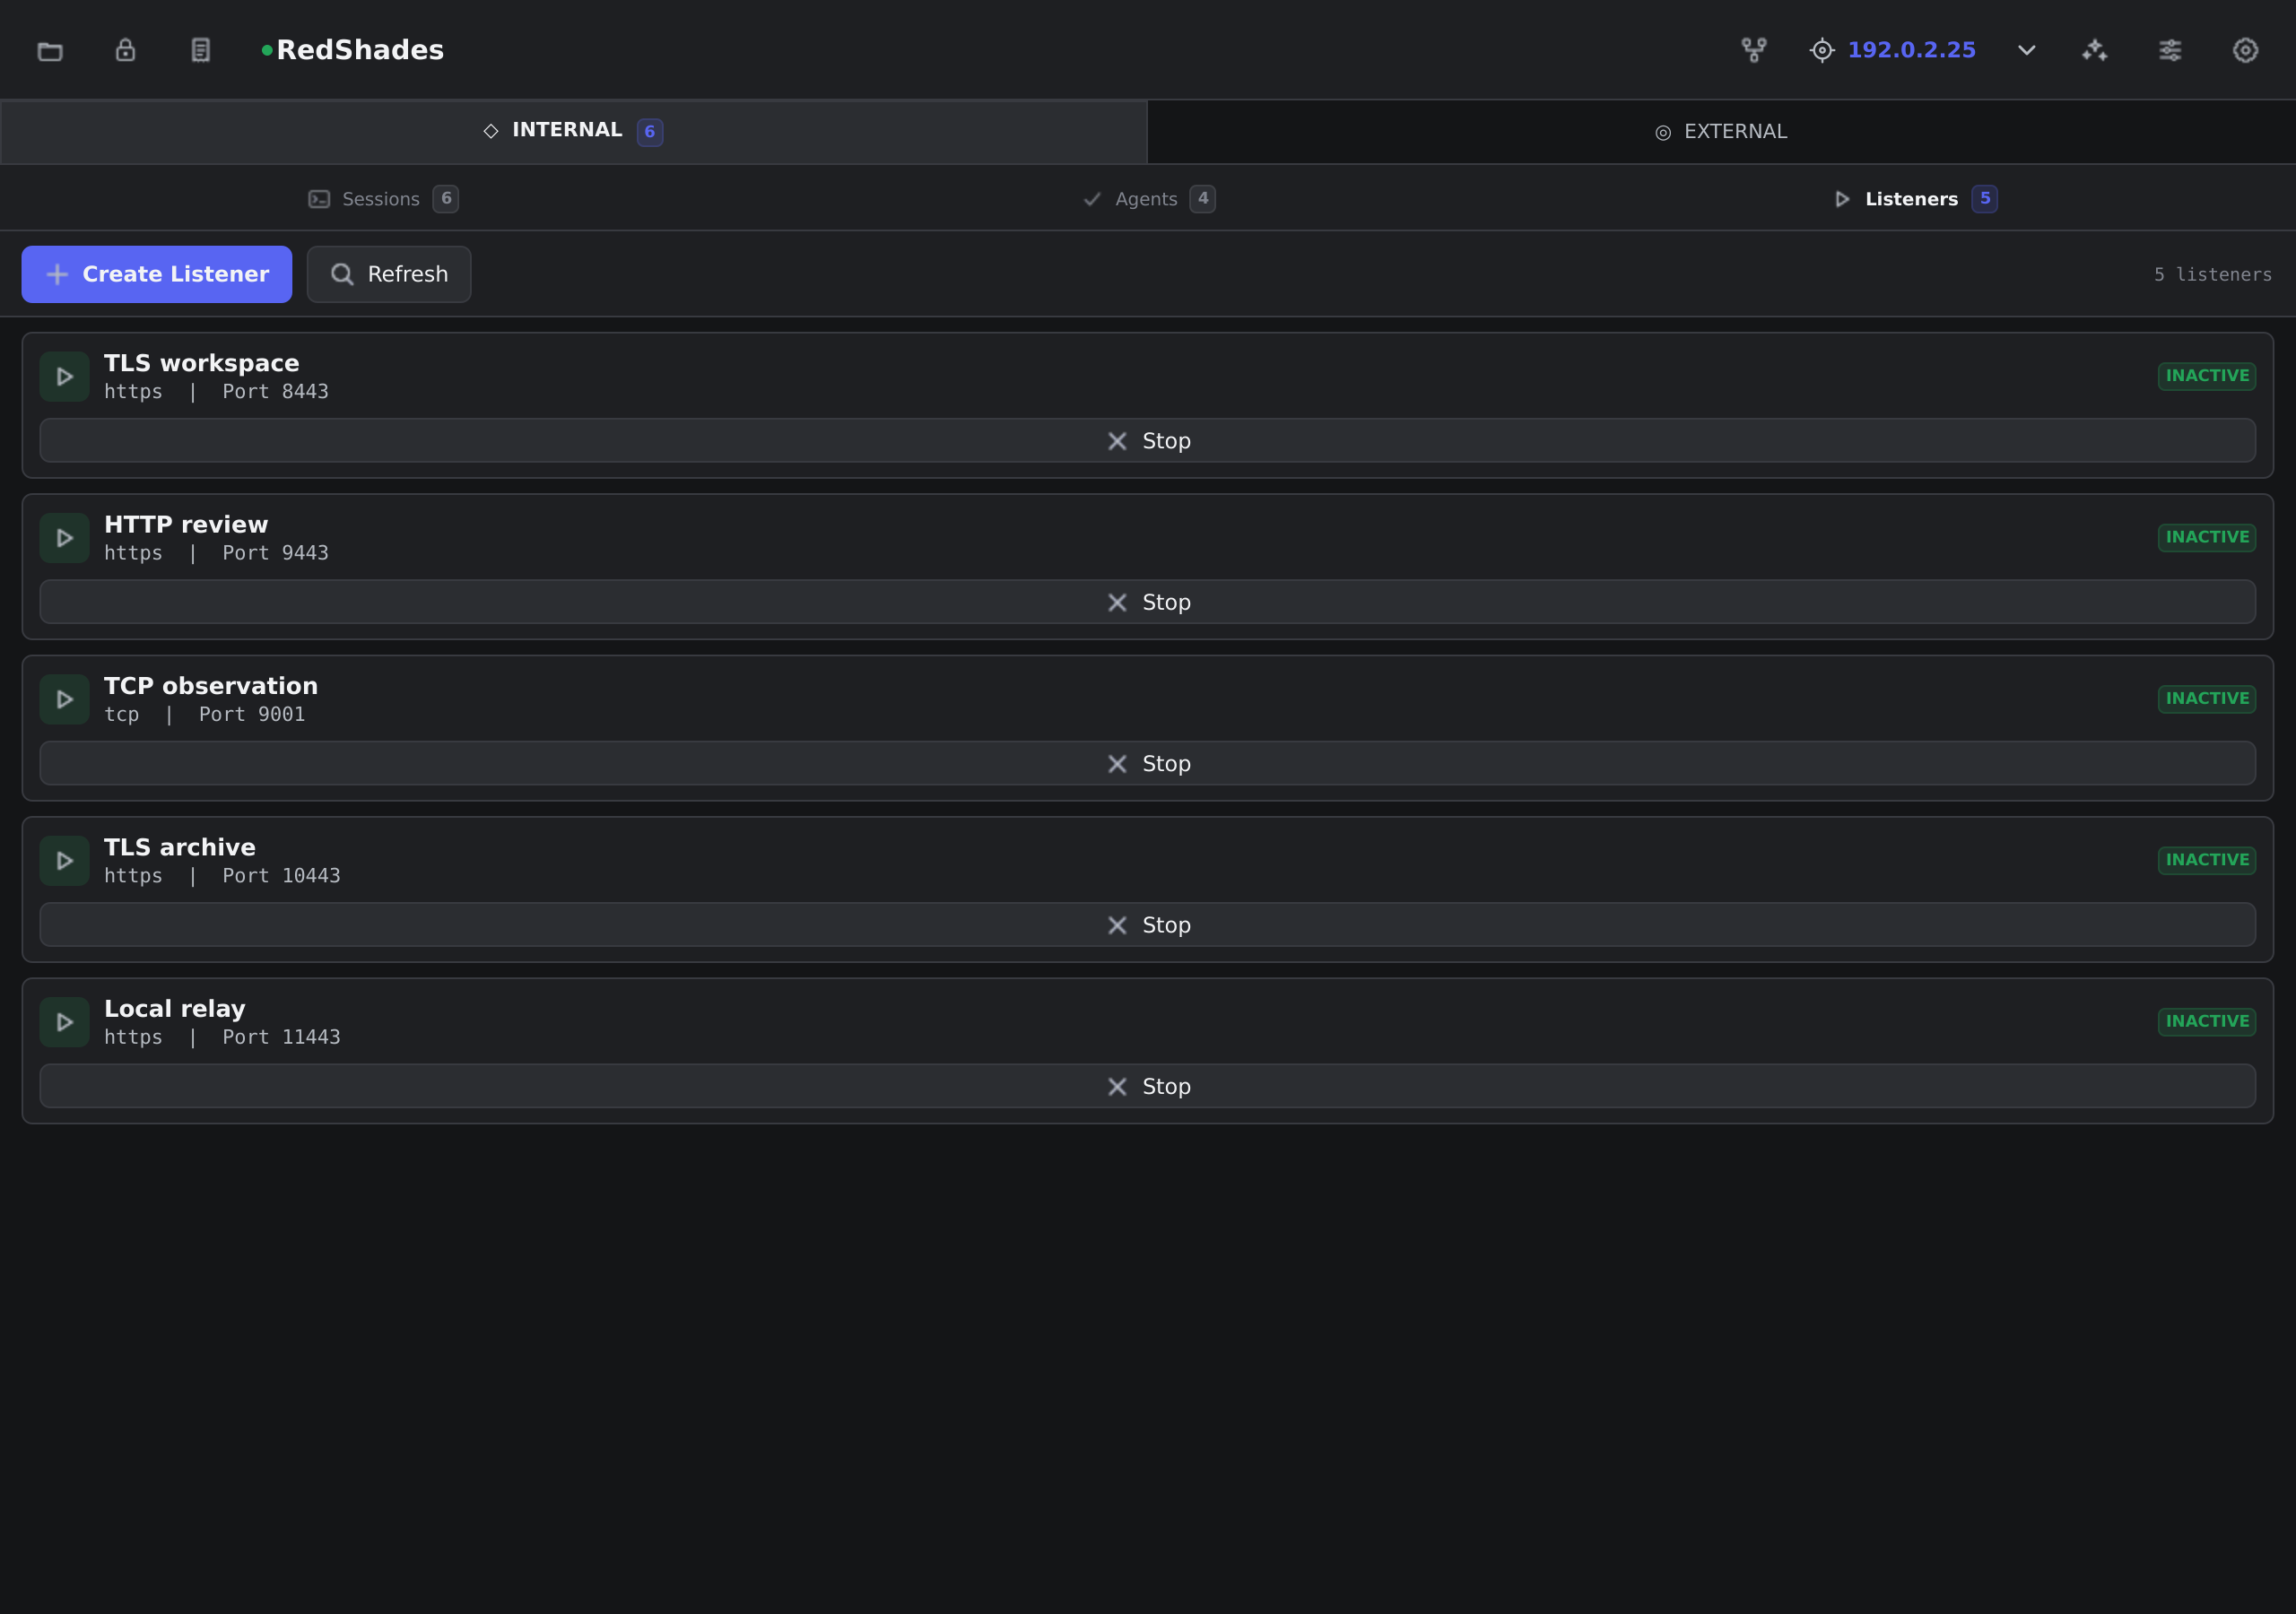
Listener inventory
Listener inventoryDistinguish recorded bindings from current availability.
Evidence relationships
Evidence relationshipsFollow support and counter-evidence from a selected record.
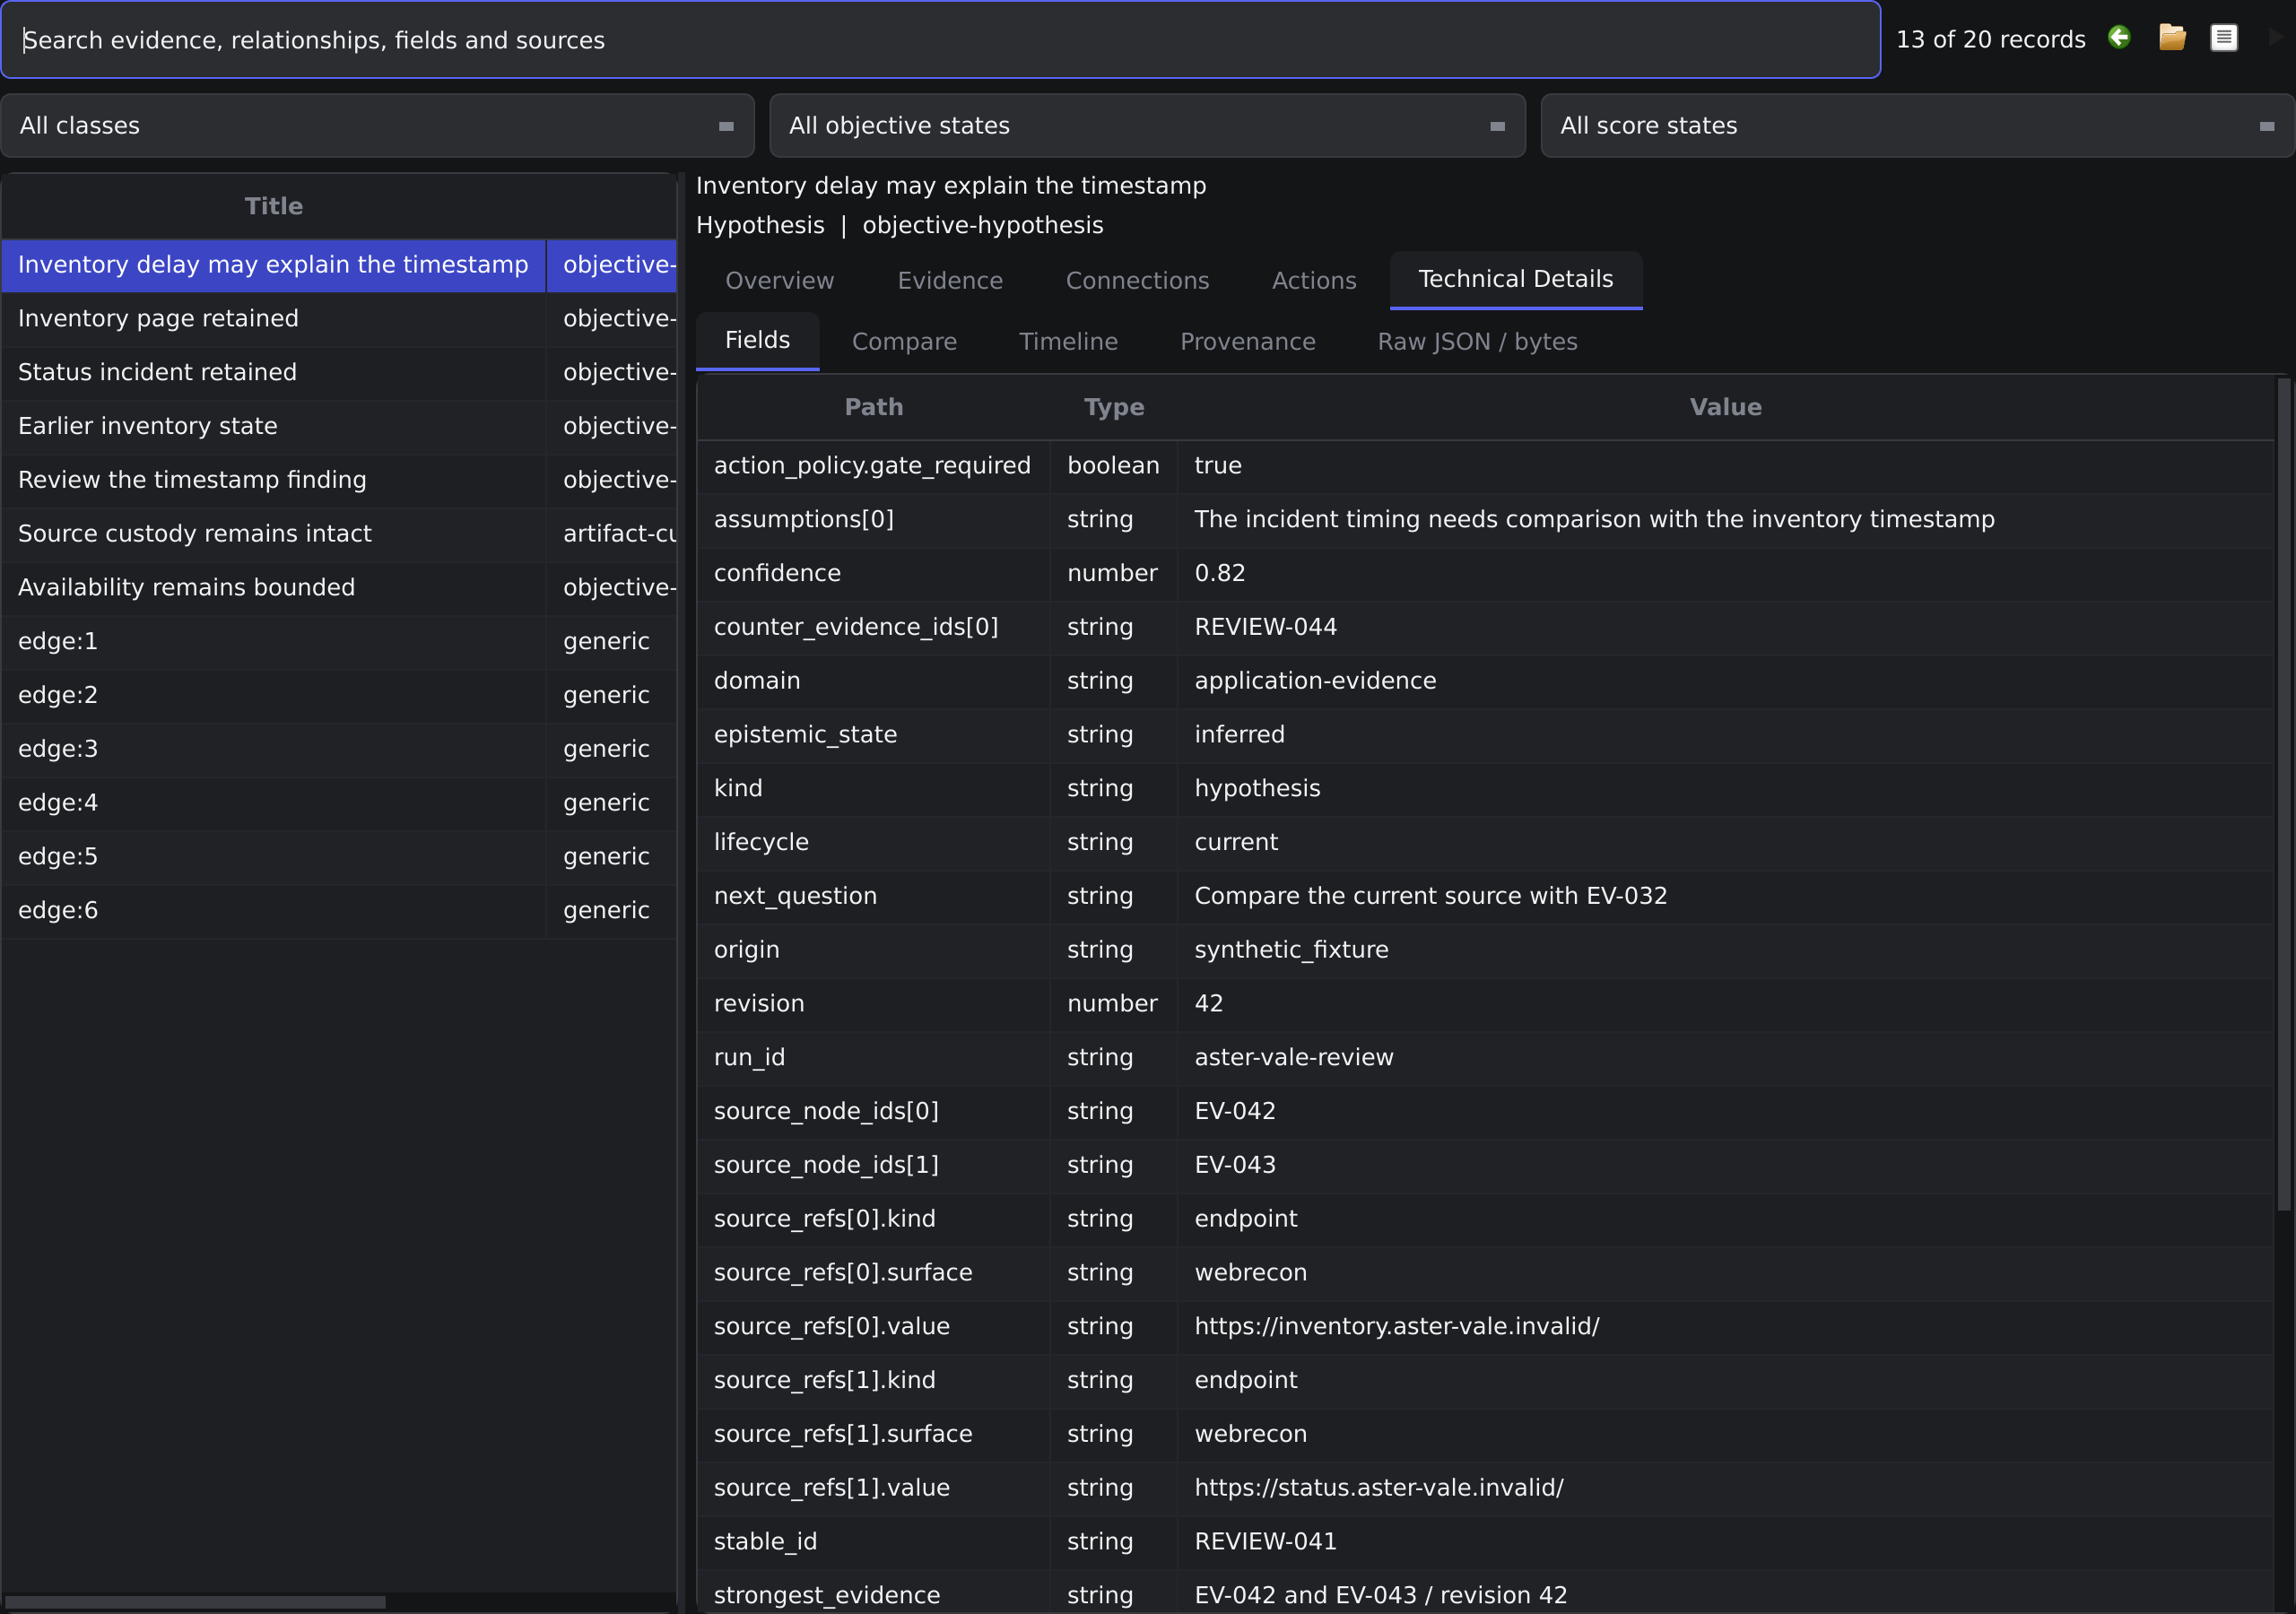
Technical record
Technical recordInspect the structured fields behind a finding.
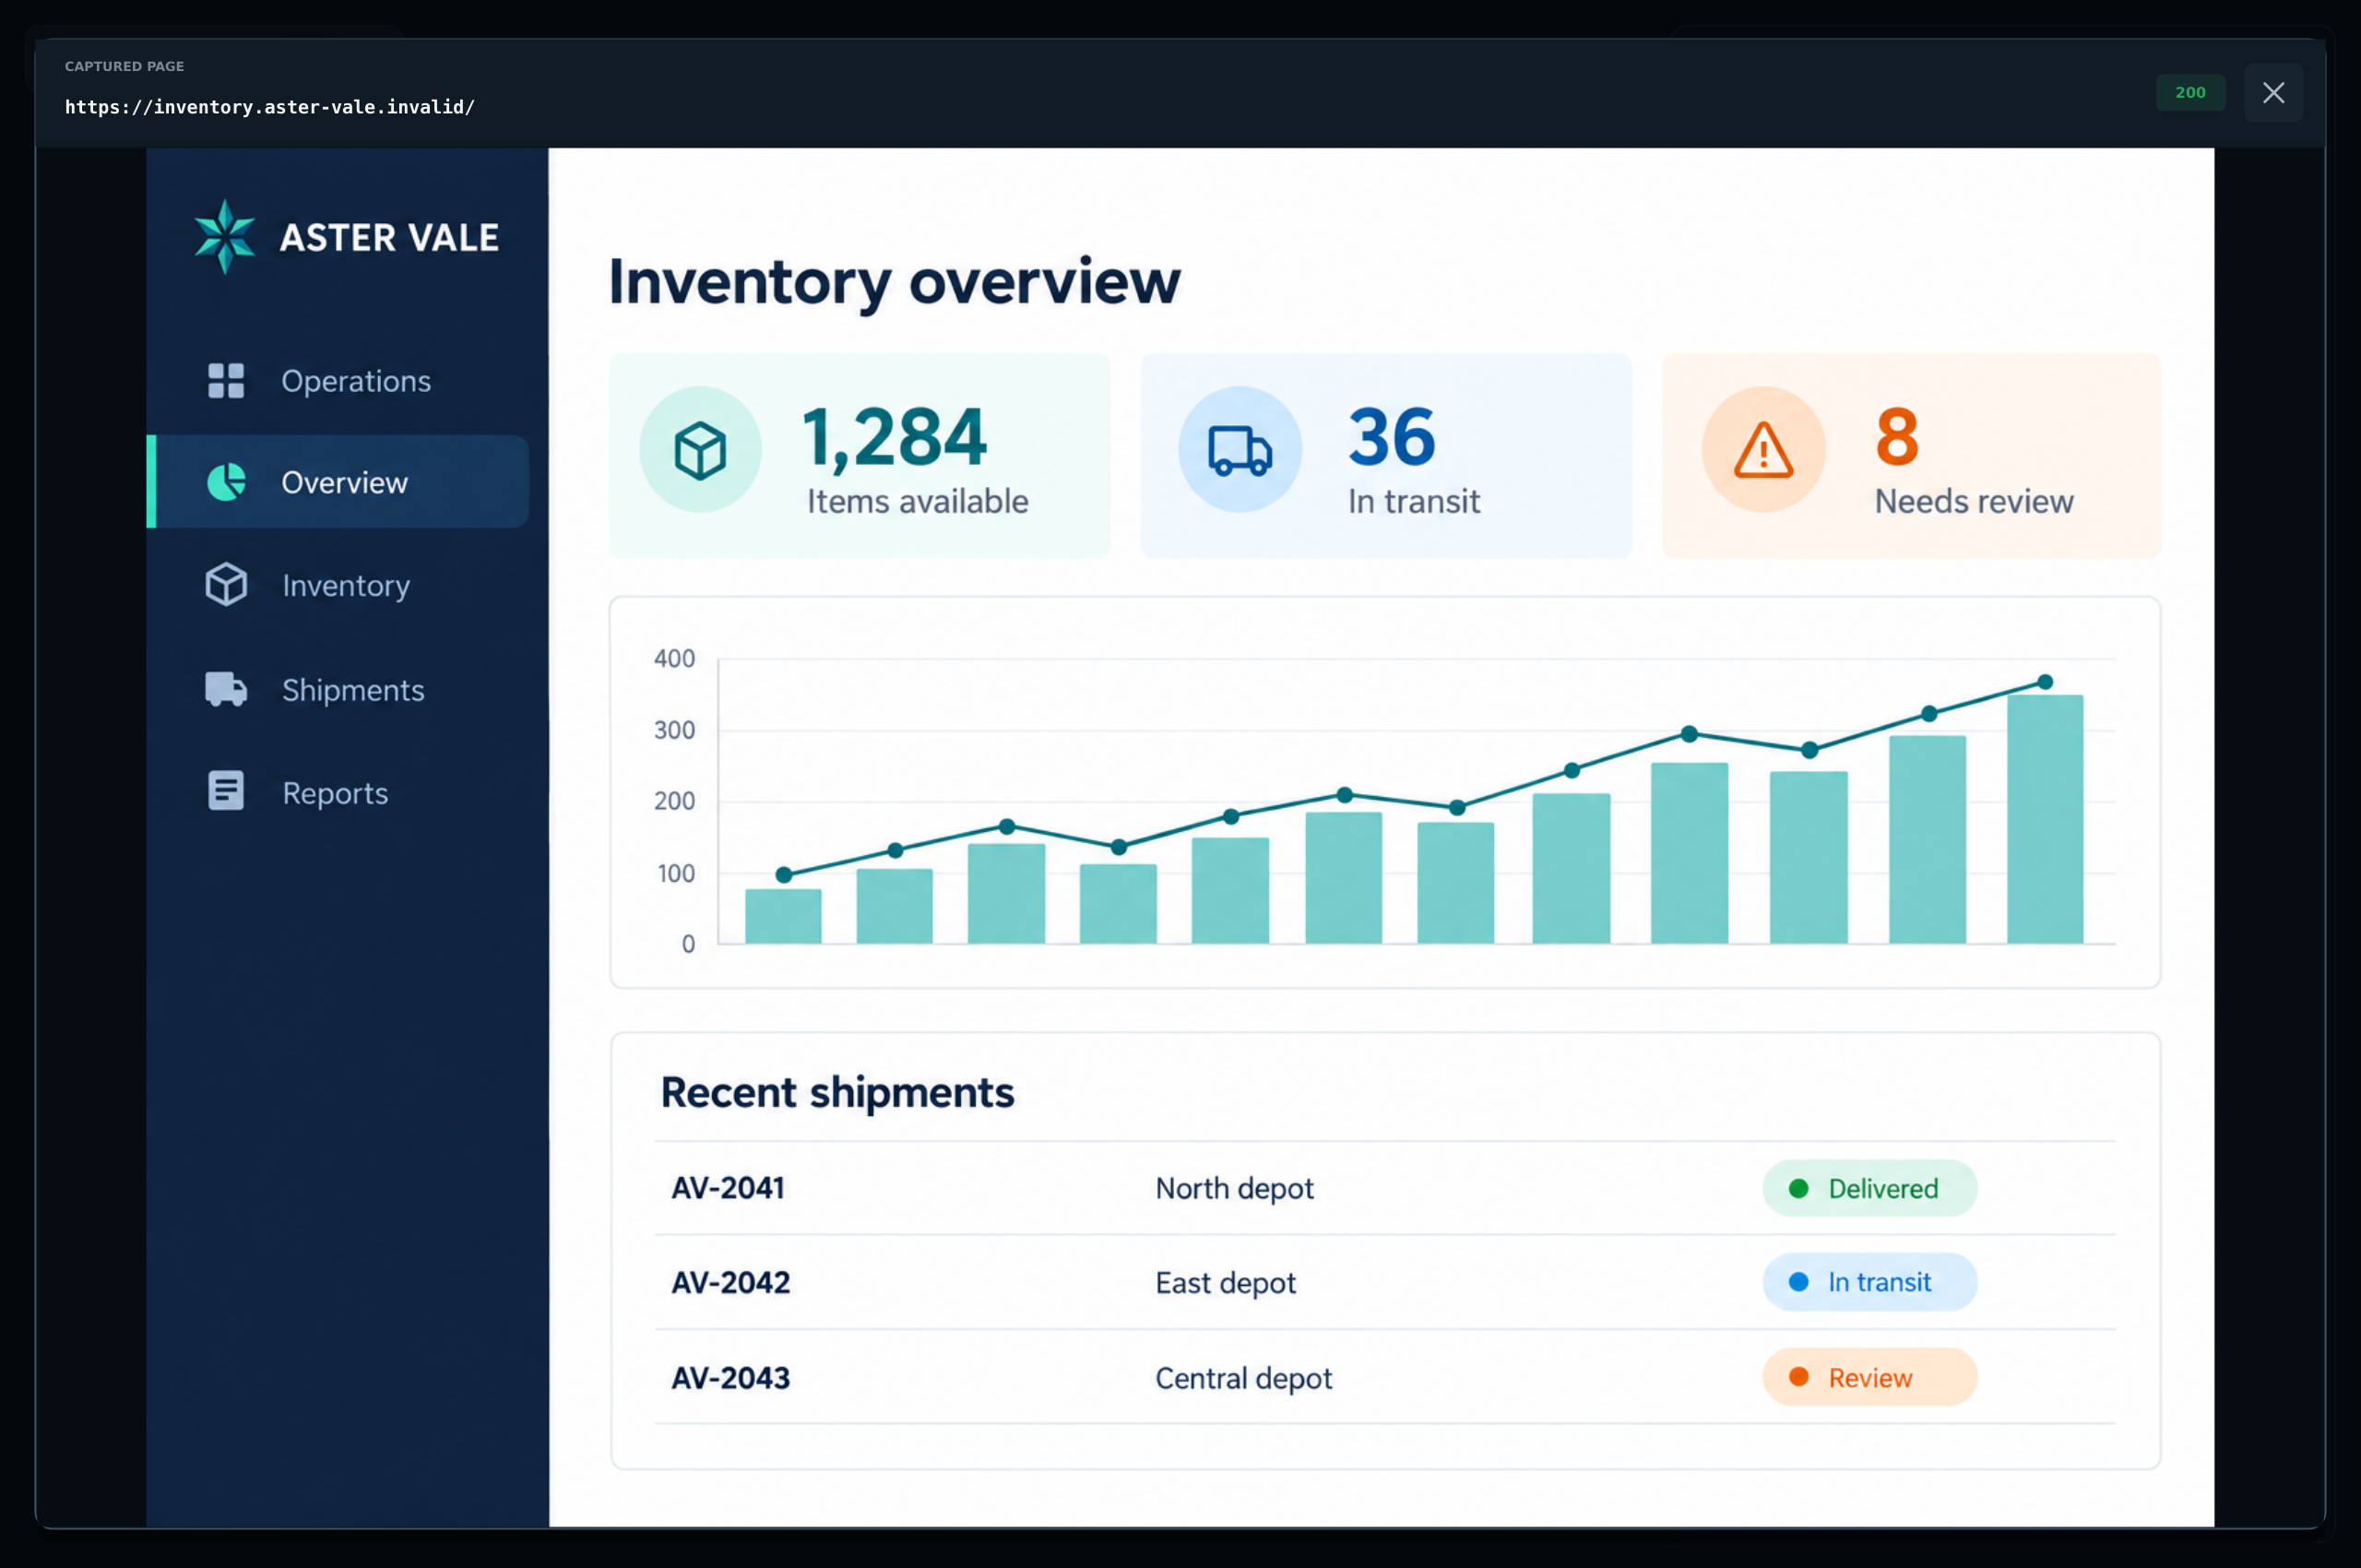
Read the retained page
Read the retained pageExpand a page image while preserving its evidence identity.
Source review
Source reviewExamine source observations alongside the review history.

Reading the evidence

Implementation, component tests, integrated evaluation and research studies establish different kinds of evidence. Section labels identify the scope of each claim.

Commercial entitlements describe the offering. Implementation, research studies and CTF evaluation retain their separate evidence labels.

Download the printable publication ↓